Verdict
The site blocked our scan, so nothing was confirmed either way. Treat it as unknown and verify who runs it another way.
usdt-aml.net blocked our automated scan and could not be verified.
- Needs Review: The site blocked or cut short the capture, so no verdict was reached.
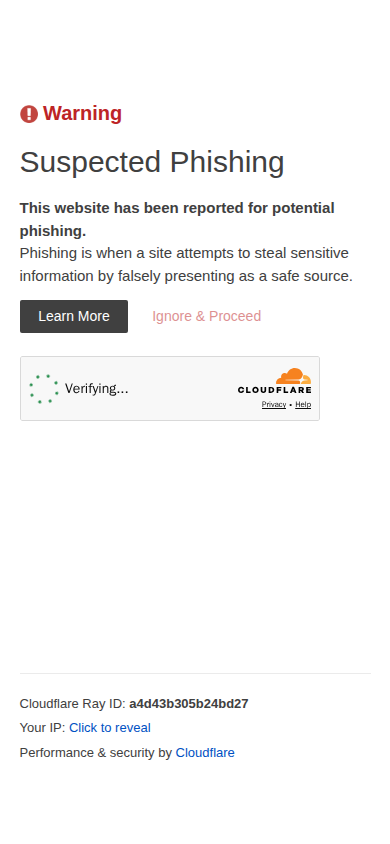
| How the site describes itself | Cloudflare security interstitial stating the requested website has been reported for potential phishing, with an option to ignore the warning and proceed. The underlying destination's content is not present in the captured HTML, so its purpose and trustworthiness cannot be verified. |
|---|
Evidence status and limitations
Evidence completeness: IncompleteThis says whether every check on the site was recorded as finished. The site blocked or cut short our capture, so the result needs review.
- Capture was incomplete or blocked; this result requires review.
- The real-world operator identity was not independently verified.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 2 months oldRegistered 2026-08-21 | Risk |
| Web archive | Archived since 20251 snapshot; the history predates the current registration (2026-08-21); an earlier owner may have held the name | Noted |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- The site blocked automated access, so TrustSniffer could not collect enough evidence to assign a score.
Full analysis
Overview
This website, which presents as usdt-aml.net, currently shows visitors a Cloudflare security interstitial titled "Suspected Phishing" instead of any site content. The warning says the requested website has been reported for potential phishing and offers an "Ignore & Proceed" option. The captured page shows no products, pricing, forms, or described service. The destination's purpose and business model therefore cannot be determined from what a visitor sees. The domain name suggests a stablecoin or compliance-screening theme, but the page contains nothing to support or contradict that.
Scam/Impersonation Risk
No contradictions were observed. No confirmed threat-feed listing, brand impersonation, or conflicting legal identities was found, and the page contains no login form, hidden form, or wallet-connection behaviour. Several adverse indicators are visible, and each is a soft signal with a stated discount reason.
- The interstitial states that the site has been reported for potential phishing. This is a soft third-party warning, not a confirmed finding. The page does not say who made the report, and the content behind the warning was not captured, so its accuracy cannot be tested. This is why the signal is discounted but not dismissed.
- One reputation engine rated the domain "suspicious". This is a soft reputation note from a single source. No engine rated the domain malicious, and no major threat feed lists it, so it carries limited weight on its own.
- Browser-behaviour testing found that most outbound requests (almost all by share) went to external hosts. None went to non-whitelisted destinations, and no wallet-drainer, clipboard-hijack, or fingerprinting activity appeared. The external share is unusual for a page that shows no content. It is not linked to any harmful destination or behaviour, so it is treated as an observation rather than a finding.
- Testing also recorded a sizeable number of console errors and a large page-structure change after interaction. It flagged a mismatch between the requested and final destination. These are consistent with the interstitial replacing the intended page, and none is attributed to malicious activity, so they are discounted.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Homepage: a "Suspected Phishing" interstitial reports the site for potential phishing and offers an option to ignore the warning. No destination content is shown.
- Domain provenance: the WHOIS record shows a creation date of 2026-08-21 (about 0.16 years). Registration continuity puts the domain's age at about 1.6 years, and the web archive holds 1 snapshot, dated 2025-03-04 (1 year tracked).
- Homepage behaviour testing across 3 successful runs: 97.1% of requests went to external hosts (56 external XHR/fetch calls, 9 external POSTs), with 16 console errors and no non-whitelisted destinations.An XHR request is a request the page sends in the background while it is open, to load or send data without reloading. "External" means it went to a different website than the one you opened.
- Reputation checks: 0 malicious and 1 suspicious detection (58 harmless, 33 undetected), no browsing-safety flag, and 0 abuse reports for the hosting address.
Regulatory Verification Notes
The captured homepage is a security warning, so no terms, privacy policy, about page, legal-entity name, licence, or registration number was available to assess. Any regulated activity would require its own verification. No broker-reputation match exists for this domain, so no third-party regulatory or reputational signal can be cited beyond the phishing warning and the single "suspicious" rating described above. The technical baseline is orderly: transport encryption is valid, the certificate is from a recognised issuer, and the domain is registered through a mainstream corporate registrar. These are basic hygiene facts. They do not establish who operates the site or what it does, and the operator's real-world identity remains unverified.
- Transport encryption: TLS certificate issued by WE1 (domain-validated, DV), valid to 2027-01-17 (89 days remaining).
- Registration: registrar is Tucows, with expiry on 2027-08-21 and registrant details redacted in the public record.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Captured homepage: no legal entity, licence, or contact details appear.
What to Verify Next
The first step is to establish why the warning was raised and what the destination actually serves. This means obtaining the real page content through an isolated, non-credentialed environment, or from whoever supplied the link, and not by clicking through the interstitial on a personal device. If the destination claims to offer anti-money-laundering, compliance, or stablecoin services, its operator, legal entity, and any licence should be confirmed against the relevant public registry. Official support and contact channels should be confirmed through an independent route, such as a known corporate directory, and not through details supplied by the site itself. Any wallet-connection or payment prompt that appears after proceeding should be treated as unvetted until these checks are complete.
- Homepage: the interstitial's "Ignore & Proceed" control is the only way past the warning, and nothing behind it was captured.
- Homepage: no company name, product description, or service claim is visible to anchor an identity check.
- Domain history: the web archive has a single snapshot, so there is no prior content record to compare against.
Summary Verdict
The available evidence supports an unverified, needs-review posture. No contradictions were found, and no confirmed malicious activity or impersonation was identified. The site's purpose and operator cannot be established, and an unresolved third-party phishing warning remains. That warning is soft and unconfirmed, but it outweighs the clean technical hygiene. Legitimacy therefore cannot be inferred, and the evidence is consistent with an unknown entity rather than a verified one. The posture is neutral-to-cautious, not condemnatory, pending clarification of what the destination serves.
Infrastructure Integrity
The site is fronted by Cloudflare's CDN and web application firewall, and all four observed IP addresses are edge servers. The origin server was not observable, so hosting cannot be verified independently. This arrangement is a mitigating factor only. It does not offset the phishing warning, and edge-only visibility makes it harder to detect rapid changes to the underlying content. A heuristic flagged a young domain with sparse subdomains. It is unconfirmed and carries limited weight on its own.
Closing Assessment
Verification should come first. Credential entry, payments, and crypto transfers should wait until the cause of the warning is explained and the operator's identity is independently confirmed.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by page content, hosting and network, behaviour in a sandbox, and registration and ownership.
01 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
02 Hosting and network
- The domain is young and has almost nothing else set up around it.Hosting and network
rule:DNS_SPARSE_YOUNG_DOMAIN
03 Behaviour in a sandbox
- Most of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH
04 Registration and ownership
- The registration record withholds contact details for the operator.Registration and ownership
rule:KF_WHOIS_HIDDEN
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of usdt-aml.net.
- The request stayed on usdt-aml.net. It was not redirected to another domain. Clear
- Registered through TUCOWS.COM, CO. Noted
- DNS for this domain is served by ns.cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-08-21. Noted
- The earliest public archive of this name is from 2025-03-04, before the current registration on 2026-08-21; an earlier owner may have held it. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | TUCOWS.COM, CO. |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3033::ac43:cf96 (a CDN edge address; the server behind it was not observed) |
| Name servers | ullis.ns.cloudflare.com, vicente.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-17 |
| Domain age | 60 days (registered 2026-08-21) |
| Domain expiry | 2027-08-21 |
| Archive first seen | 2025-03-04 (1.6 years before capture) |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
The web archive has records of this name from 2025-03-04, before the current registration on 2026-08-21. That archive history predates the current registration, and an earlier owner may have held the name.
About this assessment
A trust score summarises the evidence TrustSniffer could collect about usdt-aml.net at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.