Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
xsjiamei.com shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 6 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 3 months oldMost scam domains are under a year old | Risk |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
| Hosted by | PLI-ASServer in PA | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
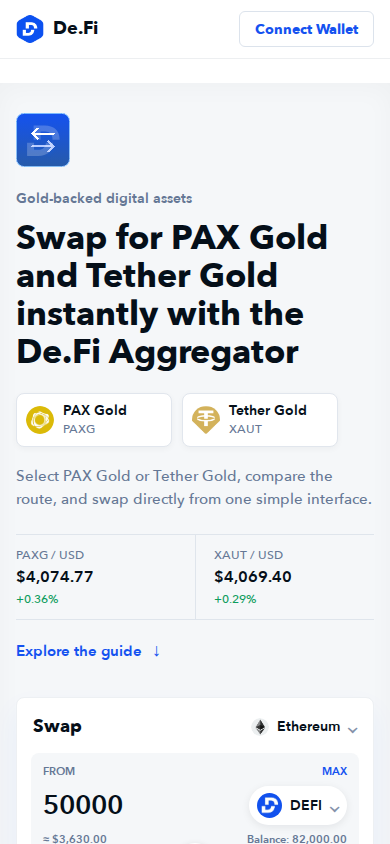
This website is a single-page storefront whose page title reads "Buy Gold Tokens | De.Fi". It presents a short, text-based offer to purchase gold-linked digital tokens and appears to operate as a token-sales or crypto-asset promotion front. The title uses the name of a recognizable decentralized-finance brand, but nothing collected independently connects the site to that brand or to any identified operator.
Scam/Impersonation Risk
Contradictory signals are present and are decisive. Two major security vendors currently flag the domain as malicious, and a number of other engines return malicious or suspicious detections. The domain is blacklisted by external threat-intelligence sources, and its reputation record also carries a prior phishing association. No conflicting legal entities were found, and the collected page content shows no confirmed on-page impersonation. The reputational detections nonetheless stand on their own as a serious warning. The domain is also only a few months old. This matters because the offer is a token purchase, where a payment is hard to reverse. The title's borrowed DeFi branding sits uneasily beside a fresh domain with no history and a hostile reputation record. In browser sessions the site served pages reliably and showed no wallet-draining, clipboard-hijacking, hidden-form or cloaking behavior. It did, however, make background requests to three external hosts outside the expected set of well-known services, and external sources accounted for a very large share of its traffic in at least one session. This is a modest behavioral concern and does not offset the reputation findings. Evidence:
- Domain registered 2026-07-30 (~0.23 years old, roughly 83 days), expiring 2027-07-30, so the domain is very young.
- Homepage: title "Buy Gold Tokens | De.Fi" with about 4,200 characters of text and no identifiable operator.
- Homepage behavior sandbox, three runs: three non-whitelisted external XHR calls, external traffic up to 84.1% in one session, no wallet-connect, drainer, clipboard or cloaking activity.
- Reputation checks: six malicious and one suspicious detection from security engines, including two top-tier vendors.
Regulatory Verification Notes
The collected content gives no confirmable evidence of licensing, registration or a named legal entity behind the token offer. The page's disclosure position could not be established. A real-world operator identity has not been independently verified, so no legitimacy should be inferred from the site's presentation. A third-party broker-reputation lookup returned no match. This is a neutral contextual signal and not a regulatory finding. Financial-style offerings of this kind would normally be expected to identify a regulated issuer or seller. The security reputation findings above, not this transparency point, drive the cautionary posture. Evidence:
- Registrar: Dynadot, with registrant details held behind its privacy service.
- Hosted on AS51852 (Private Layer INC), registry LACNIC, country Panama.
- TLS certificate issued by YR1 (Domain Validated), valid to 2027-01-05. This confirms only encryption and domain control, not operator identity.
- Homepage: no regulator, license number or corporate registration identified in the collected content.
What to Verify Next
Any dealings should stay at read-only viewing until the operator is identified. If the offer is of real interest, the claimed seller should be identified and confirmed through a regulator's public register, not through details on the site. The site should not be treated as the official channel of any brand named in its title unless that brand confirms it through its own independently known contact route. Payment cards, wallets and credentials should not be used on the site until a reputable third party has reviewed the domain and the listings have been cleared. Anyone responsible for the site who believes the listings are mistaken should seek delisting through the relevant vendors. Evidence:
- Homepage title referencing a DeFi brand: confirm with that brand directly through channels known independently of this site.
- Homepage token-purchase offer: no named seller or registry entry available to check.
- Current malicious detections: re-check reputation status before any reconsideration.
Summary Verdict
The site carries a critical risk posture. Confirmed external threat detections outweigh every technical positive and decide the assessment. The evidence points to a very new, anonymous, unverified operation. It is not suitable for login, credential entry or financial transactions.
Infrastructure Integrity
The site runs on a commodity data-center hosting provider with no content-delivery network or web application firewall in front of it. Several addresses appear to point directly at origin servers, so there is no protective layer to mitigate exposure. Unconfirmed heuristics note a mismatch between the hosting registry region and the country, a fragmented address footprint, and the thin subdomain structure typical of a new domain. These are weak indicators. The valid encryption certificate and a stable hosting response are the only mitigating points, and they do not offset the reputation findings.
Closing Assessment
Users should limit themselves to viewing the page and should not enter credentials, connect wallets or make payments. Anyone who has already interacted with the site should review account and wallet activity and rotate any shared credentials.
Written analysis generated 2026-10-22 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, hosting and network, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH
03 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D - The hosting and network setup shows a moderate level of risk indicators.Hosting and network
rule:DNS_RISK_MED
04 Registration and ownership
- The registration record withholds contact details for the operator.Registration and ownership
rule:KF_WHOIS_HIDDEN - Registration details are held behind a privacy service, so no operator is named publicly. This is common and legal, and it also means there is nobody to check.Registration and ownership
rule:KF_WHOIS_PRIVATE
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 15% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of xsjiamei.com.
- The request stayed on xsjiamei.com. It was not redirected to another domain. Clear
- Registration is published under DYNADOT LLC. Clear
- DNS for this domain is served by dyna-ns.net, across 2 name servers. Noted
- The registration is paid up to 2027-07-30. Noted
- It is hosted on PLI-AS, from a server in PA. Noted
Domain intelligence
| Registrar | DYNADOT LLC |
|---|---|
| Hosting | PLI-AS - Private Layer INC, PA |
| Country | PA |
| Server IP | 179.43.182.131 |
| Name servers | NS1.DYNA-NS.NET, NS2.DYNA-NS.NET |
| CDN / edge network | Not detected |
| Resolved IP addresses | 4 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 3 |
| SSL issuer | YR1 |
| SSL expiry | 2027-01-05 |
| Domain age | 0.23 years (continuous registration) |
| Domain expiry | 2027-07-30 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 6 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about xsjiamei.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.