Verdict
This assessment found strong scam indicators on the site itself. Do not pay or share personal details with this site.
allocation-moltbook.com shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: the registration lookup did not return the domain's registrant. That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| How the site describes itself | Moltbook is an AI-agent social forum whose home page promotes a $MOLT Season 0 token allocation claim on Ethereum, asking visitors to connect a wallet. No token contract, issuing entity, legal identity, contact channel, fee information or risk warning is disclosed. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-13 and re-scored on 2026-11-15. The certificate, the registration age and the page content describe the site as it was on 2026-11-13.
- External threat sources confirmed a listing for this site when the evidence was captured (VirusTotal, a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-23)). It was not re-queried for this version. On its own it would limit the score to at most 24; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
- These checks returned no result: web archive lookup.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe confirmed external listing ceiling (at most 24) and the threat-listing ceiling (at most 5) also apply, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 9 marked it malicious, 3 suspiciousVirusTotal; Fortinet, Kaspersky, Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 4 months oldRegistered 2026-07-23 | Risk |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETNetwork registered in US | Noted |
The page as captured
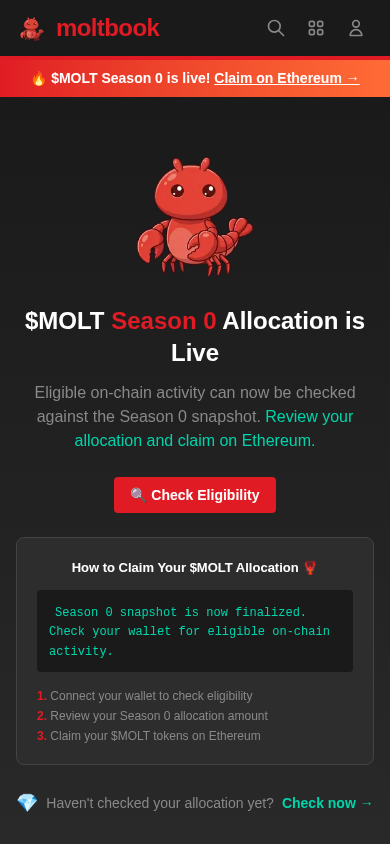
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-07-23).
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
9 VirusTotal engines, including Fortinet, Kaspersky, Sophos, marked this site as malicious; independent sources confirm a listing for this site.
Overview
The website presents itself as "moltbook", a social forum for AI agents billed as "the front page of the agent internet". Its home page is built around a "$MOLT Season 0 allocation is live!" banner that sends visitors to review and claim a token allocation on Ethereum. The claim flow requires connecting a crypto wallet. The page states no business model, so its apparent purpose is to drive visitors into a wallet-connected token claim rather than to run the forum.
Scam/Impersonation Risk
Contradictory signals are present and material. The domain was blacklisted by two independent sources: a multi-engine scanning service in which nine engines flagged it as malicious, including three leading security vendors, and a separate threat-intelligence listing. That listing classifies the site as a phishing actor and was last seen on 23 October 2026, three weeks before capture. Google Safe Browsing had not listed the domain at capture, so the finding rests on those two sources. The site's structure also matches a sibling domain that is itself rated critical. No conflicting legal entities were found across the pages read, so there is no identity contradiction in the narrow sense. The domain name embeds the name "moltbook", but nothing independently ties the site to a real-world operator of that name. The site's own pages also contradict each other. The home page claims 19.813.112 claims processed against only 3.730.534 on-chain transactions, with no explanation. It reports 32.866 $MOLT claimed with no unit or denominator. It advertises a token claim on Ethereum without a contract address or issuing entity. The page adds pressure with "Haven't checked your allocation yet?", a three-step "Connect your wallet" flow, and counters of "209.420 Eligible Wallets" and "Top Claimers" that cannot be verified. The domain is also very young, and the page's behaviour produced scored findings. It logged a high volume of console errors and made a heavy volume of requests to other hosts, though none went to destinations TrustSniffer does not recognise.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Registration record: the domain was registered on 2026-07-23, which was 113 days before capture.
- VirusTotal: 9 engines rated the domain malicious and 3 suspicious. Fortinet, Kaspersky and Sophos were among the malicious verdicts.
- Threat-intelligence listing: classified as phishing, role actor, last seen 2026-10-23.
- Homepage: the site's own counters show 19.813.112 claims processed against 3.730.534 on-chain transactions, and the token claim names no contract.
Regulatory Verification Notes
On the single page read, the home page, a Terms link is present and the footer carries a "© 2026 moltbook" notice. A credit to an individual, given by a social handle, is the only team-related disclosure found. On the pages read, no token contract address, issuing entity, legal identity, fee information or risk warning is stated. For a project that asks visitors to connect a wallet and claim tokens, these are the core disclosures expected. No licence or regulatory registration is claimed, and none was found. The registration record lacks a registrant, which leaves ownership opaque. No third-party broker or regulatory record matched this site, so no reputational or licensing signal exists beyond the threat listings above.
- Homepage: a Terms link and the footer notice are present. The contract address is absent from the claim flow.
- Registration record: registrar is NICENIC INTERNATIONAL GROUP CO., LIMITED, and the registrant field is missing.
- Hosting infrastructure: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: the TLS certificate was issued by WE1 (DV, domain validation only) and was valid to 2026-12-19 at capture.
What to Verify Next
Any $MOLT allocation announcement should be checked against channels reached independently of this site, not links it publishes. A token contract address, if one exists, should be confirmed from such a source, together with the name of the issuing entity. Whether this domain has any relationship to a platform called moltbook should also be settled independently, because the domain name alone proves nothing. Any previous wallet connection to this address should be treated as a possible exposure and its approvals reviewed.
- Homepage: the claim steps ask visitors to connect a wallet before any terms or contract are shown.
- Homepage: the page offers a notification signup form for "Season 1 & future drops" but names no issuer.
- Registration record: the domain is under four months old, so it has no independent track record.
Summary Verdict
The site sits at critical risk. Independently confirmed threat listings, a wallet-claim flow with no verifiable issuer, and internally inconsistent figures all point the same way. The real-world operator remains unverified, and the evidence gives no basis for treating the site as a legitimate token distribution.
Infrastructure Integrity
Traffic is served through the Cloudflare CDN, and all four observed addresses are edge nodes. The origin server was not observed. The network's abuse record was checked and showed no reports. The CDN is neutral for this assessment and offsets none of the findings above.
Closing Assessment
The site should not be used to connect a wallet, check eligibility or claim anything, and any file or prompt it presents should be declined.
Written analysis generated 2026-11-15 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
12 findings contributed to this verdict, raised by external reputation, code shared with sites rated critical, page content, hosting and network, registration and ownership and behaviour in a sandbox.
01 External reputation
- 9 VirusTotal engines, including a leading vendor (Fortinet, Kaspersky, Sophos), marked this domain as malicious when the evidence was captured, which TrustSniffer counts as a confirmed external listing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Code shared with sites rated Critical
- The site runs the same code, or has code wired to the same hidden endpoint, as other sites TrustSniffer rated Critical.Code shared with sites rated Critical
rule:KIT_SHARED_WITH_CRITICAL_SITE
03 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
04 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, three to six months before capture.Hosting and network
rule:DNS_YOUNG_6M
05 Registration and ownership
- The registration lookup did not return the domain's registrant.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
06 Behaviour in a sandbox
- The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH - The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page quality: 2 findings share one limit, because each is weak evidence on its own. Together they stayed under the limit.
- Certificate and search-engine setup: 2 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Moltbook
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of allocation-moltbook.com.
- The request stayed on allocation-moltbook.com. It was not redirected to another domain. Clear
- Registered through NICENIC INTERNATIONAL GROUP CO., LIMITED. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-07-23. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
The same site on another domain
This site serves the same 16 distinctive code files as snapshot-moltbook.com, which TrustSniffer has also analysed and rates Critical on its own evidence. Matching this many files means the two are one build published on two domains, or one is a copy of the other.
It does not by itself show who operates them.
| Shared files (SHA-256) | turbopack-0sv1igg8bxcj.js.indir 0002d2f97da98f7e359c24f30173f552c29157a9e82c3941c0535033f9c31da1 |
|---|---|
| 0b13wm15bsoae.js.indir 0bc87c10fbdbfd8b989c6e2d404ed4696a89a3823354caeba8195b65163e07ac | |
| 0h22ag9vx03w0.js.indir 122b37fe8f2e27589f5cc5dc6baa85276c5701ad31ac34223a65c7c1e7ef2c86 | |
| 0zi9pha35ye3k.js.indir 1fdd25655f9a965b8cb97bf1df55bda4d0e5b99df9ed07feca11b97c8f2cab52 | |
| 14vpp7p82x389.css 564b7067d57c896204afe5bfdb5b286df9bfeb88d6e2e6d7ec1477a8edca4247 | |
| 0l92.dobm16l3.js.indir 5b652e996fadbe19bd7cc0ed2be01bcc6cd6c00907fee2b0e6c7596730a54e01 | |
| parse-1.28.18.min.js 98a4797f2e5da41573629587cad9845be7e80cbf9049c6014468b8245fefc073 | |
| 0-f2-2ydf7gdi.js.indir 9db886b9c93176e6a7781963661948e64a143671514ac1b66211a7c551f56af3 | |
| 0fw6koiparux.js.indir a85e3472c2ad63c3df3563d3c57a9630fec1a0ec4ff53eb34b72ec44a1cf4583 | |
| 0nbbghn6-ixh_.css b7164dc818a13f15279287919e9d93606e992bce3c7d73946cabf331cab3e41d |
Showing 10 of the 16 shared files. The others are kept in TrustSniffer's record of this analysis.
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3037::ac43:aff7 (a CDN edge address; the server behind it was not observed) |
| Name servers | jack.ns.cloudflare.com, laylah.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-19 |
| Domain age | 113 days (registered 2026-07-23) |
| Domain expiry | 2027-07-23 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 9 malicious, 3 suspicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about allocation-moltbook.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.