Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
authorize.cash shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the site asks visitors to sign in while its operator could not be verified and the registration lookup did not return the domain's registrant and country. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | Home page is a sign-in screen titled as a shop selling CVV card data and fullz identity packages. It directs users to shop links on authorize.wiki and offers registration with a Jabber or Telegram handle. Other pages show only the same sign-in and registration forms. No legal identity, address, contact channel, or refund policy is shown. Structure indicates an illicit stolen-data marketplace. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-11-13 and re-scored on 2026-11-14. The certificate, the registration age and the page content describe the site as it was on 2026-11-13.
- One external source flagged this site when the evidence was captured: 3 VirusTotal engines marked it as malicious. No second source confirms it. The alert is from the evidence captured on 2026-11-13; it was not re-queried for this version and is treated as unconfirmed. On its own it would limit the score to at most 49; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe unconfirmed alert ceiling (at most 49) also applies, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 3 marked it maliciousVirusTotal | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 5 months oldRegistered 2026-06-19 | Risk |
| Web archive | 35 snapshots35 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-06-19).
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
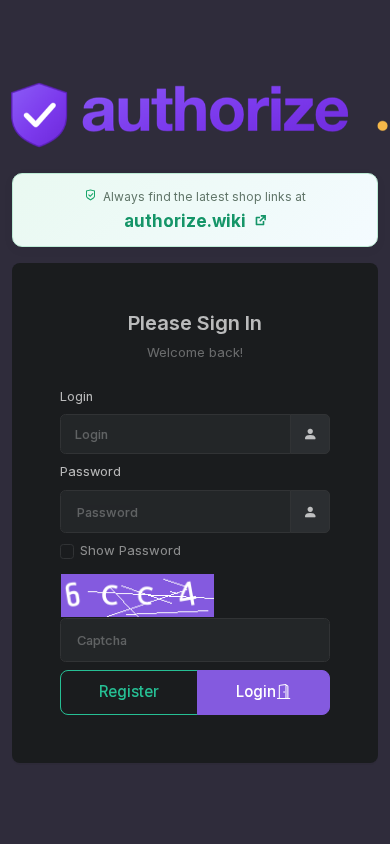
The site presents itself as "Cvv Authorize Shop | Fullz High Credit Score", a login and registration gateway to a shop that sells stolen payment-card data (CVV) and identity packages ("fullz"). Visitors see only a sign-in form, a registration form and a pointer to the "latest shop links" on a separate domain. The shop publishes no products, prices or operator. Registration is offered through a Jabber or Telegram handle. The business model is an illicit stolen-data marketplace.
Scam/Impersonation Risk
This site carries critical risk. Its own pages advertise card data and identity packages for sale, and buying such goods is a crime in most countries. Shops of this kind commonly take payment and deliver nothing, or harvest the credentials and contact handles of those who register. The pages disclose no operator, product list, pricing, contact channel or refund terms. Value flow is therefore entirely opaque. The page reader also found that the page is titled as a card-data shop yet lists no products or prices. It sends visitors to a rotating shop address on a different domain, so the site works as a funnel rather than a storefront. An external reputation service flagged the domain as malicious through three engines. That is a single source and no leading security vendor flagged it. Google Safe Browsing did not list it. The site's structure and stated business make the case independently of that alert. The assessment also found that the page kit is shared with another site rated critical. The domain name echoes a payment-processing term, but the site is a stolen-data shop and nothing shows any connection to a payment processor. No brand impersonation and no conflicting legal identities were detected.
- Homepage and login page: titled as a shop for "CVV" card data and "fullz", with a "Please Sign In" form and the line "Always find the latest shop links at" followed by a separate domain.
- Registration page: asks for account creation with a Jabber or Telegram handle, and no product, price or operator is shown on any of the three pages read.
- Registration record: domain registered 2026-06-19, 147 days old at capture.
- VirusTotal: 3 engines malicious, 0 suspicious, with no top-tier vendor among them.
Regulatory Verification Notes
On the pages read (login, index and registration), the site states no legal entity, no licence or registration and no regulator. Those are disclosures a financial or payment business is expected to make. The registration page says only that creating an account means agreeing to "Terms & Conditions and Privacy Policy", and no linked documents were read. The only name the site gives itself is the shop title. The site's own claims about what it is therefore cannot be tied to any real-world business or person, and identity is unverified. The domain's registration record lacks registrant and country details, and privacy of registration counts as a scored finding in the assessment. No licence was claimed on the pages read, so no registry check can apply. Nothing found suggests any regulated activity.
- Registration page: the Terms and Privacy Policy appear as plain text only, with no links read.
- Login, index and registration pages: no legal entity, registration number or regulator named.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- TLS: certificate issued by WE1, DV level, valid to 2027-01-14 at capture. Registrar: Global Domain Group LLC.
What to Verify Next
No verification step involves using the site. Anyone who encountered the domain should check their own accounts and cards through the issuing bank's official channels. Cardholders who suspect their data was sold should ask the issuer to monitor or reissue the card. The address, and any message steering recipients to it, should be reported to the relevant cybercrime or fraud-reporting authority and to the hosting provider's abuse channel. Organisations should check whether their own brand or customers' data appear in such listings through their usual threat-intelligence routes.
- Web archive: 35 snapshots, all in 2026, so the page was captured only during this short period.
- Registration record: expires 2027-06-19.
- Login and registration pages: the two forms collect a password and a handle, and no other data-collection channel was seen.
Summary Verdict
The site carries critical risk. Its stated business is the sale of stolen financial and identity data, and no operator or legitimate function was found. Its registration is recent, and signals that would normally support trust, such as a valid certificate, do not offset what the pages themselves advertise.
Infrastructure Integrity
The site is served through Cloudflare, with four edge addresses observed and no origin address visible. The host address's abuse record was checked and showed no reports. The use of a CDN is neutral and says nothing about the legitimacy of the content behind it. It does not reduce the risk.
Closing Assessment
Do not register, sign in, enter any password or handle, or follow the shop links. Do not attempt any purchase.
Written analysis generated 2026-11-14 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
14 findings contributed to this verdict, raised by external reputation, page content, hosting and network, several checks together, code shared with sites rated critical, registration and ownership and behaviour in a sandbox.
01 External reputation
- 3 VirusTotal engines marked this domain as malicious when the evidence was captured.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - A sign-in path on this site handles sensitive information.Page content
rule:PAGE_LOGIN_PATH_SENSITIVE - The page presents a sign-in form, and the operator behind it could not be independently verified.Page content
rule:PAGE_TYPE_LOGIN_UNVERIFIED - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
03 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, less than three months before capture.Hosting and network
rule:DNS_NEW_DOMAIN_90D
04 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
05 Code shared with sites rated Critical
- The site runs the same code, or has code wired to the same hidden endpoint, as other sites TrustSniffer rated Critical.Code shared with sites rated Critical
rule:KIT_SHARED_WITH_CRITICAL_SITE
06 Registration and ownership
- The registration lookup did not return the domain's registrant and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE - The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
07 Behaviour in a sandbox
- The page showed a password field during the sandbox session, and it could not be matched to a recognised brand's sign-in page.Behaviour in a sandbox
rule:BEHAV_PASSWORD_FORM_PRESENT
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page quality: 3 findings share one limit, because each is weak evidence on its own. The limit applied, so together they counted for less than their sum.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Cvv Authorize Shop
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of authorize.cash.
- The request stayed on authorize.cash. It was not redirected to another domain. Clear
- Registered through Global Domain Group LLC. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-06-19. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 3 other sites it has analysed. All 3 are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
| Shared files (SHA-256) | custom.js 285a7d712b3daee2dcb7193d08cf8ec4168e80d8d370091a6f60e7ae9802d416 (4 sites) |
|---|---|
| styles.min.css 314b6dcbfa4580bbfe81d3b0ce4a6f894fc7a0f46449c3f6aeaff510fb6c8ea6 (4 sites) | |
| main.js 5c04e7816955a33fc65caae85435f7ad5e91db35894fbaf31ee109a740002031 (4 sites) |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Global Domain Group LLC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3031::ac43:99f1 (a CDN edge address; the server behind it was not observed) |
| Name servers | greg.ns.cloudflare.com, grannbo.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-14 |
| Domain age | 147 days (registered 2026-06-19) |
| Domain expiry | 2027-06-19 |
| Archive first seen | Not available |
| Archive snapshots | 35 |
| Reputation | VirusTotal: 3 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about authorize.cash at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.