Verdict
The site's own pages showed several warning signs that deceptive sites commonly use, and together with the other checks they put it in the critical-risk band. Do not pay, sign in, or share personal details with this site.
authorizecc.shop shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the site asks visitors to sign in while its operator could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A login-gated site branded 'Authorize CVV' and 'Cvv Authorize Shop' that advertises CVV and 'Fullz' listings, which indicate stolen payment card and identity data. It discloses no operator, legal identity, address, licence, or refund terms, and its FAQ is keyword-repetitive. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-13 and re-scored on 2026-11-15. The certificate, the registration age and the page content describe the site as it was on 2026-11-13.
- The real-world operator identity was not independently verified.
- These checks returned no result: domain registration record (WHOIS), name servers (DNS), web archive lookup.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | None malicious; 2 marked it suspiciousVirusTotal, including Fortinet | Watch |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETNetwork registered in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- No security engine marked this domain as malicious; some marked it suspicious, which TrustSniffer does not count as a listing.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
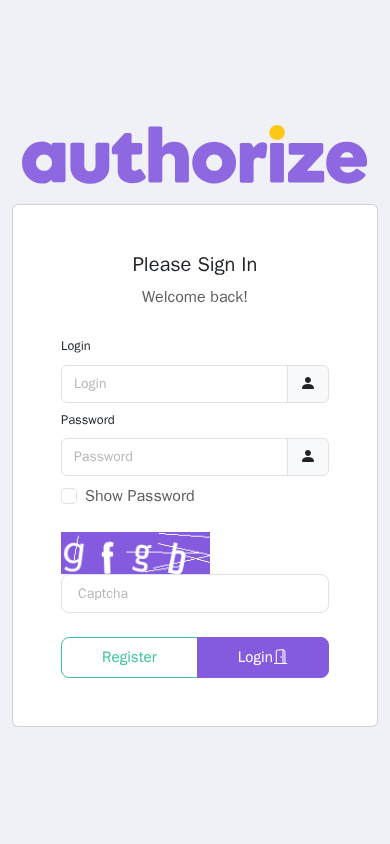
Authorizecc.shop presents itself to visitors as "Cvv Authorize Shop" and "Authorize CVV". Its homepage is a CAPTCHA-protected sign-in screen with a registration option. The page title advertises "CVV" and "Fullz High Credit Score" listings, which in underground-market usage refer to stolen payment card details and bundled identity records. The site's own FAQ calls it an online platform for "secure payment and digital services". The apparent business model, assessed with moderate confidence, is the sale of stolen financial and identity data to registered account holders. The pages describe no real product, service, delivery process or refund process.
Scam/Impersonation Risk
This assessment is one of critical risk. The pages read contain no conflicting legal entities, no hard-confirmed third-party listing and no detected impersonation of a named brand. The risk comes from what the site offers and how it describes itself. The site says it provides "secure payment and digital services", yet its listing titles refer to stolen card and identity data. The page reader judged these two claims irreconcilable. The FAQ repeats "authorize cvv" and "authorize cc shop" many times without describing any actual product. That is keyword stuffing, not a description of a service. The word "authorize" echoes the vocabulary of legitimate payment-processing services. The domain does not appear to belong to any such brand, and nothing on the pages connects the site to one. Registration asks for a Jabber or Telegram contact instead of a verifiable email address or company contact. No postal address was found on the pages read. Purchasing stolen card data is unlawful in most jurisdictions, and marketplaces of this kind commonly collect payment or contact details and deliver nothing. A third-party reputation check recorded two engines with a suspicious rating and none with a malicious rating. The source of this note is the reputation engines, not the site's own content. The details of any other external detections were not specified. I treat it as a soft reputation note and give it limited weight, because no engine rated the site malicious and it is not a confirmed listing. The risk assessment rests mainly on the site's own content.
- Homepage: the title and page text advertise "CVV" and "Fullz High Credit Score" listings, translated in meaning as stolen card data and identity packages.
- Homepage FAQ: repetitive brand-keyword answers that describe no concrete product, price, delivery method or refund process.
- Registration page: asks for a Jabber or Telegram contact in place of an email address or company contact.
- Reputation check: 2 engines returned a suspicious rating and 0 returned a malicious rating. This is a soft third-party warning, not a confirmed listing. No safe-browsing listing was recorded.
Regulatory Verification Notes
On the pages read (the homepage and the registration page), no legal entity, registration or licence number, regulator or terms-and-privacy page was found. The only identity the site offers is its own brand label, "Cvv Authorize Shop". This is a self-asserted claim, and TrustSniffer found no independent verification of it. The site's operator and ownership are not identifiable from the pages read. A business that offers payment or financial services would be expected to publish all of these disclosures. Their absence is consistent with the other findings and does not by itself establish wrongdoing. No third-party broker or regulator record matched the site. The site's transport encryption is a basic domain-validated certificate. That shows only that the connection is encrypted and says nothing about who operates the site.
- Homepage and registration page: no operator name, legal entity, address, licence, regulator or terms of service on the pages read.
- Transport encryption: TLS certificate issued by WE1 (DV validation), valid until 2026-12-21 as seen at capture on 2026-11-13.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Third-party broker dataset: no matching record.
What to Verify Next
Verification here is mainly about protecting potential victims, since the evidence does not support treating the site as a legitimate merchant. Anyone who believes their own card or identity details were offered or exposed through this kind of marketplace should contact their card issuer or bank through the official number printed on the card. Anyone who has already supplied details to the site should do the same. A payment-processing company whose name the domain seems to echo can be asked, through its own published support route, whether it has any relationship with this site. Security teams may wish to record the domain in their internal block and monitoring lists. The matter can also be reported to the relevant national cybercrime or fraud-reporting authority.
- Pages read: only the homepage and the registration page were available for review.
- Homepage: listings sit behind a single CAPTCHA-gated sign-in form, so the offers themselves could not be inspected.
- Registration page: the only contact route is a messaging handle request, so no independent business channel exists to confirm.
Summary Verdict
The available evidence places this site at critical risk. The content it presents, the way it describes itself, and its lack of any identifiable operator all point the same way. No apparent legitimate purpose offsets this. Because the site's identity is unverified and the offers could not be inspected, this is a judgement from the evidence available. The evidence is most consistent with an illicit marketplace for stolen payment and identity data, not a lawful business.
Infrastructure Integrity
The site is fronted by a Cloudflare content delivery network. All four observed addresses are edge addresses, and the origin server was not observed. The host's abuse record was checked and showed no reports. This is a neutral finding that neither supports nor undermines the site's legitimacy, and it does not offset the content-based findings.
Closing Assessment
The site should not be used. No data, contact handles or payment details should be submitted to it, and no one should register on it or buy from it. Anyone who has already interacted with it should treat any details they supplied as exposed and contact their card issuer or bank.
Written analysis generated 2026-11-15 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
9 findings contributed to this verdict, raised by page content, several checks together, and registration and ownership.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page presents a sign-in form, and the operator behind it could not be independently verified.Page content
rule:PAGE_TYPE_LOGIN_UNVERIFIED - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
02 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
03 Registration and ownership
- The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page quality: 2 findings share one limit, because each is weak evidence on its own. Together they stayed under the limit.
- Certificate and search-engine setup: 3 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Cvv Authorize Shop
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of authorizecc.shop.
- The request stayed on authorizecc.shop. It was not redirected to another domain. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3034::ac43:8aee (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-21 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 0 malicious, 2 suspicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about authorizecc.shop at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.