Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
axiomdeveloperrpc.pages.dev shows high-risk / scam indicators.
| What this site appears to be | A crypto support and recovery page that asks visitors to connect their wallet before proceeding, offers help with lost funds, locked accounts, and airdrop claims, and gates token purchases behind a 'trusted payment source' status. It names no verifiable operator, legal entity, address, or regulatory status, and it references third-party wallet brands (Coinbase Wallet, Ledger) without establishing any affiliation. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 7 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
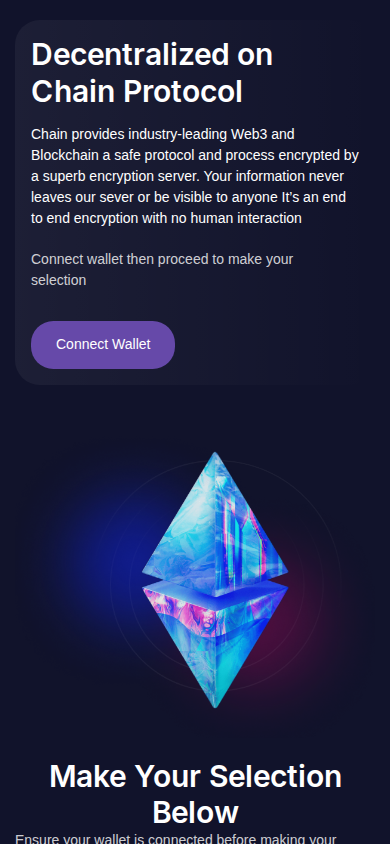
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- No flags from the reputation services TrustSniffer consulted at assessment time.
Full analysis
Scam/Impersonation Risk
No confirmed listing on a blocklist, phishing finding, identity contradiction or verified brand impersonation was observed, and the identity-contradiction category is not triggered. The page's structure and content nonetheless call for verification before any interaction. The homepage opens with "Connect wallet then proceed to make your selection". It then offers a menu of generic grievance categories aimed at users in distress: "Missing/Irregular balance – recover lost/missing funds", "Locked Account", "Claim Airdrop", "Wallet glitch / wallet error" and "Click here to claim assets". This is consistent with the pattern of wallet-drainer and recovery-scam funnels, in which a visitor is steered to authorise a connection or signature in order to be "helped". That is an assessment of the pattern, not a confirmed finding about this site. The "Buy Coins/Tokens" item states that "your account must be marked as a trusted payment source". This gatekeeping status is not explained and could be used to justify a fee or deposit, although no fee is shown. The page asserts "industry-leading" Web3 protection, a "superb encryption server", "end to end encryption with no human interaction" and that "your information never leaves our server". It supports none of these claims with a named operator, audit or mechanism. It also names Coinbase Wallet and Ledger without any demonstrated affiliation. The hostname is a free-hosting subdomain whose label evokes a developer or RPC service, and it closely resembles its hosting platform's own domain, which raises a lookalike concern. No brand impersonation is confirmed. A single security engine returned an unconfirmed "suspicious" rating. This is a soft third-party reputation note. It comes from one source, is not corroborated by other engines, and is not a finding of listing, so it is given limited weight. During automated browsing no wallet-connection, clipboard-manipulation or outbound data-posting behaviour was triggered. The page did load several suspicious inline scripts and produced a high volume of console errors. Both are observations from automated browsing and neither is confirmed malicious behaviour. Evidence: Homepage: wallet-connection prompt precedes all content, and fund-recovery, asset-claim and airdrop call-to-action items are presented as support topics. Homepage: "Buy Coins/Tokens" is conditioned on the account being "marked as a trusted payment source", with no fee or process explanation. Homepage: unsubstantiated security claims ("superb encryption server", "end to end encryption") appear alongside no named operator. Domain provenance: the site's hostname is about 9 days old (0.02 years), and the web archive holds 1 snapshot, dated 2026, so there is no meaningful history.
Scam/Impersonation Risk
No confirmed listing on a blocklist, phishing finding, identity contradiction or verified brand impersonation was observed, and the identity-contradiction category is not triggered. The page's structure and content nonetheless call for verification before any interaction. The homepage opens with "Connect wallet then proceed to make your selection". It then offers a menu of generic grievance categories aimed at users in distress: "Missing/Irregular balance – recover lost/missing funds", "Locked Account", "Claim Airdrop", "Wallet glitch / wallet error" and "Click here to claim assets". This is consistent with the pattern of wallet-drainer and recovery-scam funnels, in which a visitor is steered to authorise a connection or signature in order to be "helped". That is an assessment of the pattern, not a confirmed finding about this site. The "Buy Coins/Tokens" item states that "your account must be marked as a trusted payment source". This gatekeeping status is not explained and could be used to justify a fee or deposit, although no fee is shown. The page asserts "industry-leading" Web3 protection, a "superb encryption server", "end to end encryption with no human interaction" and that "your information never leaves our server". It supports none of these claims with a named operator, audit or mechanism. It also names Coinbase Wallet and Ledger without any demonstrated affiliation. The hostname is a free-hosting subdomain whose label evokes a developer or RPC service, and it closely resembles its hosting platform's own domain, which raises a lookalike concern. No brand impersonation is confirmed. A single security engine returned an unconfirmed "suspicious" rating. This is a soft third-party reputation note. It comes from one source, is not corroborated by other engines, and is not a finding of listing, so it is given limited weight. During automated browsing no wallet-connection, clipboard-manipulation or outbound data-posting behaviour was triggered. The page did load several suspicious inline scripts and produced a high volume of console errors. Both are observations from automated browsing and neither is confirmed malicious behaviour. Evidence:
- Homepage: wallet-connection prompt precedes all content, and fund-recovery, asset-claim and airdrop call-to-action items are presented as support topics.
- Homepage: "Buy Coins/Tokens" is conditioned on the account being "marked as a trusted payment source", with no fee or process explanation.
- Homepage: unsubstantiated security claims ("superb encryption server", "end to end encryption") appear alongside no named operator.
- Domain provenance: the site's hostname is about 9 days old (0.02 years), and the web archive holds 1 snapshot, dated 2026, so there is no meaningful history.
Regulatory Verification Notes
The site contains no legal or identity pages. It names no operating company, registered address, support channel, terms of service, privacy policy, license or regulator, so no legal basis for handling user funds or wallet permissions can be assessed. The operator's real-world identity is unverified, and ownership is opaque on the page itself. Services of this kind (recovery, token sales, asset claims) would ordinarily require clear entity disclosure and, depending on jurisdiction, virtual-asset provider registration. None is claimed, so none can be tested. No third-party broker or regulatory record matched this site, which means the absence of an external record is neutral, not exculpatory. The TLS certificate shows the connection is encrypted but says nothing about who runs the site. Evidence:
- Homepage: no company name, address, license number, regulator reference, or terms and privacy documents.
- Homepage: no fee schedule, service description or accountable party behind the recovery and purchase flows.
- Transport layer: Domain-validated TLS certificate issued by YE1, valid to 2026-12-08 (49 days remaining), which confirms encryption only.
- Hosting: served from AS13335 (Cloudflare, Inc., US); not recognised as a listed DeFi protocol.
What to Verify Next
Any claim of affiliation with a wallet vendor or protocol should be tested directly. The wallet vendor or protocol team should be contacted through its official website, typed by hand or taken from a trusted source, to ask whether this site is endorsed. Any wallet vendor's genuine support process should be reached independently, because legitimate wallet providers do not normally recover funds through an unsolicited "connect your wallet" page. The operating entity should be established from a source outside this site before any signature, approval or deposit is considered. Where a regulated-entity claim is later made, it should be checked against the relevant national virtual-asset or financial-services register. Existing wallet approvals should be reviewed and revoked if there has been any prior interaction. Evidence:
- Homepage: no operator, address or regulator is named, so independent registry checks have no identifier to start from.
- Homepage: Coinbase Wallet and Ledger are referenced with no demonstrated relationship.
- Homepage: recovery and claim flows require a wallet signature or connection, so any prior interaction merits an approvals review.
Summary Verdict
The available evidence supports a verify-before-proceed posture. The site is an anonymous, newly observed crypto-recovery funnel. Its content, structure and unsupported claims are consistent with patterns associated with fund-recovery and wallet-connection schemes. This is not a confirmed finding. Legitimacy cannot be inferred from the site's technical hygiene, and the operator's identity remains unverified.
Infrastructure Integrity
The site is served through Cloudflare's CDN and web-application-firewall network (AS13335, US), and all four observed addresses are edge nodes. The hosting origin is not observable. This is a mitigating factor only: it indicates a mainstream hosting platform and a valid, encrypted connection, but it conceals the origin and can mask rapid content swaps. It does not offset the page-level concerns or establish who operates the site.
Closing Assessment
Before connecting a wallet, signing or paying on this page, the operator should be independently identified and any affiliation claims confirmed through official channels. Until then, browsing for information alone is the proportionate limit. Any assistance with lost funds should be sought through the official channels of the relevant wallet or exchange.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by page content, hosting and network, behaviour in a sandbox, history in the web archive.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Behaviour in a sandbox
- The page carried inline scripts written in a style TrustSniffer treats as suspicious.Behaviour in a sandbox
rule:BEHAV_SUSPICIOUS_INLINE_SCRIPTS
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of axiomdeveloperrpc.pages.dev.
- The request stayed on axiomdeveloperrpc.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-10-10. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2f79 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-08 |
| Domain age | 0.02 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2026-10-10 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 0 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about axiomdeveloperrpc.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.