Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
bordrsolana.com shows high-risk / scam indicators.
| What this site appears to be | A Solana-based token airdrop landing page for '$ATTENTION' that asks visitors to connect a wallet to claim tokens under time pressure. It gives no verifiable team, legal entity, audit, contact details, or product detail, and it uses homoglyph and zero-width text obfuscation. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 11 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20262 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
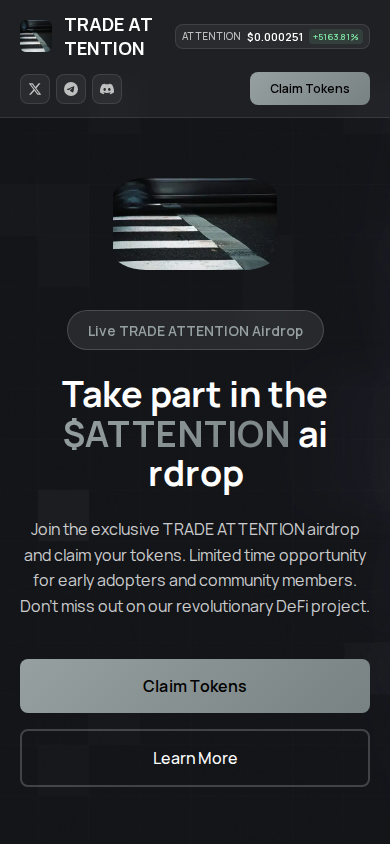
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website is a single-page Solana token airdrop landing site branded "TRADE ATTENTION". It promotes a "$ATTENTION" token giveaway and shows a displayed price, a dramatic percentage gain and a "Claim Tokens" button. Visitors are asked to connect a crypto wallet to receive an allocation. Its apparent purpose is to funnel visitors into a wallet-connection step under the cover of a promotional token distribution, with no explained product or revenue model.
Scam/Impersonation Risk
The evidence converges on a clearly elevated risk. At least one external threat-intelligence source currently lists the domain, and this confirmed blacklist is the decisive contradiction. No brand impersonation and no conflicting legal identities were found, but the page content independently shows the hallmarks of a wallet-targeting promotion. The homepage offers 1,000,000 tokens to a stated 50,000 participants. A "7 Days Left" countdown and "Limited time" wording create urgency. An unsourced price of $0.000251 sits beside a claimed +5163.81% move, and the page cites unverifiable usage figures of $2.5M volume and 150K+ users, alongside phrases such as "Join millions of users" and a "revolutionary DeFi project". The eligibility steps (be a Solana user, hold some tokens, follow a social account) end in a "Connect Wallet" prompt. The page explains no mechanism by which the token has value. Its navigation promises Trading, Staking, Analytics, API, Whitepaper, Roadmap and Tokenomics sections, but the captured page shows no such product, so the claims do not match the evidence behind them. The page text is also deliberately obfuscated. It mixes Cyrillic look-alike letters into English words and inserts invisible zero-width characters, which defeats keyword matching and reads as intentional evasion of detection. This combination is the standard pattern of wallet-drainer and fake-airdrop campaigns. No wallet-drain behavior was observed in sandbox runs, but the lack of observed behavior does not offset the other signals.
- The domain was registered on 2026-10-08 (about 12 days old, 0.03 years), so there is no operating track record behind the token and statistics it advertises.
- The web archive holds only 2 snapshots, both from 2026 (first seen 2026-10-08, last seen 2026-10-08, 1 year tracked), which shows no prior history for the brand.
- The homepage shows a countdown, a +5163.81% price change and unsourced volume and user counts next to a wallet-connect call to action.
- The homepage text uses Cyrillic homoglyph substitution and zero-width characters to disguise words, a deliberate deception signal.
Regulatory Verification Notes
The site presents no legal entity, team, audit, registered address, licence, or contact route. The footer links to Privacy Policy, Terms of Service, Cookie Policy and Disclaimer pages and carries a copyright line in the brand's name. None of this identifies an accountable operator, and the brand name itself is rendered with look-alike characters. A token distribution that solicits wallet access is a high-stakes interaction, and the absence of any verifiable legal status or accountable counterparty is material here. This is a verification gap that compounds the confirmed threat listing rather than a stand-alone finding. Independent identity verification is unconfirmed, and no third-party broker or regulatory-registry match exists for the site. The domain registrant is masked by privacy protection, which is an administrative detail and not itself an identity contradiction. Any apparent professionalism of the page therefore cannot be treated as evidence of legitimacy.
- The homepage footer lists legal-style links and a copyright line but names no company, jurisdiction, officer, or registration number.
- The homepage states no contact address, support channel or team information.
- The domain is registered through PDR Ltd. d/b/a PublicDomainRegistry.com with the registrant masked, registered 2026-10-08 and expiring 2027-10-08.
- The site is served from AS13335 (Cloudflare, Inc., US) behind a valid DV TLS certificate issued by YE1, valid to 2027-01-06. A DV certificate confirms only domain control and says nothing about the operator.
What to Verify Next
No verification step can make this site safe to interact with while the threat listing stands. Verification is therefore for investigators and for anyone who encountered the link. The first step is to trace how the link was received (social post, direct message, or advertisement) and to treat unsolicited promotion as an aggravating factor. The second step is to look for an official announcement of "$ATTENTION" from an independently verified project channel, reached by a route not provided by this site. The third step is to confirm any claimed token on an independent blockchain explorer, checking mint authority, holder distribution, and creation date before assuming it exists as described. The last step is to check official, independently sourced contact channels, since none are published here.
- The homepage cites a stated 1,000,000-token allocation and a 50,000-participant figure with no source or on-chain reference.
- The homepage lists Whitepaper, Tokenomics, Roadmap and Documentation labels but, as captured, offers no working documentation to cross-check.
- The homepage names a single token, "$ATTENTION", which makes an independent ledger lookup straightforward.
Summary Verdict
The assessment is critical. Confirmed adverse reputation from external threat intelligence, a newly created domain, and a page designed around urgency and wallet connection all point the same way. No credible positive evidence of legitimacy offsets this. Valid certificate hygiene is the only supportive element and carries negligible weight against the convergence of negative signals.
Infrastructure Integrity
The site sits entirely behind Cloudflare's CDN and WAF, with all four observed addresses belonging to edge servers. The origin server is not observable. This is a mitigating factor only and does not indicate legitimacy. Edge-only visibility also prevents independent verification of where the content is actually hosted and can mask rapid content swaps. A new, low-cost domain behind a shared edge network is exactly the setup used to relaunch quickly if a domain is taken down.
Closing Assessment
Treat the site as hostile. Do not connect a wallet, sign any transaction or approval, follow its social prompts, or enter credentials or payment details. If a wallet was already connected, revoke token approvals and move assets to a fresh wallet. Report the link to the platform where it was found. Any further inspection should be read-only and done in an isolated environment.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, page content, hosting and network, several checks together.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG
03 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
04 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of bordrsolana.com.
- The request stayed on bordrsolana.com. It was not redirected to another domain. Clear
- Registration is published under PDR Ltd. d/b/a PublicDomainRegistry.com. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-10-08. Noted
- The earliest public archive of this site is from 2026-10-08. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | PDR Ltd. d/b/a PublicDomainRegistry.com |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3034::6815:2405 |
| Name servers | PENNY.NS.CLOUDFLARE.COM, SCOTT.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2027-01-06 |
| Domain age | 0.03 years (continuous registration) |
| Domain expiry | 2027-10-08 |
| Archive first seen | 2026-10-08 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 1 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about bordrsolana.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.