Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
decentralizedapp.pages.dev shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
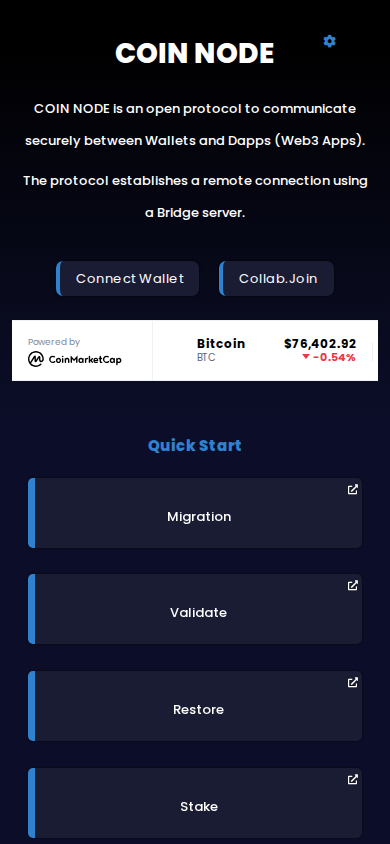
| How the site describes itself | The page promotes a crypto wallet 'fix' and recovery service under the COIN NODE / Wallet Fix branding. It centers on a Connect Wallet action and promises restoration of tokens, airdrop claims, and staking harvests, with claimed metrics (50K+ active wallets, 200K+ resolved issues) and no verifiable operator identity, contact, or pricing. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 14 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 28 months before captureWeb archive; a site on pages.dev has no registration of its own | Risk |
| Web archive | Archived since 20246 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: less than 1 year before capture (web archive; a site on pages.dev has no registration of its own).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Overview
COIN NODE, also branded "Wallet Fix", is a single-page crypto website. It presents itself as an open protocol for connecting wallets to decentralized apps. Its main call to action is a "Connect Wallet" button, and it offers to "fix", "recover" and "restore" wallet problems. The page lists services such as token restoration, airdrop claims, staking harvests, reflection claims, NFT minting, bridging and LP lock. Its apparent business model is to draw visitors into linking a wallet in return for promised recovery or reward outcomes, with no stated price, operator or terms.
Scam/Impersonation Risk
Contradictory signals are present, and they are severe. Several independent security engines, including tier-one vendors, currently flag the site as malicious, and the site is blacklisted by external threat sources. The page content matches the pattern of wallet-drainer lures. A "Connect Wallet" button is the only entry point. The offered outcomes ("Claim Airdrop Rewards", "Harvest my stakings", "Restore tokens", "Claim Reflection") are the usual bait for tricking holders into approving malicious transactions. The unsupported claims make this worse. The page boasts "50K+ active wallets", "200K+ resolved issues" and "100+ contributors", with nothing to substantiate them. It also shows a live price ticker for BTC, ETH, XRP, USDT, BNB, ADA and USDC, which adds an appearance of legitimacy but proves nothing. The footer reads "© 2022" on a page observed in 2026, which suggests recycled template content rather than a maintained product. The site is a free-tier tenant subdomain on a shared hosting platform, so no registered brand domain stands behind it. A sibling site on the same platform, with a similar fix-and-recovery theme, is also flagged as malicious. This points to a reused scam kit rather than a one-off project. The behavioural sandbox did not observe a wallet-drain attempt, clipboard hijacking or hidden forms. That is a limited mitigating observation and does not offset the external detections or the nature of the offer. No brand impersonation was confirmed.
- Homepage: the primary action is "Connect Wallet", with promises of airdrop claims, staking harvests, token restoration and reflection claims, and no explanation of how these outcomes are achieved.
- Homepage: unverifiable usage statistics and a 2022 copyright notice on a current page.
- Threat-intelligence results: multiple security engines, including tier-one vendors, flag the domain as malicious, and it is also listed in external blacklists.
- Platform context: the site is a tenant subdomain, and a similar sibling site on the same platform is also flagged.
Regulatory Verification Notes
The site discloses no legal entity, registered address, licence, registration number, contact channel, pricing, refund policy or security documentation. For a service that asks visitors to expose wallet access, this is a significant transparency gap. The site's own copy also describes the service in ways that would normally fall under financial or custody oversight, yet no authority or licence is claimed. Governance and ownership are opaque. No third-party broker or regulatory-registry entry matched the site, and the absence of a match is neutral rather than adverse. The domain is a few months old. The archive holds only a handful of snapshots, which does not amount to an established track record.
- Domain registration: about 0.4 years old (roughly five months).
- Web archive: 6 snapshots spanning 2024–2026 (3 years tracked).
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: DV certificate issued by WE1, valid to 2026-12-25. This confirms an encrypted connection only, not who operates the site.
What to Verify Next
Any party that has already interacted with the site should first check whether a wallet was connected or a transaction signed. If so, they should review and revoke token approvals through a reputable approval-management tool and move remaining assets to a newly created wallet. Anyone contemplating the service should look for the operator in the official registries of their own jurisdiction. Recovery services should be sought only from providers found through independent, offline routes. The site offers no usable contact channel, so there is nothing to confirm with the operator. Recovery claims such as "200K+ resolved issues" should be treated as unproven unless an independent source supports them.
- Homepage: the only action offered is wallet connection, and the page names no operator who could be checked.
- Homepage and footer: no company name, licence or registration reference is shown.
- Threat-intelligence results: the external flags relate to this domain and are current.
Summary Verdict
The assessment is critical and the posture is high-risk. Current external threat detections, a wallet-connection lure and an unverifiable operator converge on a likely asset-theft or credential-theft purpose. The site's technical hygiene does not alter that conclusion.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF. All four observed addresses are CDN edge servers, and no origin server was observable. That provides ordinary delivery protection and a valid certificate, which are only mitigating factors. They cannot be read as evidence of legitimacy. Edge-only visibility also means the site's content can be swapped quickly without any change being visible at the infrastructure level.
Closing Assessment
The site should not be used for any purpose involving a wallet, login, credentials or payment. Wallet connection and transaction signing should be avoided. At most, the page may be viewed for information, and nothing should be downloaded or approved from it.
Written analysis generated 2026-11-04 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content and several checks together.
01 External reputation
- A confirmed external listing marks this domain as malicious: at least five security engines including a leading vendor, ten engines, or Google Safe Browsing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of decentralizedapp.pages.dev.
- The request stayed on decentralizedapp.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2024-06-21. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 1 other site it has analysed. That site is rated Critical on its own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
| Shared files (SHA-256) | main.css 39ba049d03abe5def80830ba38d0f2b432dd7374cac67ffd3c800d9bcc551164 |
|---|---|
| walletpage.css 7f27584b0c891c2340eae90868b94b543d1a9d149bc9c6e9407d127320f57b98 |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:310c::ac42:2f55 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-25 |
| First seen (web archive) | 0.42 years before capture; a site on pages.dev has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2024-06-21 (2.4 years before capture) |
| Archive snapshots | 6 |
| Reputation | VirusTotal: 14 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about decentralizedapp.pages.dev at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.