Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
dragondex-claim.vercel.app shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on vercel.app, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| How the site describes itself | A DragonDEX token airdrop ('Hunt') campaign page that rewards points for crypto activity on a Nexo-branded platform, with a wallet connection step and a stated 10M-token pool. The page's licensing, certification and legal content belongs to Nexo, while the issuing DragonDEX entity and the token's verifiable details are not identified. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 89 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 9 months before captureWeb archive; a site on vercel.app has no registration of its own | Watch |
| Web archive | Archived since 20265 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WR1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: less than 1 year before capture (web archive; a site on vercel.app has no registration of its own).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
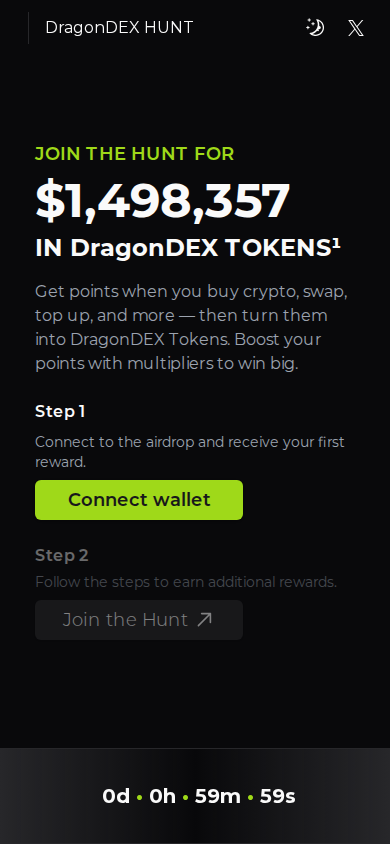
This website is a single-page token airdrop landing page titled "DragonDEX Hunt", hosted as a free subdomain on a shared application-hosting platform. It invites visitors to connect a crypto wallet and earn points for buying crypto, swapping or topping up. The points can then be converted into "DragonDEX" tokens from a stated pool of 10,000,000 tokens, with a headline claim of roughly $1.5 million in tokens at stake. Its apparent purpose is to promote a token launch and drive wallet connections and platform activity, using Nexo-branded footer material that the page does not clearly tie to the DragonDEX campaign.
Scam/Impersonation Risk
Material contradictions are present. Several independent security engines currently flag the site as malicious or suspicious, and it also appears on an external blacklist. A sibling campaign page on the same hosting platform, built to the same "Hunt" pattern, is also flagged. That indicates a reusable template, not an isolated page. The homepage shows several pressure and trust-borrowing mechanics. A countdown timer reads under one hour remaining. A large dollar figure is attached to the tokens, yet the page concedes the figure rests on a market price dated June 2024 and may differ at claim time. The main call to action is "Connect wallet", with a second step that sends visitors on to "earn additional rewards". The page does not name the entity issuing the token, and no verifiable token details are given. A page like this is a common lure for wallet-draining and credential-harvesting campaigns. The sandbox did not observe wallet-drainer behavior, clipboard hijacking or hidden forms. Those negative observations do not offset the external detections. No conflicting legal entities were found, and the verdict does not rest on any identity inconsistency.
- Homepage: the "Connect wallet" and "Join the Hunt" steps, the near-expired countdown, and the $1,498,357 headline value are tied to a price "as of June 16, 2024".
- Domain provenance: the domain is about 0.77 years old (roughly 280 days), with its first web-archive capture in 2026.
- Web archive: 5 snapshots in total, all within 1 year tracked (2026), indicating a young, thinly documented site.
- Reputation: 3 engines rate the site malicious and 1 suspicious. A sibling page on the same platform is flagged as part of the same pattern.
Regulatory Verification Notes
The page carries a large block of footer material that reads as another company's: product menus, a "Licenses" link, a list of legal terms, security certifications and the statements "Licensed & Regulated Digital Assets Institution" and "Trusted by 7M+ people". None of this identifies the DragonDEX issuer, and no licence, registration number or regulator is stated for the campaign itself. The licensing, certification and user-count claims are unverifiable superlatives that belong to a different brand, so they cannot support the airdrop. The page also tells residents of the USA, UK and Canada they are ineligible and points to a separate legal page for the campaign terms. Ownership and governance are opaque, and the operator's real-world identity is unverified. No broker-reputation entry was matched. The cautionary posture rests on the threat detections, not on this licensing gap.
- Homepage footer: Nexo-branded product, legal and certification links appear alongside the DragonDEX name, with no link between the two entities.
- Homepage disclaimer: the 10,000,000-token pool value is described as "indicative", and USA, UK and Canada residents are excluded.
- Hosting: served from AS16509 (Amazon, AMAZON-02, US).
- Transport encryption: the TLS certificate was issued by WR1 (DV, domain validation only), valid to 2027-01-29. This confirms encryption only, not operator identity.
What to Verify Next
Any claim connecting this page to a real company should be confirmed from the official channels of the brand it borrows from. Those channels are reached by typing the brand's known address directly or using its official app, never through this page. The campaign and the token should be checked for an official announcement from that brand. The issuing entity and a verifiable token contract should be confirmed independently before any wallet is linked. Support and contact channels should be confirmed through an independent route.
- Homepage: no issuing entity, token contract or campaign legal page was identified in the captured content.
- Page behavior: 12 console errors and external requests to several destinations were observed during sandbox runs.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Page signals: the page shows a mismatch between its claims and its supporting evidence, and an unverifiable legal status.
Summary Verdict
The overall posture is high-risk. External threat detections outweigh the site's technical hygiene, and its operator remains unverified. The site is a thinly established, template-style airdrop page that borrows another brand's credibility without substantiation. It is not safe for sensitive interaction.
Infrastructure Integrity
The site is served from Amazon-hosted infrastructure in the United States, behind a shared platform's CDN/WAF. All observed addresses are edge nodes, and no origin server was observable. That means the hosting cannot be independently verified, and content could be swapped quickly. A valid certificate and mainstream hosting are mitigating factors only. The platform's free subdomains are open to anyone, so the setup says nothing about who runs this page. Numerous abuse reports exist against the shared edge address. They are attributed to the provider's shared infrastructure and discounted, so they are not treated as evidence against this site.
Closing Assessment
The page should be treated as read-only at most. Wallets should not be connected, credentials or seed phrases should not be entered, and no funds or tokens should be moved through it. Anyone interested in the campaign should use only the official channels of the genuine brand.
Written analysis generated 2026-11-06 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content, registration and ownership and behaviour in a sandbox.
01 External reputation
- Three or more VirusTotal engines, or two including a leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The page runs on a free vercel.app address instead of a domain of its own, a setup common to short-lived phishing and claim pages.Page content
rule:PAGE_BRAND_SUSPECTED - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
03 Registration and ownership
- As a site on vercel.app, this address has no registration record of its own (the platform's domain is registered, not the site).Registration and ownership
rule:KF_WHOIS_INCOMPLETE
04 Behaviour in a sandbox
- The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 89 reports on hosting IP 64.29.17.131 (AMAZON-02), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of dragondex-claim.vercel.app.
- The request stayed on dragondex-claim.vercel.app. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-01-29. Clear
- It is hosted on AMAZON-02, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 1 other site it has analysed. That site is rated Critical on its own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
| Shared files (SHA-256) | 249261e921aeebba.js 7961aca892de681b29e57241a0ce9228f757707798eab660b1802fcde0f720dc |
|---|---|
| 54f7a9c94896a495.js 86c746840d8072cb4b8e41f6ebdc70aeb9dacc40fdb275314061c468ccaca6a9 | |
| 51d44c3b9bf8d551.js 92d411ab27e010620848069f2c17d85e962c0540cd31d55a2e9a92530614a412 | |
| 761b28e8667a8205.css a0886fbb110aef702f3850684020edb2b5d62eda83e35afb557100ebd44363f6 | |
| aa0a7c5c022cbeb9.js a32cfbfeb00a7e262808bf7665f4cdd076d8fc1fe6321b0be01c97c9d7692bd9 | |
| 7340adf74ff47ec0.js d8e91f5e0c241a7fc0b00a57fbd5398c27b03931244b685e2a703a1947dda34a | |
| 63cc160050942eaf.js ebf948b9885e915211cbb7370586f764d6c5c19581ceed9efc1c833f1de79f05 |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc. |
| Network registered in | US |
| Server IP | 64.29.17.131 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected |
| Resolved IP addresses | 6 |
| Edge IP addresses | 6 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR1 |
| SSL expiry | 2027-01-29 |
| First seen (web archive) | 281 days before capture; a site on vercel.app has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2026-01-29 (281 days before capture) |
| Archive snapshots | 5 |
| Reputation | VirusTotal: 3 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 89 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about dragondex-claim.vercel.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.