Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
mainetsapps.pages.dev shows high-risk / scam indicators.
| What this site appears to be | Coin Node describes itself as an open protocol for secure wallet-to-dapp communication via a bridge server. The page is mainly a service menu for wallet recovery, restoration, token claims, staking, and gas or bridge issues, with a 'Connect Wallet' call to action and unverified usage statistics. The footer names a different brand (Wallet Fix) and a 2022 copyright. No legal entity, address, contact channel, or pricing is shown, so the high-stakes wallet interactions lack supporting evidence. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 12 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Listed as unsafeGoogle | Risk |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 2.6 years oldRegistered history | Clear |
| Web archive | Archived since 20249 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
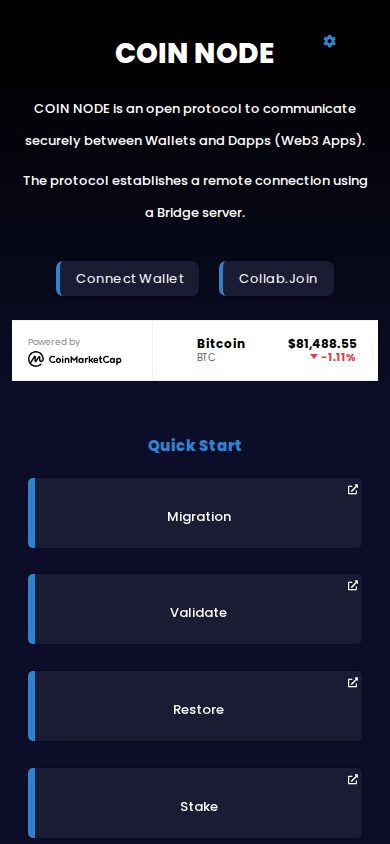
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: 1 to 3 years (registration continuity).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Google, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website presents itself as "Coin Node", an open protocol for secure communication between crypto wallets and web3 applications through a bridge server. Its single landing page is mostly a menu of wallet-intervention services: Restore, Recovery, Claim Airdrop Rewards, Harvest my stakings, Withdrawal, Gas, LP Lock, Restore tokens and NFT Mint. A prominent "Connect Wallet" call to action leads into these services, and a scrolling ticker of major cryptocurrency prices sits above them. The apparent business model is a "blockchain issue resolution" service, either paid or free, that has visitors link their wallets in order to recover, claim or move tokens.
Scam/Impersonation Risk
Contradictory signals are present and they are severe. The site is blacklisted by multiple independent reputation sources. A major browser-protection service flags it under its social-engineering category, which covers phishing and deceptive-lure pages. A large cluster of security engines also rate it malicious, including several top-tier vendors. These are confirmed external detections, and they alone place the site in an elevated-risk posture. The content matches the detections. The homepage offers wallet "recovery", airdrop claims, staking "harvesting", withdrawals and token restoration as a menu behind a wallet-connection prompt. This is the standard lure for wallet-drainer and fake-support schemes, in which a visitor is induced to authorise transactions or reveal access to the wallet. The page gives no explanation of what a connected wallet would be asked to sign, and it shows no fee schedule or refund terms. The branding is also inconsistent: the header says "Coin Node" while the footer says "Wallet Fix" and carries a 2022 copyright, although the domain's own history begins roughly two years later. The headline figures of "50K+ active wallets", "200K+ resolved issues" and "100+ contributors" have no supporting source on the page and read as unverifiable social proof. The site also publishes no contact channel, so a user who loses funds would have no named party to approach. The behavioural sandbox did not capture an active drainer or clipboard hijack, and the page has no hidden forms. That absence does not offset the confirmed external detections, because a wallet-connection lure may only execute its harmful logic after a real wallet interaction. Evidence:
- Homepage: the service menu pairs wallet-restoration, token-claim, staking-harvest and withdrawal flows with a "Connect Wallet" call to action, and it shows no pricing or refund terms.
- Homepage footer: the "Wallet Fix © 2022" notice contradicts the "Coin Node" header and predates the domain's observed history.
- Reputation checks: the browser-protection service lists the site as social engineering, and 12 security engines rated it malicious with 2 more rating it suspicious.
- Domain history: the domain is about 2.6 years old, and the web archive holds 9 snapshots spanning 2024–2026 (3 years tracked, first seen February 2024).
Regulatory Verification Notes
The page identifies no operating legal entity, registered address, licence, registration number, terms of service or privacy policy. Ownership and governance are opaque. For a service that asks visitors to connect wallets and move assets, this lack of disclosure is substantial. Wallet-level token movement is normally accompanied by named responsible parties and complaint routes, and none exist here. The site belongs to the crypto-services category, where regulators increasingly expect custody and asset-handling services to be registered, and the site makes no claim of such authorisation. No third-party broker or regulatory-database record could be associated with the site, so there is no external regulatory context to weigh. The ownership opacity is an administrative finding. The confirmed external detections described above are what drive the risk assessment. Evidence:
- Homepage: no company name, address, licence, registration number or legal pages appear anywhere on the page.
- Hosting: the site is served from AS13335 (Cloudflare, Inc., US), a shared platform that discloses nothing about the site's operator.
- Transport encryption: the TLS certificate was issued by WE1 at DV level, valid to 2026-12-17. DV validates domain control only and says nothing about the operator.
What to Verify Next
Any contact with this site is premature while the confirmed detections stand. A user who has already visited should treat the wallet as potentially exposed. If a wallet was connected or a transaction signed, the user should review and revoke active token approvals using a reputable approval-management tool and move remaining assets to a freshly generated wallet. Anyone with a genuine wallet problem should go only to the official support channel of the wallet or protocol concerned, reached through an independently sourced route, never through a link or search result leading here. Seed phrases or private keys must never be entered in response to any prompt from this page. The user should also confirm the official support/contact channels of the project the site claims to serve, and confirm that the protocol is real, through an independent offline route. Evidence:
- Homepage: the "Connect Wallet", "Restore", "Recovery" and "Claim Airdrop Rewards" actions are the points at which approvals or key exposure could occur.
- Homepage: neither "Coin Node" nor "Wallet Fix" can be tied to a named, reachable organisation.
- Reputation checks: the confirmed social-engineering classification means this site should not be used as a verification or support route.
Summary Verdict
The site carries a critical, high-risk trust posture. Confirmed blacklisting by independent sources is reinforced by page content that matches a known wallet-lure pattern, and it is compounded by inconsistent branding and unverifiable claims. Nothing in the available evidence supports a legitimate-service reading, and the real-world operator remains unidentified.
Infrastructure Integrity
The site is delivered through Cloudflare's CDN and WAF platform, with a valid TLS certificate from a mainstream issuer, and only edge addresses are visible, so the origin host cannot be independently identified. These protections are standard on a shared hosting platform and are available to any publisher, including malicious ones. They are a minor mitigating factor and do not offset the confirmed external threat detections or the content-level risks.
Closing Assessment
The site should not be visited for any purpose that involves a wallet, and no wallet connection, signature, credential, seed phrase or payment should be given to it. Anyone who has already interacted with it should act promptly to secure their assets and report the page to the relevant browser-safety and hosting abuse channels.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, several checks together.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of mainetsapps.pages.dev.
- The request stayed on mainetsapps.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2024-02-26. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2f47 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-17 |
| Domain age | 2.64 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2024-02-26 |
| Archive snapshots | 9 |
| Reputation | VirusTotal: 12 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 1 match |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about mainetsapps.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.