Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
mrmigglesbase-appclaim.pages.dev shows high-risk / scam indicators.
| What this site appears to be | A memecoin promotion page for $MIGGLES on Base, presented as a community project tied to a cat mascot. It gives a contract address and buying steps and promotes an NFT collection and an airdrop claim. Its claims of burned liquidity, renounced ownership and charity donations are unverified, and the 'Claim Airdrop' CTA conflicts with its own statement that no airdrops occurred. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Listed as unsafeGoogle | Risk |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 2.2 years oldRegistered history | Clear |
| Web archive | Archived since 20245 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
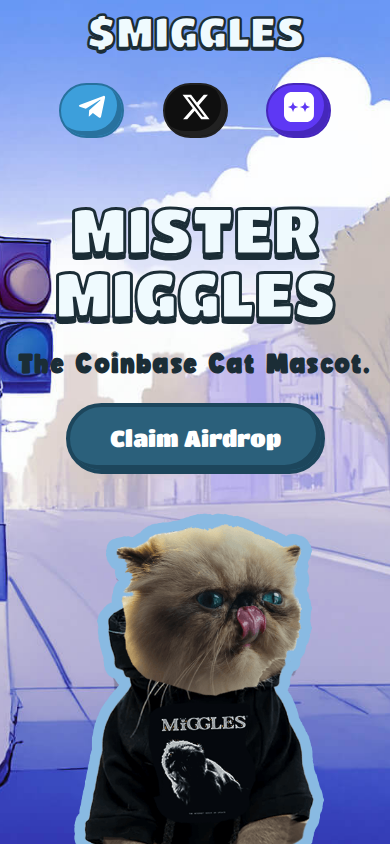
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: 1 to 3 years (registration continuity).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Google flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website is a single-page promotional landing site for a community memecoin called $MIGGLES on the Base blockchain. It is themed around a cat mascot, "Mister Miggles," and describes itself as a fan community project. It presents a token contract address, a "how to buy" walkthrough, a companion NFT collection and an airdrop-claim button. Its apparent purpose is to steer visitors into acquiring the token and NFTs through decentralized exchanges and wallet connections. The page describes no revenue model beyond a claim that part of the proceeds goes to feline charities.
Scam/Impersonation Risk
Contradictory signals are present and decisive. A major browser-safety service classifies the site under its social-engineering category, and several independent reputation engines flag it as malicious. Together these amount to a confirmed blacklist condition, and protective hosting does not offset it. The page content is consistent with that concern. The "Claim Airdrop" button, shown in the page header and elsewhere, contradicts the site's own story, which states the token had "no pre-sale, no KOLs, and no airdrops." Airdrop-claim prompts are a common lure for wallet-connection and approval abuse. The page presents "Liquidity: BURNED," "Ownership: RENOUNCED" and "0% taxes" as fact, but links no audit, lock record or on-chain proof. The team is anonymous, and an "Our Partner" entry cannot be verified. The page leans heavily on Coinbase and Base branding, including the tagline "The Coinbase Cat Mascot." A small disclaimer says the project is not affiliated with Coinbase or Base, which only partly offsets this. The hostname is also a free-hosting subdomain whose label combines the mascot name, the chain name and the word "appclaim," and it closely resembles that hosting platform's name. This is a typical pattern for disposable claim pages. No conflicting legal entities were observed, and no credential form was detected. However, the external reputation findings, the contradictory airdrop messaging and the unproven safety claims point to elevated risk for any wallet interaction. Evidence:
- Homepage: the "Claim Airdrop" call-to-action appears alongside the statement that no airdrops occurred.
- Homepage tokenomics block: burned liquidity, renounced ownership and 0% tax are asserted for a 1B-supply token without any audit or lock link.
- Homepage: the "Coinbase Cat Mascot" branding is paired with a non-affiliation disclaimer, and an unverifiable "Our Partner" entry appears.
- Domain provenance: the domain is about 2.2 years old, and the web archive holds 5 snapshots between 2024-08-22 and 2024-12-15 (1 year tracked).
Regulatory Verification Notes
The site is not a regulated financial service and claims no licence, registration number or supervisory authority. It names no operating company, and no identifiable operator appears anywhere on the page. The legal status of the token, the NFT collection and the charity pledge is therefore unverifiable from the site alone. The page claims that a portion of token and NFT proceeds goes to feline charities. It names no recipient and gives no accounting, so the claim has no documentary support. No third-party broker or regulator listing was found for this site. The reputational concerns above come from threat-detection sources, not from any licensing or regulatory finding. The site's identity could not be independently connected to a real-world brand or person. Evidence:
- Homepage: the site shows no company name, licence, registration number or legal-entity disclosure, and the team is anonymous.
- Homepage FAQ and story: the charity-donation claim names no recipient and gives no accounting.
- Transport and hosting: the TLS certificate is issued by WE1 (DV, domain validation only), valid to 2026-12-21, and the site is served from AS13335 (Cloudflare, Inc., US). A DV certificate confirms control of the domain, not the identity of its operator.
What to Verify Next
Any engagement should begin with independent confirmation that the token contract address matches the one published through official, separately sourced project and exchange channels. The airdrop claim needs the same independent check: whether any such campaign exists, and whether it is announced somewhere other than this page. The "burned liquidity" and "renounced ownership" statements should be checked directly against on-chain records and any third-party contract audit. The charity pledge should be confirmed with the named beneficiaries, if any are identified. The "Our Partner" entry, and any claimed link to Coinbase or Base, should be confirmed with those organizations through their own official channels. The community's Telegram and X links should be reached through a route independent of this page, and the project's support channels confirmed the same way. Evidence:
- Homepage: the contract address is published as plain text with a "Copy" control and no verification link.
- Homepage: the "How to buy" steps direct visitors to a wallet download and a decentralized-exchange swap.
- Homepage: the only community channels offered are Telegram and X, with no contact page or mailing address.
Summary Verdict
The assessment is critically low trust with elevated risk. Confirmed adverse external detections and contradictory on-page messaging outweigh the otherwise stable technical presentation. The site's real-world operator remains unverified. Valid encryption and consistent, successful page loads do not offset the reputational findings, and the site must be treated as a likely vehicle for social-engineering abuse.
Infrastructure Integrity
The site sits behind a mainstream CDN and web application firewall, and all observed addresses are edge servers. The origin server was not observable, so the real hosting location cannot be independently confirmed. This is a mitigating factor for availability and basic transport hygiene only, and it says nothing about the legitimacy of the content. Edge-only visibility also means page content could be swapped quickly without a change in network footprint.
Closing Assessment
At most, the site should be viewed read-only. No wallet should be connected, no transaction or token approval signed, no airdrop claimed, and no credentials or funds submitted through it. Anyone who has already interacted with it should review and revoke wallet approvals and move assets to a fresh wallet.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by governance, external reputation, page content.
01 Governance
- A threat feed lists this domain as malicious, and that caps the score whatever the other checks found.Governance
rule:GOV_CRITICAL_BLACKLIST
02 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
03 Page content
- The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 60% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of mrmigglesbase-appclaim.pages.dev.
- The request stayed on mrmigglesbase-appclaim.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2024-08-22. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2f38 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-21 |
| Domain age | 2.16 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2024-08-22 |
| Archive snapshots | 5 |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 1 match |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about mrmigglesbase-appclaim.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.