Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
noahdevs.com shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the registration record did not name the registrant and a form asks for sensitive details and sends them to a destination that could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
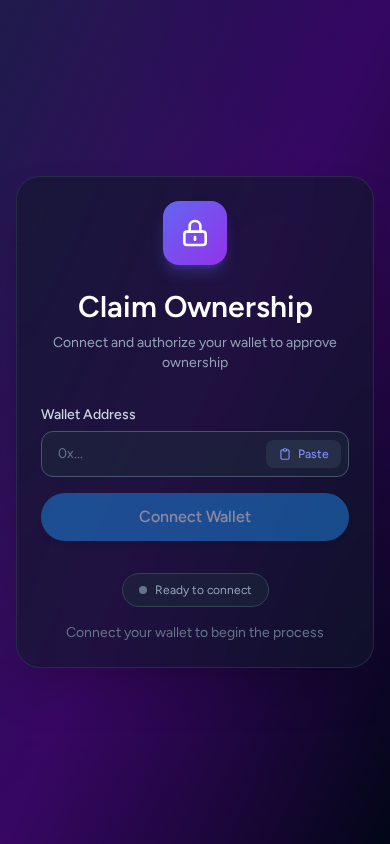
| How the site describes itself | A minimal page titled "Wallet Setup - Laravel" asks users to paste a wallet address, connect the wallet, and authorize a contract to "confirm ownership", with a possible gas fee. It gives no service description, legal identity, contact details, or explanation of the permissions being granted, which matches wallet-approval phishing. Risk is critical. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-11-04 and re-scored on 2026-11-05. The certificate, the registration age and the page content describe the site as it was on 2026-11-04.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 marked it maliciousVirusTotal; a single engine, not a confirmed listing | Watch |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports | Clear |
| Domain age | 6 months oldRegistered 2026-04-29 | Watch |
| Web archive | Archived since 20248 snapshots; the history predates the current registration (2026-04-29); an earlier owner may have held the name | Noted |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-04-29).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
This website is a single-page wallet-connection interface titled "Wallet Setup - Laravel". Under a "Claim Ownership" heading, it asks visitors to paste a wallet address, connect the wallet, and authorize a smart contract so that it can "confirm you are the wallet owner". It gives no product, service, price, or named operator. Its only apparent function is to induce a wallet approval, with value flowing to whoever controls the contract.
Scam/Impersonation Risk
The evidence converges on a wallet-approval phishing pattern, and the site is blacklisted by an external threat-intelligence source. The homepage's flow (paste an address, connect, authorize a contract, "might cost gas fee") presents a routine-sounding ownership check. It never says what permissions the contract receives, which is the structure typically used to obtain token-spending approvals and drain wallets. The page offers no audit, no named entity, and no explanation, which creates a sharp mismatch between a high-stakes action and the proof supplied. The generic framework-default page title suggests a reused template rather than a bespoke product. The page's structural fingerprint also matches that of another site already assessed as critical-risk, which further links it to a recycled kit. Three suspicious inline scripts and ad and analytics trackers were also observed on a page that otherwise has almost no content. Behavioral testing showed no clipboard hijacking, hidden forms, or cloaking, and all outbound network activity went to recognized destinations. These findings do not offset the core risk, because the harm here would occur through the user's own wallet approval. No brand impersonation or conflicting legal identities were observed; the contradiction is the blacklisting combined with the deceptive approval flow.
- Homepage: the form asks for a wallet address and a contract authorization "to confirm you are the wallet owner", with only a possible gas fee disclosed.
- Homepage: the page offers no description of what the approval grants, no operator name, and no contact channel.
- Reputation checks: an external threat-intelligence source lists the domain as blacklisted, with one engine flagging it as malicious and another as suspicious.
- Domain registration: registered 2026-04-29 (~0.5 years old). Only 8 archive snapshots exist, spanning 2024–2025 (2 years tracked), so the earlier archived history predates the current registration.
Regulatory Verification Notes
The site presents no legal pages, no corporate identity, no licence, and no registration number. For a page requesting wallet authorization, that absence is a material disclosure gap and not a minor omission. It also leaves no accountable party to whom a complaint, dispute, or recovery request could be directed. No third-party broker or regulatory record corresponds to the domain, and the site claims no licence. The disclosure gap is therefore best read as part of the evidence for an anonymous, unaccountable operation. The identity of the real-world operator remains unverified.
- Homepage: no company name, legal terms, privacy policy, address, or licensing statement is present.
- Registrar: the domain is registered through HOSTINGER operations, UAB, and the registration runs to 2027-04-29.
- Hosting and encryption: the site is served from AS47583 (Hostinger International Limited), and its TLS certificate is a DV certificate issued by YE2, valid to 2027-01-24. DV certification confirms control of the domain only, not the operator's identity.
What to Verify Next
Anyone who reached this page through a message, advertisement, or social post should confirm, through an independent channel, whether the claimed sender or project actually directed them here. Real "ownership" or "claim" processes are normally announced on a project's established official channels. Wallet holders who already connected should review their wallet's active token approvals on a block explorer and revoke any unfamiliar contract permissions. They should also move remaining assets to a fresh wallet if there is any doubt. Any official support or contact channel claimed in connection with this page should be confirmed through an independent, offline route.
- Homepage: the "Connect Wallet" and "Confirm" controls trigger a contract-authorization request that the page does not describe.
- Homepage: the prompt is framed as a one-step ownership confirmation, which no legitimate protocol requires through an unnamed site.
- Domain history: the registration is recent, so no long operating record exists to support the claim.
Summary Verdict
The overall posture is high risk. The deterministic assessment places this site at the bottom of the trust scale because of a confirmed external blacklisting combined with a deceptive wallet-authorization flow. The site offers no accountable operator, so nothing in the evidence supports legitimate use. A valid certificate and mainstream hosting do not change that conclusion.
Infrastructure Integrity
The domain resolves to two addresses in the hosting provider's own address space, with no CDN or WAF vendor detected in front of them. The only network-level anomaly is an unconfirmed heuristic flag for infrastructure fragmentation, which carries no weight against the verdict. The site's hosting is a mainstream commercial provider with valid transport encryption. This is a neutral technical fact and mitigates nothing, because the external threat detection stands independently of where the site is hosted.
Closing Assessment
Do not connect a wallet, sign any transaction, or enter credentials or funds on this site. If any wallet interaction has already occurred, revoke the approvals and move assets promptly. The page is suitable for read-only inspection only, in an isolated environment.
Written analysis generated 2026-11-05 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content, several checks together and code shared with sites rated critical.
01 External reputation
- Two VirusTotal engines, or one leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_MEDIUM
02 Page content
- A form on the page submits to a destination TrustSniffer could not verify.Page content
rule:PAGE_FORM_UNTRUSTED_DEST - The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 Code shared with sites rated Critical
- The site runs the same code, or has code wired to the same hidden endpoint, as other sites TrustSniffer rated Critical.Code shared with sites rated Critical
rule:KIT_SHARED_WITH_CRITICAL_SITE
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of noahdevs.com.
- The request stayed on noahdevs.com. It was not redirected to another domain. Clear
- Registered through HOSTINGER operations, UAB. Noted
- DNS for this domain is served by dns-parking.com, across 2 name servers. Noted
- The domain is registered until 2027-04-29. Noted
- The earliest public archive of this name is from 2024-08-20, before the current registration on 2026-04-29; an earlier owner may have held it. Noted
- It is hosted on AS-HOSTINGER, a network registered in GB; the provider, Hostinger International Limited, lists its country as CY. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 1 other site it has analysed. That site is rated Critical on its own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
| Shared files (SHA-256) | CDjGF7sZ.js 263932c95073af6f602102499788eef9cad5cb708af69c1415b5cde0978b9f4f |
|---|---|
| B_lyXhpy.js 3b8a87aa48541723a9d316938419ae9ecb213fb6a336cc670448178a5d217296 |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | HOSTINGER operations, UAB |
|---|---|
| Hosting | AS-HOSTINGER - Hostinger International Limited (the provider lists its country as CY) |
| Network registered in | GB |
| Server IP | 2a02:4780:a:598:0:a0c:470c:10 |
| Name servers | apollo.dns-parking.com, athena.dns-parking.com |
| CDN / edge network | Not detected |
| Resolved IP addresses | 2 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 2 |
| SSL issuer | YE2 |
| SSL expiry | 2027-01-24 |
| Domain age | 189 days (registered 2026-04-29) |
| Domain expiry | 2027-04-29 |
| Archive first seen | 2024-08-20 (2.2 years before capture) |
| Archive snapshots | 8 |
| Reputation | VirusTotal: 1 malicious | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
The web archive has records of this name from 2024-08-20, before the current registration on 2026-04-29. That archive history predates the current registration, and an earlier owner may have held the name.
About this assessment
A trust score summarises the evidence TrustSniffer could collect about noahdevs.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.