Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
pagfinance.xyz shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 10 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 29% confidenceAbuseIPDB, 8 reports; shared hosting inflates reports | Clear |
| Domain age | 4 months oldMost scam domains are under a year old | Risk |
| Certificate | Encrypted connectionIssued by YR2 | Noted |
| Hosted by | PONYNETServer in US | Noted |
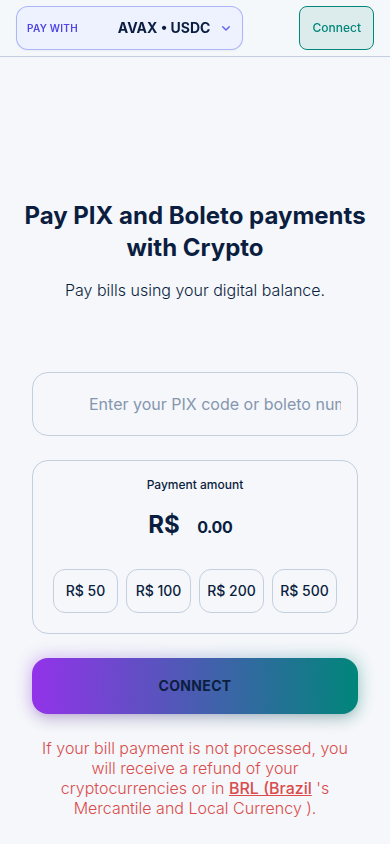
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
PagFinance is a single-page website whose homepage, titled "PIX com Cripto em segundos | PagFinance," presents itself as a service for converting PIX instant payments into cryptocurrency within seconds. It is written in Portuguese and aimed at Brazilian users. Its apparent purpose is a fiat-to-crypto payment or conversion service, a category in which visitors are asked to move money or share financial credentials.
Scam/Impersonation Risk
The evidence shows confirmed contradictions. Several major security vendors independently flag the domain as malicious, with additional engines rating it suspicious. The domain is blacklisted by external reputation sources, and the detection level is high enough to trigger a hard reputation cap that no other positive signal can offset. The domain was also registered only a few months ago. Together, a fresh domain, a financial-conversion pitch aimed at a specific national payment rail, and broad malicious detections are a recognised pattern for fraudulent payment and crypto-conversion fronts. The hosting IP also carries abuse reports from multiple distinct reporters. These reports relate to a shared provider address and are not discounted. The site's own behaviour was benign in sandbox testing: no external calls, no hidden forms, no wallet-connection prompts, no clipboard manipulation, and no cloaking. That does not outweigh the external detections, because a clean first-load profile is consistent with a lure page whose harmful stage appears later. No conflicting legal-entity identities and no direct brand impersonation were observed. The risk therefore rests on the reputation and blacklist evidence, not on an identified impersonated brand. Evidence:
- Homepage: the title and content offer PIX-to-crypto conversion "in seconds," a speed claim that gives no basis for assessing the operator.
- External reputation: 10 malicious and 2 suspicious detections, including three top-tier security vendors, with the blacklist condition active.
- Hosting IP 198.251.84.200 has 8 abuse reports from 7 distinct reporters, most recently within the past week.
- Domain registered 2026-06-30 (~0.34 years old, about 123 days), expiring 2027-06-30, through Dynadot.
Regulatory Verification Notes
The real-world operator is not independently verified. The captured homepage content does not make clear which legal entity runs the service or under what financial authorisation. For a service that would handle fiat-to-crypto flows, this is a verification gap. On its own it is not evidence of fraud, but here it sits alongside confirmed reputation contradictions. The site's claims should be treated as unproven. No third-party broker or regulator match was found to support them. The valid, long-dated encryption certificate shows only that traffic is encrypted. It says nothing about who operates the site or whether it is legitimate. Evidence:
- Homepage: no licensed-entity, registration or regulator information is evident in the captured text.
- Hosted on AS53667 (PONYNET – FranTech Solutions, US), registry ARIN.
- TLS certificate issued by YR2 (DV, domain validation only), valid to 2027-01-28 with about 88 days remaining.
- Identity verification status: unknown; no independent link to a real-world brand or person was established.
What to Verify Next
No sensitive interaction should proceed. Any claim of authorisation to offer PIX or crypto services should be checked directly with the relevant Brazilian financial and virtual-asset regulators, not through anything stated on the site. If a legal entity is named, its registration should be confirmed in the official corporate registry. The service should also be tested against an independently sourced, known-genuine brand of the same name. Official support and contact channels should be confirmed through an independent route. Any prior deposit, PIX transfer or credential submission to this domain should be treated as potentially compromised and reported to the payment provider. Evidence:
- Homepage: it offers instant PIX-to-crypto conversion without any visible operator or authorisation detail.
- The domain is under a hard reputation cap driven by multiple malicious detections.
- The hosting IP's abuse history is recent and ongoing.
Summary Verdict
The site carries an elevated, clearly cautionary risk posture. Confirmed external threat detections and a blacklist condition dominate the assessment. Supportive signals are limited to basic technical hygiene and benign sandbox behaviour, which cannot offset them. The operator's identity remains unverified, so no legitimacy can be inferred.
Infrastructure Integrity
The site is hosted directly on a US provider's network with no CDN or WAF layer. Its origin addresses are exposed and there is no edge protection. Infrastructure therefore provides no mitigation. The encryption certificate and stable, error-free responses are routine hygiene and do not change the reputation picture.
Closing Assessment
The site should not be used for login, credential entry, payments or any financial transaction. At most it should be viewed passively, from an isolated environment, and nothing should be downloaded from it. Anyone who has already interacted with it should secure the affected accounts and report the activity.
Written analysis generated 2026-11-01 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, hosting and network, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered between three and six months ago.Hosting and network
rule:DNS_YOUNG_6M
03 Registration and ownership
- The registration record withholds contact details for the operator.Registration and ownership
rule:KF_WHOIS_HIDDEN - Registration details are held behind a privacy service, so no operator is named publicly. This is common and legal, and it also means there is nobody to check.Registration and ownership
rule:KF_WHOIS_PRIVATE
Signals weighed against the site
- AbuseIPDB: 8 reports on hosting IP 198.251.84.200 (FranTech Solutions, Content Delivery Network), 29% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 15% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of pagfinance.xyz.
- The request stayed on pagfinance.xyz. It was not redirected to another domain. Clear
- Registration is published under DYNADOT LLC. Clear
- DNS for this domain is served by asurahosting.com, across 2 name servers. Noted
- The registration is paid up to 2027-06-30. Noted
- It is hosted on PONYNET, from a server in US. Noted
Domain intelligence
| Registrar | DYNADOT LLC |
|---|---|
| Hosting | PONYNET - FranTech Solutions, US |
| Country | US |
| Server IP | 198.251.84.200 |
| Name servers | NS5.ASURAHOSTING.COM, NS6.ASURAHOSTING.COM |
| CDN / edge network | Not detected |
| Resolved IP addresses | 2 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 2 |
| SSL issuer | YR2 |
| SSL expiry | 2027-01-28 |
| Domain age | 0.34 years (continuous registration) |
| Domain expiry | 2027-06-30 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 10 flagged | AbuseIPDB: 29% confidence, 8 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about pagfinance.xyz at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.