Verdict
The site's own pages showed several warning signs that deceptive sites commonly use, and together with the other checks they put it in the critical-risk band. Do not pay, sign in, or share personal details with this site.
starcvv.at shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the site asks visitors to sign in while its operator could not be verified and the registration lookup did not return the domain's registrant, creation date, expiry date and country. On its own this does not say who runs the site or that anything is wrong with it.
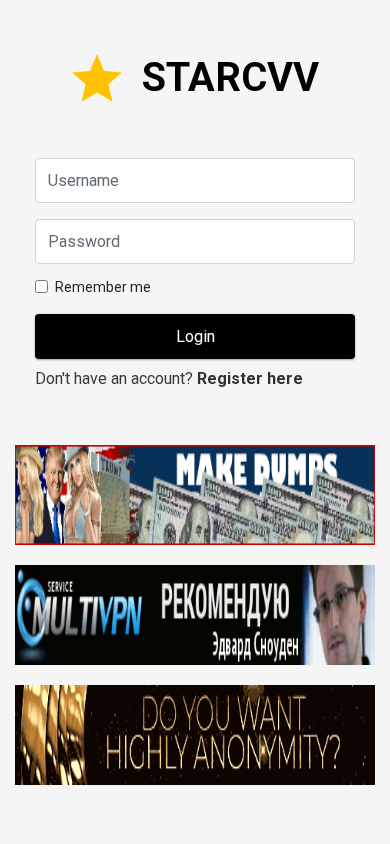
| How the site describes itself | STARCVV is a storefront that sells stolen credit card data (CVV, dumps, fullz) and advertises valid cards, refunds for non-working cards, and fresh stock. It has login and registration forms and no verifiable legal entity, address, contact channel, or licence, so it is a high-stakes illicit financial marketplace. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The real-world operator identity was not independently verified.
- These checks returned no result: domain expiry date (WHOIS).
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 7/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 marked it maliciousVirusTotal; a single engine, not a confirmed listing | Watch |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 4.6 years before captureWeb archive; the registration lookup returned no registration date | Clear |
| Web archive | Archived since 202262 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: 3 to 10 years before capture (web archive; the registration lookup returned no registration date).
- Public web-archive history exists since 2022.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
STARCVV is an online storefront that presents itself as a "CVV shop". It offers stolen payment card data, described on its pages as CVV records, "dumps" and "fullz". It shows a login and a registration form and links to related storefronts labelled "Trump Dumps", "Multi VPN" and "UAS Store". Its apparent business model is selling stolen card data to registered buyers, with a refund guarantee for cards that do not work. The site's pages mention bitcoin as the payment route, but they name no operator and describe no payment process.
Scam/Impersonation Risk
The site's own pages offer stolen financial data for sale, and this is the decisive finding of the report. The home page advertises "Updated every two days with more than 1 million CVV available" and "High valid CC guaranteed. Instant refund with checktime available". The page text is dense with search-style phrases such as "buy cvv fullz" and "buy bitcoin with cvv". Buying stolen card data is a crime in most countries, and shops of this kind commonly take payment and deliver nothing or deliver unusable data. The site anticipates this, writing that "it is hard to get a legit CVV site on the internet or darkweb because there are lot of scam website exists nowadays". Its claims to be the "most reliable CVV sites" and its "fresh cvv guaranteed" promise are unverifiable self-assertions that no page substantiates. The pages also contradict themselves on timing: the footer reads 2021, the home page carries a November 2022 date, the register page carries a November 2021 date, and "updated every two days" sits beside content labelled "Latest CVV 2021". This is the site's own stale and inconsistent material and weakens the freshness promise. No brand impersonation and no conflicting legal identities were observed, and the site's critical-risk assessment rests on what it offers rather than on contradictory identity claims. One external reputation engine flagged the site as malicious. That is a single signal and does not meet the standard of a confirmed listing, so it is noted as supporting context only. During page analysis, 12 outbound requests went to destinations TrustSniffer does not recognise, including form-style submissions, and roughly two-thirds of loaded files came from other domains. Both are scored findings.
- Home page: advertises "more than 1 million CVV" refreshed every two days, "High valid CC guaranteed", and refunds for most cards.
- Home page and register page: the site's own pages carry mismatched dates (footer 2021, home page November 2022, register page November 2021) and different page titles ("CVV SHOP | BUY CC" versus "BEST CVV SITES").
- Web archive: 62 snapshots between 2022-04-22 and 2026-10-24 (a 1,646-day span), with a longest gap of 69 days. This shows the storefront has been present for years, not that it is established or legitimate.
- External reputation check: 1 engine reported the site as malicious and none reported it as suspicious. Google Safe Browsing did not list it.
- Page behaviour: 12 requests, 9 of them background data calls, went to unrecognised destinations, and 65.2% of loaded files came from other domains.
Regulatory Verification Notes
A business that handles card or payment data would be expected to disclose a legal entity, a registration or licence, a regulator and terms or privacy terms. On the pages read (the home page, login page and register page), none of these four disclosures was present. The only disclosure of any kind was a refund statement on the home page. Identity is only partly evident. The site presents itself as STARCVV and offers a contact form, but no company name, address, or registration is given. The business model is inherently unlicensable, so the absence of regulatory credentials reflects the nature of the offering and not a gap that a licence lookup could close. No third-party broker or regulatory-database match was found for this name, and that absence is neutral context only.
- Home, login and register pages: no legal entity, registration or licence, regulator, or terms or privacy page was found on the pages read.
- Home page: the only disclosure found was "Refund is available for most of the CVV."
- Registration record: the domain is registered through Hosting concepts B.V. / Registrar.eu.
- Transport and hosting: served from AS13335 (Cloudflare, Inc., US), with a DV TLS certificate issued by WE1 and valid to 2027-01-17. A valid certificate only encrypts traffic and says nothing about the operator.
What to Verify Next
Verification here should aim to confirm the risk, not to establish the operator's credibility. Anyone assessing a connection with this site should treat any claim of "valid" cards or refunds as unverified. Any payment instruction would be an unverifiable transfer to an undisclosed party. Organisations should check whether card data issued by their own institution, or credentials of their own customers, appear in sales listings of this kind. If so, they should alert the relevant card issuer or fraud team through its official channels. Reports of illicit card-data shops can also be passed to national cybercrime authorities. Any official contact channels for an organisation should be taken from that organisation's own independently sourced materials, not from this site.
- Home page: the site states that it sells card data, so the verification need centres on protecting cardholders and not on authenticating a seller.
- Register page: a registration form is offered with no accompanying legal, privacy or terms page on the pages read.
- Login page: the sign-in form collects account details with no disclosed operator behind it.
Summary Verdict
STARCVV carries a critical risk assessment. The site's own pages describe a marketplace for stolen payment card data, and the signals that normally support legitimacy (a working certificate, a multi-year archive presence) do not offset that. Available evidence is consistent with an illicit storefront, and no evidence supports treating it as a lawful business.
Infrastructure Integrity
The site is delivered through Cloudflare, and all four observed addresses are edge addresses, so no origin address was observable. TrustSniffer treats this as a neutral condition that neither reduces nor adds to the risk. The host address showed no abuse reports, but that record is shared across the provider's customers and carries no weight for this site's legitimacy.
Closing Assessment
The site should not be used. No account should be registered, no cryptocurrency or other payment sent, and no personal or card details entered. Anyone who believes a card or account of theirs appears in a listing of this kind should contact the card issuer or bank through its official channels and consider reporting it to the relevant cybercrime authority.
Written analysis generated 2026-11-10 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
17 findings contributed to this verdict, raised by page content, several checks together, behaviour in a sandbox, and registration and ownership.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - A sign-in path on this site handles sensitive information.Page content
rule:PAGE_LOGIN_PATH_SENSITIVE - The page presents a sign-in form, and the operator behind it could not be independently verified.Page content
rule:PAGE_TYPE_LOGIN_UNVERIFIED - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
02 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK - No external threat source confirms a listing for this site, but its own page content reads as risky.Several checks together
rule:HYB_POSITIVE_EXTERNAL_NEGATIVE_PAGE
03 Behaviour in a sandbox
- A large share of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_MODERATE - The page exchanged network traffic with destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_TRAFFIC - The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS - The page made background requests to destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_XHR - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
04 Registration and ownership
- The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY - The registration lookup did not return the domain's registrant, creation date, expiry date and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:STARCVV
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of starcvv.at.
- The request stayed on starcvv.at. It was not redirected to another domain. Clear
- Registered through Hosting concepts B.V. / Registrar.eu ( https://nic.at/registrar/648 ). Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The earliest public archive of this site is from 2022-04-22. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Hosting concepts B.V. / Registrar.eu ( https://nic.at/registrar/648 ) |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3037::6815:fb5 (a CDN edge address; the server behind it was not observed) |
| Name servers | ben.ns.cloudflare.com, mallory.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-17 |
| First seen (web archive) | 4.55 years before capture; the registration lookup returned no registration date |
| Domain expiry | Not available |
| Archive first seen | 2022-04-22 (4.6 years before capture) |
| Archive snapshots | 62 |
| Reputation | VirusTotal: 1 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about starcvv.at at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.