Verdict
External threat listings named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
v3-morpho.com shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
| How the site describes itself | Morpho's home page presents a non-custodial, Ethereum-based lending and borrowing protocol where users supply assets to curated vaults to earn yield or post collateral to borrow. It cites audits, open-source contracts, curator risk teams, and a DeFi risk warning. It names no legal entity, registration, regulator, or physical address, and the network list conflicts across pages. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- External threat sources confirmed a listing for this site when the evidence was captured (VirusTotal, a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-24)). On its own it would limit the score to at most 24; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
- These checks returned no result: web archive lookup.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe confirmed external listing ceiling (at most 24) and the threat-listing ceiling (at most 5) also apply, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 16 marked it malicious, 2 suspiciousVirusTotal; Fortinet, Kaspersky, Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 7 months oldRegistered 2026-04-23 | Watch |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
| Hosted by | CLOUDFLARENETNetwork registered in US | Noted |
The page as captured
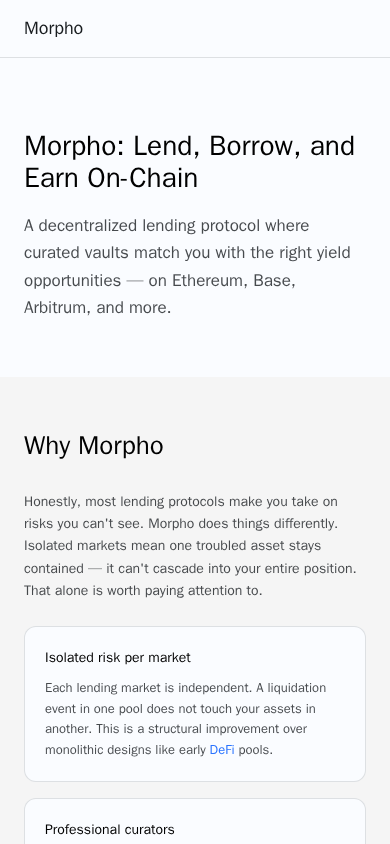
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year at capture (registered 2026-04-23).
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
16 VirusTotal engines, including Fortinet, Kaspersky, Sophos, marked this site as malicious; independent sources confirm a listing for this site.
Overview
The website at v3-morpho.com presents itself as a non-custodial lending and borrowing protocol called Morpho, aimed at crypto users. Visitors are invited to connect an EVM wallet, supply assets to curated vaults to earn yield, or post collateral to borrow. The site says it spans Ethereum, Base, Arbitrum and Monad, and that its own pages carry a DeFi risk warning. It is an investment-style DeFi front end built around depositing assets before any service is received, and its domain name embeds the name of the established Morpho lending protocol.
Scam/Impersonation Risk
This site carries critical risk. The domain combines "v3" with the name of a known lending protocol, and the site is not shown to be that protocol's operator. A threat-intelligence listing classes the site as an active distributor of phishing, last seen on 24 October 2026. Many independent security engines also rated the address malicious, including three leading vendors. Together these meet the bar for a confirmed listing, and no engine verdict clears the site. The site's own copy is polished and plausible. It cites professional curators (Gauntlet, Steakhouse Financial and Sentora), claims "multiple independent security audits", promises that users can "Deposit and start earning" with yield that "accumulates block by block", and asserts "$2B+ Total Value Locked across all vaults and networks" with "60+ vaults". None of these claims is sourced or dated on the pages read. The curator names are the site's own assertions. The tokens it mentions (ETH, USDC, USDT, wstETH, cbBTC) are standard, familiar assets that lend credibility to the presentation. A newly registered look-alike domain that asks visitors to connect a wallet and deposit assets presents a direct risk of loss. The score reflects the accumulation of scored findings rather than any single item. These include the confirmed listing, the deposit-before-service model, and a page dominated by crypto-token content. They also include nearly all page files loading from other domains, data being sent to destinations TrustSniffer does not recognise, and missing page metadata and structured data. The page captured showed no login or sensitive-data form.
- VirusTotal: 16 engines rated the address malicious and 2 suspicious, including Fortinet, Kaspersky and Sophos. Safe Browsing did not list it.
- Threat-intelligence listing: the site is classed as a phishing actor, last seen 2026-10-24.
- Homepage behaviour capture: 97.1% of files loaded from other domains, and 3 requests sent data to 3 destinations TrustSniffer does not recognise.
- Registration record: registered 2026-04-23 (201 days at capture).
Regulatory Verification Notes
On the pages read (the homepage, the info page and the questions page), the site names no legal entity, registration, regulator or physical address. The only identity it offers is the label "V3 Morpho", which is consistent with a real-world connection but is not verified. The homepage does carry a clear DeFi risk warning (smart contract bugs, oracle failures, market volatility). It also states that performance fees are set at vault level and shown before deposit. On the pages read, no contract address and no terms or privacy page appeared, although the site says its contracts are open source and readable on-chain. The site's own pages contradict each other on fees: the homepage says the protocol takes a small share of interest, while the info page says the full rate passes to both sides. The Monad network is presented as live on the homepage and as a testnet in the FAQ. The info page names Optimism and Base as L2s and omits Arbitrum, which the homepage lists. The audits are described as public and multiple, but no auditor names or report links appear on the pages read. No third-party broker or regulatory record matched this site, and the absence of such a record is not itself a finding.
- Homepage: the DeFi risk warning and the vault-level fee statement are present. The $2B+ and 60+ vault figures carry no source or date.
- Info and questions pages: the full-rate-to-both-sides fee statement and the Monad testnet reference conflict with the homepage.
- Pages read: no contract address and no terms or privacy page.
- Hosting and transport: served from AS13335 (Cloudflare, Inc., US), and the TLS certificate seen at capture was DV-issued by YE1 and valid until 2027-02-02. This shows the site is encrypted and says nothing about the operator's legitimacy.
What to Verify Next
Any interaction with the real Morpho protocol should start from an address obtained through an independent route, such as the protocol's established public channels, not from this domain or links on it. Contract addresses shown here should be compared against those published by the protocol's verified sources before any wallet connection is considered. The audit claims, the curator relationships and the stated TVL should be confirmed with the named auditors and curators directly. Confirming that this domain is an official property would also settle the matter. Absent that confirmation, the evidence points away from it.
- Homepage: the audit, curator and TVL claims carry no reference that can be checked from the pages read.
- Homepage: the wallet-connection flow (MetaMask, Coinbase Wallet, WalletConnect) is the point at which assets would be put at risk.
- Registration record: the domain was registered 201 days before capture through the registrar Atak Domain.
Summary Verdict
The available evidence places this site at critical risk. It is an unverified, recently registered look-alike of an established protocol brand, and independent security sources have confirmed it as a threat. The professionally written content does not offset those findings, and the identity the site presents is not independently verified.
Infrastructure Integrity
The site resolved to four Cloudflare edge addresses on a US-registered network, and the origin server was not observed. This is a neutral fact: using a CDN says nothing for or against the operator, and it neither mitigates nor aggravates the other findings. The abuse record for the host address was checked and showed no reports. That record belongs to a shared provider address, so it says little about this particular site.
Closing Assessment
The site should not be used for connecting a wallet, approving transactions or depositing any assets. Anyone who has already interacted with it should review and revoke any wallet approvals granted to it. Access to the genuine Morpho protocol should come only through its officially published channels.
Written analysis generated 2026-11-10 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
7 findings contributed to this verdict, raised by external reputation, page content and behaviour in a sandbox.
01 External reputation
- 16 VirusTotal engines marked this domain as malicious when the evidence was captured, which TrustSniffer counts as a confirmed external listing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Behaviour in a sandbox
- Most of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:V3 Morpho
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of v3-morpho.com.
- The request stayed on v3-morpho.com. It was not redirected to another domain. Clear
- Registered through Atak Domain. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-04-23. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Atak Domain |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3035::6815:2e08 (a CDN edge address; the server behind it was not observed) |
| Name servers | aida.ns.cloudflare.com, sergi.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2027-02-02 |
| Domain age | 201 days (registered 2026-04-23) |
| Domain expiry | 2027-04-23 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 16 malicious, 2 suspicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about v3-morpho.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.