Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
vaurex.co shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the registration lookup did not return the domain's registrant and country and the site asks visitors to sign in while its operator could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | Vaurex is a no-KYC anonymous token swap front end that asks visitors to connect a wallet, including by entering a 12–24 word Secret Recovery Phrase. It discloses no operator, legal entity, registration, regulator, contact channel, address, fees, or audit report, and its only policy link is 'Terms'. The seed-phrase entry combined with a financial swap and no verifiable proof of identity is a high-stakes evidence gap. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- External threat sources confirmed a listing for this site when the evidence was captured (VirusTotal, a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-24)). On its own it would limit the score to at most 24; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe independent sources ceiling (at most 24) and the threat-listing ceiling (at most 5) also apply, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 2 marked it malicious, 3 suspiciousVirusTotal; Fortinet among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 55% confidenceAbuseIPDB, 78 reports; shared hosting inflates reports | Risk |
| Domain age | 5 months oldRegistered 2026-05-30 | Risk |
| Web archive | Archived since 20261 snapshot; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
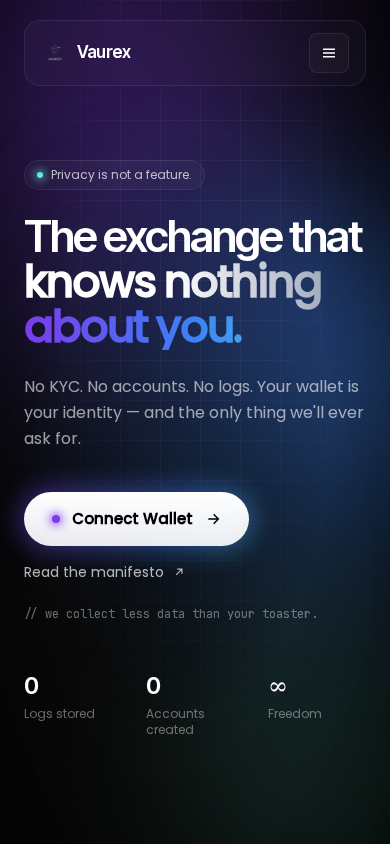
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-05-30).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
2 VirusTotal engines, including Fortinet, marked this site as malicious; independent sources confirm a listing for this site.
Overview
Vaurex is a single-page crypto front end that presents itself as an anonymous, no-KYC "exchange that knows nothing about you." Under the slogan "Trade without permission," it offers a wallet-connect swap interface for ETH, USDC, BTC and SOL, with a demonstration quote of 1.250 ETH for 2,524.78 USDC. Its apparent business model is custody-free token swapping paid from a visitor's own wallet. The site discloses no fee schedule or revenue source, so its monetisation cannot be established from the page.
Scam/Impersonation Risk: Contradictory signals are present, and the assessment is critical risk. A threat-intelligence listing classifies the site as the actor distributing phishing content, last seen on 24 October 2026. Independent reputation engines also flagged the domain, including a leading security vendor. Two independent sources, the threat-intelligence listing and VirusTotal, confirm the listing, so it meets TrustSniffer's bar for a confirmed listing. The homepage's own content is consistent with this. Its "Connect manually" option asks the visitor to type a 12-, 15-, 18-, 21- or 24-word Secret Recovery Phrase directly into the page. Anyone who submits that phrase gives up full control of the wallet, whatever the page says about keys. The site's own pages state "Your keys never touch our servers. We can't freeze, seize, or lose what we never held," and also state "We don't have a form." The same page contains a recovery-phrase entry form. The page also advertises "0 logs" and "0 accounts" counters and the line "we collect less data than your toaster," and none of these can be checked. Sandbox runs showed the page making heavy outbound data requests, including to some destinations TrustSniffer does not recognise, and rewriting its own content extensively after interaction. These are scored findings, so the page's behaviour cannot be called clean. The page layout also matches a template used by other sites previously rated critical. No brand impersonation was identified.
Regulatory Verification Notes: On the only page read, the homepage, a business of this type would be expected to show a legal entity, a registration or licence, pricing or fees, a policy page and contact channels. The homepage links only to "Terms." The legal entity, the licence or registration, the fees and the contact channels were all missing on the page read. The site names "Vaurex" as its brand, but this is an on-site claim that nothing independent verifies. No operator, regulator or audit report is attached to it. The site also makes jurisdiction-defying statements: "execution that doesn't care what jurisdiction you're in" and "your government called. we ignored them." A financial-exchange service that advertises regulatory avoidance and discloses no accountable party gives a user no recourse if funds are lost.
What to Verify Next: The checks below are for confirming the findings, not for making the site safe to use. First, search the registers of any financial or virtual-asset regulator in the relevant jurisdiction for a service called Vaurex. Second, ask whether any audit or source code exists outside the site, since the "Open source" claim is not backed by a repository, auditor or report on the page. Third, confirm any support or contact channel offline, through a route not published on the site. Fourth, never reach the service through a link from this page. Use only wallet providers' own official sites, found independently, for anything involving a wallet.
Summary Verdict: The overall posture is critical risk. Confirmed external listings, the site's own self-contradictory security claims and its request for a wallet's master secret converge on the same conclusion. The evidence is consistent with a phishing or wallet-draining front end. The site does not merit trust for any financial or sensitive interaction.
Infrastructure Integrity: The site resolves to a single address on Amazon's network, with no CDN detected. This is neutral and does not offset the findings above. TrustSniffer checked the host address's abuse record and found 78 abuse reports. These apply to a shared provider address, so they cannot be attributed to the site alone. The valid DV certificate and a recognised network show only that the site is technically operational. They say nothing about its intent.
Closing Assessment: Do not connect a wallet, enter a recovery phrase, sign transactions or send funds through this site. Anyone who has already entered a recovery phrase should treat that wallet as compromised. They should move any assets to a newly created wallet immediately.
- Threat-intelligence listing: the site was classified as a phishing actor, last seen 2026-10-24.
- VirusTotal: 2 engines rated the domain malicious and 3 suspicious, including Fortinet.
- Homepage: one sensitive form, a Secret Recovery Phrase entry with word-length options of 12, 15, 18, 21 and 24.
- Sandbox behaviour: 38 outbound requests sent data to other hosts, 3 of them to unrecognised destinations, and 3,253 page changes were recorded after interaction.
- Registration record: the domain was registered on 2026-05-30 through Tucows Domains Inc., 164 days old at capture, with an expiry of 2027-05-30.
- Web archive: a single snapshot, dated 2026-07-04 (span 0 days), so there is no extended operating history.
- Hosting: served from AS16509 (AMAZON-02, Amazon.com, Inc.).
- Transport encryption: a TLS certificate issued by YE1 (DV, domain validation only) was valid until 2026-12-26 at capture.
- Homepage "Audits" entry: it reads only "Open source," with no auditor name, report or repository link.
- Homepage claim: "Your funds remain in your control — we are never a counterparty." No fee, route or execution party is shown in the swap flow.
- Homepage jurisdiction statements: the site's wording sets no jurisdiction or accountable entity.
Written analysis generated 2026-11-10 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
19 findings contributed to this verdict, raised by external reputation, page content, several checks together, code shared with sites rated critical, history in the web archive, hosting and network, behaviour in a sandbox, and registration and ownership.
01 External reputation
- 2 VirusTotal engines, including a leading vendor (Fortinet), marked this domain as malicious when the evidence was captured.External reputation
rule:EXT_BLACKLIST_HIGH - The server address behind this site has a strong record of abuse reports.External reputation
rule:EXT_ABUSEIP_SEVERE - An external threat signal for this site is backed up by something the analysis observed on its own.External reputation
rule:EXT_THREAT_CORROBORATED
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 Code shared with sites rated Critical
- The site runs the same code, or has code wired to the same hidden endpoint, as other sites TrustSniffer rated Critical.Code shared with sites rated Critical
rule:KIT_SHARED_WITH_CRITICAL_SITE
05 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
06 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, three to six months before capture.Hosting and network
rule:DNS_YOUNG_6M
07 Behaviour in a sandbox
- The page replaced a large part of its own content during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION - The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY
08 Registration and ownership
- The registration lookup did not return the domain's registrant and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE - The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
Signals weighed against the site
- AbuseIPDB: 78 reports on hosting IP 75.2.60.5 (AMAZON-02), 55% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:Vaurex
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of vaurex.co.
- The request stayed on vaurex.co. It was not redirected to another domain. Clear
- Registered through Tucows Domains Inc. Noted
- DNS for this domain is served by njalla.no, across 3 name servers. Noted
- The domain is registered until 2027-05-30. Noted
- The earliest public archive of this site is from 2026-07-04. Watch
- It is hosted on AMAZON-02, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 2 other sites it has analysed. All 2 are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
| Shared files (SHA-256) | eth.js 278e929d41fea29ce790e5fdd066fb3e61c833e97dc597315064b1e3c8f5b79e (3 sites) |
|---|---|
| main.js 388974113b19ff2b7b084deb9c040f02c431a0b061cc1b8c72394b47fcbe6285 (3 sites) | |
| w-modal.js 6ac7e7f391409f0a3ccdfa2d0e70d0355dc218f86cc2ba638ed31d1b03ee89bb (3 sites) | |
| style.css d18eddca51577aad8927acf0c365637984e1529e2dc8824e5d8fd46fa17384eb (3 sites) |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Tucows Domains Inc. |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc. |
| Network registered in | US |
| Server IP | 75.2.60.5 |
| Name servers | 1-you.njalla.no, 2-can.njalla.in, 3-get.njalla.fo |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-26 |
| Domain age | 164 days (registered 2026-05-30) |
| Domain expiry | 2027-05-30 |
| Archive first seen | 2026-07-04 (129 days before capture) |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 2 malicious, 3 suspicious | AbuseIPDB: 55% confidence, 78 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about vaurex.co at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.