Verdict
This assessment found strong scam indicators on the site itself. Do not pay or share personal details with this site.
velarteam.online shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: the registration lookup did not return the domain's registrant and country. That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| How the site describes itself | Velar is a Bitcoin DeFi landing page promoting a DEX with leveraged perpetual trading (up to 20x), liquidity pools that earn trading fees, staking of the VELAR token, and a launchpad. It names two audit firms and investor backers, but gives no legal entity, registration, regulator, physical address, or risk warning. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-10 and re-scored on 2026-11-11. The certificate, the registration age and the page content describe the site as it was on 2026-11-10.
- One external source flagged this site when the evidence was captured (a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-23)). No second source confirms it. The alert is from the evidence captured on 2026-11-10; it was not re-queried for this version and is treated as unconfirmed. On its own it would limit the score to at most 49; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
- These checks returned no result: web archive lookup.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 2/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe unconfirmed alert ceiling (at most 49) and the threat-listing ceiling (at most 5) also apply, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | None flagged itVirusTotal | Clear |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 5 months oldRegistered 2026-06-18 | Risk |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETNetwork registered in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-06-18).
- No flags from the reputation services TrustSniffer consulted when the evidence was captured.
Full analysis
Overview
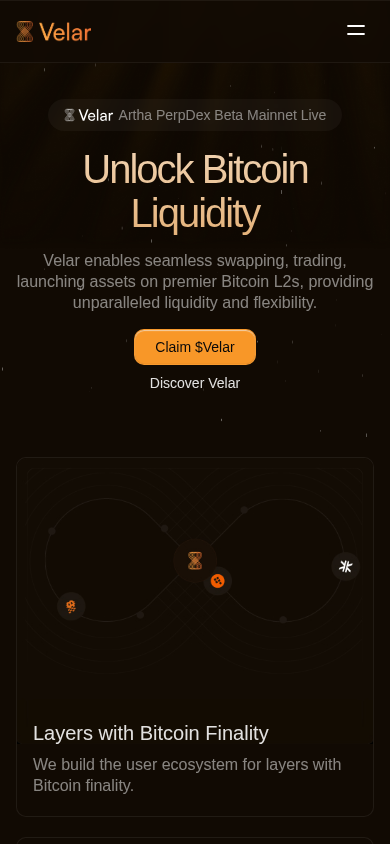
Velar, served from the domain velarteam.online, is a single-page marketing site for a Bitcoin-layer DeFi platform. It presents a decentralised exchange for swaps, a perpetual-futures product advertised with 20x leverage, liquidity pools that pay providers a share of trading fees, staking of its VELAR token, and a token launchpad. The apparent business model is fee and reward generation from users who deposit crypto assets to trade, provide liquidity or stake.
Scam/Impersonation Risk
No identity contradictions, brand impersonation or corroborated third-party flags were observed. The site presents consistently under a single name, and the analysis detected no impersonation of another brand. Even so, the site carries critical risk, driven by several separate signals. First, a single third-party threat-intelligence source carries a soft warning that classes the site as a phishing actor, last seen on 23 October 2026. This is a reputation note, not a confirmed finding. It is discounted because no other source corroborated it. Major scanning engines reported nothing malicious or suspicious, and Google Safe Browsing did not list the site. The captured page also contained no login or password form, only a newsletter form. The warning is therefore a notable signal that stands alone. It is shown here in full and is not treated as proof of phishing. Second, the domain was registered only recently, and its page build shares a fingerprint with another site assessed as critical risk. Third, the site's own pages contradict each other. The banner announces "Artha PerpDex Beta Mainnet Live", but the Perpetual DEX product is labelled "Coming Soon". The launchpad and bridge are also marked "coming soon", yet the page invites projects to launch on Bitcoin now and describes the DEX as live with pools and staking. These statements may not all be wrong, but a visitor cannot tell from the page which products actually operate. Fourth, the page's behaviour is a scored concern. It generated a large volume of traffic to other hosts, including destinations TrustSniffer does not recognise, loaded most of its files from other domains, and produced frequent console errors. The business model requires deposits before any service is delivered. The page offers up to 20x leverage and fee and reward earnings, and it carries no risk warning. It also makes scale claims it does not support, such as a Bitcoin TVL "over $1 trillion, around 45%" of a larger total. This implies a market tailwind, not any measured performance of the platform.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Third-party threat-intelligence warning (soft, uncorroborated): one source classed the site as a phishing actor, last seen 2026-10-23, with no other source confirming it. VirusTotal engines reported 0 malicious and 0 suspicious, and Google Safe Browsing did not list it.
- Homepage: the banner "Artha PerpDex Beta Mainnet Live" sits alongside Perpetual DEX, Launchpad and Bridge labelled "coming soon". The page also advertises 20x leverage and fee-earning liquidity pools with no risk warning.
- Behavioural sandbox: 38 requests sent data to other hosts, 22 of them to destinations TrustSniffer does not recognise. 61.4% of files loaded from other domains, and 33 console errors were recorded.
- Registration record: domain registered 2026-06-18, 145 days old at capture.
Regulatory Verification Notes
On the single page read, the homepage, the site links to Terms of Use, which is the only expected disclosure found. For a platform that takes leveraged trades, liquidity deposits and staking, no legal entity, registration, regulator, physical address, risk warning or smart-contract address appeared on the pages read. The site claims audits by Strata Labs and CoinFabrik and says it is "backed by incredible investors", but it names no investors and links no verifiable audit reports. It names a co-founder, Alexei Zamyatin, described as "Co-Founder of BoB", and offers a Discord community and a contact form as its contact channels. These are the site's own claims and do not independently establish who operates it. The fee language ("swap with minimal fees") gives no actual figures. Identity is rated as likely, not verified. The signals behind that rating are the organisation name Velar, a contact form and on-site identity details. The registration record lacks registrant and country fields. No regulatory status was found for the site, and no third-party broker record matched it.
- Homepage: Terms of Use link present. Contract address and risk warning not found on the pages read. Audit claims (Strata Labs, CoinFabrik) and the unnamed investor backing are unsupported by linked reports.
- Registration record: registered through NAMECHEAP INC on 2026-06-18, expiring 2027-06-18. Registrant and country fields were missing from the record.
- Hosting and transport: served from AS13335 (CLOUDFLARENET, Cloudflare, Inc., US). The TLS certificate seen at capture was issued by WE1 at DV level and valid until 2027-01-12.
What to Verify Next
The audit claims should be checked by locating the published reports directly with the named audit firms. The reports should name the contract addresses and cover the exact products offered here. Contract addresses for the exchange, pools and staking should be obtained from a source independent of this site, such as the project's publicly documented repositories, and matched against on-chain records. Whether velarteam.online is the project's official domain should be confirmed through a channel that does not start from this page. The named co-founder's connection to the project and the claimed investors should be confirmed through those parties' own communications. It should also be confirmed whether the products marked "coming soon" are live, and whether the single phishing listing, last seen on 2026-10-23, has since been withdrawn or has been matched by any other source.
- Homepage: audit claims name two firms but link no reports visible on the pages read.
- Homepage: contract address not shown on the pages read.
- Homepage: contact channels limited to Discord and a contact form, so official channels should be confirmed independently.
Summary Verdict
The site sits in the critical-risk band. A newly registered domain, a high-stakes deposit-based business model, an absence of operator and risk disclosures, product claims that conflict across its own pages and a heavy third-party traffic profile together outweigh the technically valid certificate and clean results from major scanners. The single uncorroborated third-party phishing warning is a soft reputation note and contributes less weight than these. The available evidence is consistent with the operator being the project it names, and identity is rated likely, but this is not established.
Infrastructure Integrity
The site is fronted by Cloudflare, and all four observed addresses are edge addresses, so the origin server could not be seen. This is neutral. It confirms the site is served through a mainstream provider but says nothing about the operator or the content behind it. A request to the host's abuse record returned no reports.
Closing Assessment
Committing funds in any form is premature until the contract addresses, audit reports and official domain have been independently confirmed. Until then, reviewing the public information is the proportionate level of engagement.
Written analysis generated 2026-11-11 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
18 findings contributed to this verdict, raised by code shared with sites rated critical, page content, hosting and network, behaviour in a sandbox, and registration and ownership.
01 Code shared with sites rated Critical
- The site runs the same code, or has code wired to the same hidden endpoint, as other sites TrustSniffer rated Critical.Code shared with sites rated Critical
rule:KIT_SHARED_WITH_CRITICAL_SITE
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The page title is only a few characters long, which tells a visitor little about the site.Page content
rule:PAGE_TITLE_GENERIC - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, three to six months before capture.Hosting and network
rule:DNS_YOUNG_6M
04 Behaviour in a sandbox
- The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - A large share of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_MODERATE - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH - The page exchanged network traffic with destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_TRAFFIC - The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS - The page made background requests to destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_XHR - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
- The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
05 Registration and ownership
- The registration lookup did not return the domain's registrant and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:Velar
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of velarteam.online.
- The request stayed on velarteam.online. It was not redirected to another domain. Clear
- Registered through NAMECHEAP INC. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-06-18. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
The same site on another domain
This site serves the same 20 distinctive code files as unclaimedsolana.net, which TrustSniffer has also analysed and rates Critical on its own evidence. Matching this many files means the two are one build published on two domains, or one is a copy of the other.
It does not by itself show who operates them.
| Shared files (SHA-256) | Bd9iBqSP.js 04439413f869742d16d531ef2bc2c6cb85693aa4bcc5ae1d621f18acc389b0f3 |
|---|---|
| D_Bm0cRX.js 2b4518e6e59dd8ca2b7f319bd62fe01cf00096a53c94b4cb66340f2684790551 | |
| s8zDI9DO.js 31f0baf1139db495744435502ba08f50a59a4b8a9976330445d195b9a5fcb82e | |
| BM83MYy6.js 33afad166500eea8395463c6534d4d556c7f4c23c031831fd7bb5b9a32cb67b3 | |
| BN-kvb7a.js 509daa0d4d7691cdfb3db9258af83c4d0ad470596c0a7b2f8c725e026936c286 | |
| BwcqZYul.js 52eb336b7f1b5792acbd89b3f248914d80f4933d02c6f632cb2a1c1846df2ff2 | |
| ySsYoSRz.js 5d87ef551f7a8a4a5e0e24c3c59791c648149bffc1ddd47940cb73ed2da50a49 | |
| De0fwC6A.js 60136d6ad7938fef7229608c577f5050a74ea6b83f3cbe5136d560a0ba88142f | |
| CLeNqVAl.js 72944dd21932556888c29076880ca33b98bcb28153c7fb9284f35f4d0c2df627 | |
| DSgKiq2E.js 8b65298ee00e5402079745de695c789b8d9fcf3c5db9a26daf3058e528378328 |
Showing 10 of the 20 shared files. The others are kept in TrustSniffer's record of this analysis.
Domain intelligence
| Registrar | NAMECHEAP INC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3033::6815:518 (a CDN edge address; the server behind it was not observed) |
| Name servers | elaine.ns.cloudflare.com, jihoon.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-12 |
| Domain age | 145 days (registered 2026-06-18) |
| Domain expiry | 2027-06-18 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about velarteam.online at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.