Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
authorize-cvv.in shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the site asks visitors to sign in while its operator could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A login and registration gateway for a shop named "CC Shop" that advertises CVV and fullz packages with credit scores. These are stolen payment card and identity data, so the site is a criminal marketplace. No legal identity, contact channel, or legitimate product information is shown. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-13 and re-scored on 2026-11-15. The certificate, the registration age and the page content describe the site as it was on 2026-11-13.
- The real-world operator identity was not independently verified.
- These checks returned no result: CDN / edge network lookup, web archive lookup.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 2/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports | Clear |
| Domain age | 4 months oldRegistered 2026-07-22 | Risk |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETNetwork registered in US | Noted |
The page as captured
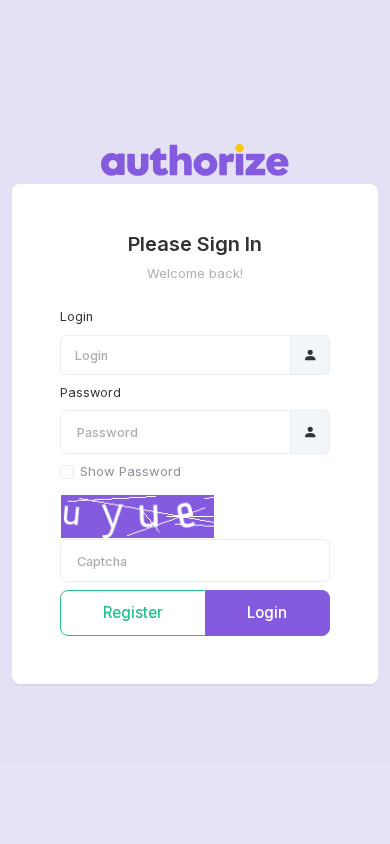
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-07-22).
- No flags from the reputation services TrustSniffer consulted when the evidence was captured.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
This website is a login and registration gateway for an online shop that calls itself "CC Shop" and "Authorize CVV". Its pages advertise "CVV", "FULLZ" and "credit scores", which are stolen payment-card records, full identity packages and credit-profile data. The only content a visitor sees is a sign-in prompt and a registration link. Its apparent business model is the sale of illicit financial data through an account-gated storefront.
Scam/Impersonation Risk: The site's own offering is the risk. The homepage title promises "FULLZ, CREDIT SCORES", and the page text reads "Cvv Authorize Shop | Fullz High Credit Score". These are stolen card and identity records, so the site presents itself as a criminal marketplace. Buying such data is a crime in most countries. Shops of this type typically take payment and deliver nothing, or hand the buyer's own details to the operators. The site describes no delivery, refund or dispute process. No conflicting legal identities, brand impersonation or phishing-database listings were observed, and reputation checks returned no detections. None of that offsets the nature of the offering, which is why the assessment is critical risk. The domain name contains the word "authorize", which is also the name of a well-known payment-gateway brand. The site is not that brand and presents itself only as a card-data shop. Its page structure also matches sibling domains with near-identical names that have already been assessed as critical, which fits a reused shop template. The sandbox recorded heavy page instability: many scripting errors and thousands of page-structure changes after interaction. These are scored findings and count toward the score.
- Homepage: title and text advertise "CC Shop", "FULLZ" and "CREDIT SCORES", with no legitimate product described.
- Homepage and registration page: access is gated behind sign-in and registration, and the page text mentions "Jabber or Telegram" as an access route.
- Sandbox behaviour: 63 console errors and 4,198 page-structure changes after interaction across 3 runs. No data was sent to unrecognised hosts.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Page template: matches three near-identically named sibling domains already assessed as critical.
Written analysis generated 2026-11-15 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
14 findings contributed to this verdict, raised by page content, code shared with sites rated critical, several checks together, behaviour in a sandbox, hosting and network, and registration and ownership.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page presents a sign-in form, and the operator behind it could not be independently verified.Page content
rule:PAGE_TYPE_LOGIN_UNVERIFIED - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
02 Code shared with sites rated Critical
- The site runs the same code, or has code wired to the same hidden endpoint, as other sites TrustSniffer rated Critical.Code shared with sites rated Critical
rule:KIT_SHARED_WITH_CRITICAL_SITE
03 Several checks together
- No external threat source confirms a listing for this site, but its own page content reads as risky.Several checks together
rule:HYB_POSITIVE_EXTERNAL_NEGATIVE_PAGE
04 Behaviour in a sandbox
- The page replaced a large part of its own content during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH - The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH
05 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, three to six months before capture.Hosting and network
rule:DNS_YOUNG_6M
06 Registration and ownership
- The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page structure: 3 findings share one limit, because they describe one page structure. The limit applied, so together they counted for less than their sum.
- Page quality: 3 findings share one limit, because each is weak evidence on its own. The limit applied, so together they counted for less than their sum.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Authorizecvv in
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of authorize-cvv.in.
- The request stayed on authorize-cvv.in. It was not redirected to another domain. Clear
- Registered through DYNADOT LLC. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-07-22. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 9 other sites it has analysed. All 9 are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
- authorisecvv.com (Critical)
- authorize-cvv.com (Critical)
- authorizecvv.shop (Critical)
- authorlzecvv.cc (Critical)
- authorizecvvv.in (Critical)
- authorizedcvv.in (Critical)
- authorizevcc.in (Critical)
- authorizevcc.io (Critical)
- authorizecvv.com (Critical)
| Shared files (SHA-256) | custom.js.download adf64f59a8ffa1cfcb9a837bf595796b624eac1fc6870a91bda55060f565cb24 (10 sites) |
|---|---|
| main.js.download 16697db49ca2f8d437eba02a05eedf61df917ee4f57c8e9903ffde235a3db252 (9 sites) | |
| styles.min.css 50171cf89baf10628e96fd1fef7d835ed6e3c16e3829300fc66003dbc604d424 (9 sites) | |
| v4513226cdae34746b4dedf0b4dfa099e1781791509496 e1ac4849b9d4a498b68f8aca01e6ed99a11d94b35a2cec533b3916b8fb722fd6 (6 sites) |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | DYNADOT LLC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3035::6815:61f |
| Name servers | aitana.ns.cloudflare.com, zeus.ns.cloudflare.com |
| CDN / edge network | Cloudflare (from the hosting network; the edge lookup did not complete) |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-19 |
| Domain age | 114 days (registered 2026-07-22) |
| Domain expiry | 2027-07-22 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about authorize-cvv.in at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.