Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
authorizedcvv.in shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the site asks visitors to sign in while its operator could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A login page for a site branded as a CVV shop. Other pages advertise 'Fullz High Credit Score' and require registration with Jabber or Telegram. The site appears to sell stolen payment card data and identity packages. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-13 and re-scored on 2026-11-15. The certificate, the registration age and the page content describe the site as it was on 2026-11-13.
- The real-world operator identity was not independently verified.
- These checks returned no result: CDN / edge network lookup, web archive lookup.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 2/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports | Clear |
| Domain age | 4 months oldRegistered 2026-07-22 | Risk |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETNetwork registered in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-07-22).
- No flags from the reputation services TrustSniffer consulted when the evidence was captured.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
AuthorizeCVV.IN is a members-only storefront that presents itself as the "BEST CVV Shop" and advertises "Fullz High Credit Score" packages. Visitors reach a sign-in and registration gateway, and registration asks for a Jabber or Telegram contact. The pages read describe an apparent marketplace that sells stolen payment-card data and bundled identity records to registered buyers. No legitimate product, seller or business is presented on those pages. Classification confidence is moderate (0.55), and the assessment rests on the site's own wording.
Scam/Impersonation Risk
The site presents critical risk, driven by what its own pages offer rather than by any third-party listing. Those pages advertise card verification values and "fullz" identity packages, which are stolen payment-card and personal-identity data. Buying such goods is unlawful in most jurisdictions. Shops of this kind also commonly take payment and deliver nothing, so a buyer faces legal exposure and a high chance of financial loss. The page reader found no named product catalogue, no verifiable seller and no company behind the offer. The only contact-related field requests a Jabber or Telegram identifier for registration, so no accountable operator could be identified from the pages read. TrustSniffer could not verify the identity of the site's operator. The signals found are an organisation name ("AuthorizeCVV IN"), a contact form and on-site identity text. These are consistent with a trade name, but they do not independently connect the site to a real-world brand or person.
Several signals count against the site, and each is described below with its source and how much weight it carries:
No third-party listing, brand impersonation, phishing finding or conflicting legal-entity names were observed. No external reputation source had flagged the domain when it was captured. That absence offers no assurance, given the nature of the offer and the very recent registration.
- Related domains: five of ten related domains that share the same page kit are themselves rated as critical risk in TrustSniffer's own analysis. This comes from infrastructure and page-kit similarity, so it is an inference about a possible replicated template, not direct evidence about this domain. It is discounted accordingly.
- Browser console errors and page-structure changes: the sandbox recorded a very high count of both after interaction. These are scored findings from automated behavioural runs. They are technical indicators rather than proof of intent, so they are weighed as supporting concern only.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Recent registration: the domain is very new. This is a registration-record fact, and on its own it is a weak indicator.
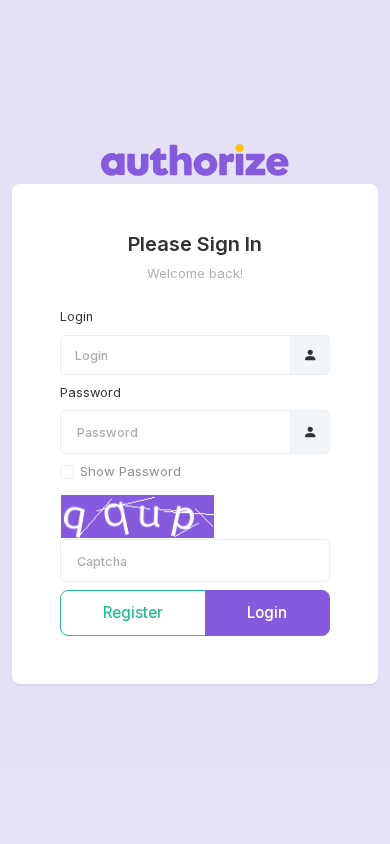
- Homepage: titled "AuthorizeCVV.IN | BEST CVV Shop | Authorize CVV", with sign-in and registration forms as its only visible content.
- Registration page: titled "Cvv Authorize Shop | Fullz High Credit Score" and asks for "Jabber or Telegram" as the contact channel. The page title differs from the homepage branding, which may simply be two names for the same shop.
- Registration record: the domain was created on 2026-07-22 and was 114 days old at capture, registered through Dynadot LLC with an expiry of 2027-07-22.
- Behavioural sandbox: 65 console errors and 4,198 page-structure mutations were recorded across three successful runs.
Regulatory Verification Notes
The pages read contain no regulatory or corporate disclosure of the kind a financial-data or payments business would be expected to make. On the pages read, no legal entity, registration or licence number, or regulator is named, and no postal address or company contact channel appears. The only disclosure found is a line on the registration page stating that creating an account means agreeing to "Terms & Conditions and Privacy Policy". That line is a generic statement and does not identify who operates the service. These gaps are consistent with the nature of the offer, since a business selling stolen card data would not be expected to hold a legitimate licence. The on-page disclosure position remains unclear. No third-party broker or regulatory-register match exists for the site, so there is no outside signal to weigh in either direction. The site's own identity claims are limited to its trade names. They have not been independently linked to any real person or organisation.
- Registration page: the Terms and Privacy line is the sole disclosure found, and it names no operator.
- Homepage and registration page: no legal entity, licence, regulator or address on the pages read.
- Transport encryption: the TLS certificate is a domain-validated one issued by WE1, valid to 2026-12-19. That validation level confirms control of the domain only and says nothing about who operates the business.
What to Verify Next
No step is needed to establish whether the site is a legitimate merchant, because its own pages describe an illicit card-data marketplace. Any person who has already registered, supplied contact details or paid should treat those details as compromised. Such a person should notify the relevant card issuer or bank, ask for card replacement and monitoring, and report the site to the national cybercrime or consumer-fraud authority. An organisation that finds employees or customers referencing this site should confirm the official support channels for any affected payment cards and alert its fraud team. Because the related domains share a page kit, blocking them at the network level may also be worthwhile. That judgement rests on similarity rather than confirmed common control.
- Registration page: the Jabber or Telegram requirement means any details given to the shop go to an unidentified party.
- Registration record: a domain created 114 days before capture, held through Dynadot LLC, gives a registrar abuse channel as a route for reporting.
- Homepage: the page is a credential gateway for an apparent card-data marketplace, so any identifiers entered there should be assumed exposed.
Summary Verdict
The available evidence supports a critical-risk assessment. The site's own pages offer what appear to be stolen payment-card and identity data through a members-only storefront with no identifiable operator, and nothing legitimate was found that counterbalances that purpose. The site should not be treated as a trustworthy service for any use beyond observation. The technical hygiene that is present, a valid certificate and no external reputation flag at capture, does not alter this conclusion.
Infrastructure Integrity
The site was served from AS13335, a network operated by Cloudflare, Inc., and the edge addresses observed, 104.21.78.172 and 172.67.136.32, belong to that provider. The origin server was not observed, so no hosting location or operator can be inferred. Use of this network is neutral: it neither mitigates the risk nor adds to it, and it gives no indication of who runs the site. The abuse record for the host address showed no reports, and this has no bearing on what the site's own pages offer.
Closing Assessment
The site should not be registered with, paid, or given any personal or financial details. Any interaction should be limited to passive observation by security or fraud teams, and anyone who has already engaged with it should follow the remediation steps above promptly.
Written analysis generated 2026-11-15 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
14 findings contributed to this verdict, raised by page content, code shared with sites rated critical, several checks together, behaviour in a sandbox, hosting and network, and registration and ownership.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page presents a sign-in form, and the operator behind it could not be independently verified.Page content
rule:PAGE_TYPE_LOGIN_UNVERIFIED - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
02 Code shared with sites rated Critical
- The site runs the same code, or has code wired to the same hidden endpoint, as other sites TrustSniffer rated Critical.Code shared with sites rated Critical
rule:KIT_SHARED_WITH_CRITICAL_SITE
03 Several checks together
- No external threat source confirms a listing for this site, but its own page content reads as risky.Several checks together
rule:HYB_POSITIVE_EXTERNAL_NEGATIVE_PAGE
04 Behaviour in a sandbox
- The page replaced a large part of its own content during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH - The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH
05 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, three to six months before capture.Hosting and network
rule:DNS_YOUNG_6M
06 Registration and ownership
- The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page structure: 3 findings share one limit, because they describe one page structure. The limit applied, so together they counted for less than their sum.
- Page quality: 3 findings share one limit, because each is weak evidence on its own. The limit applied, so together they counted for less than their sum.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:AuthorizeCVV IN
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of authorizedcvv.in.
- The request stayed on authorizedcvv.in. It was not redirected to another domain. Clear
- Registered through DYNADOT LLC. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-07-22. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 9 other sites it has analysed. All 9 are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
- authorisecvv.com (Critical)
- authorize-cvv.com (Critical)
- authorizecvv.shop (Critical)
- authorlzecvv.cc (Critical)
- authorize-cvv.in (Critical)
- authorizecvvv.in (Critical)
- authorizevcc.in (Critical)
- authorizevcc.io (Critical)
- authorizecvv.com (Critical)
| Shared files (SHA-256) | custom.js.download adf64f59a8ffa1cfcb9a837bf595796b624eac1fc6870a91bda55060f565cb24 (10 sites) |
|---|---|
| main.js.download 16697db49ca2f8d437eba02a05eedf61df917ee4f57c8e9903ffde235a3db252 (9 sites) | |
| styles.min.css 50171cf89baf10628e96fd1fef7d835ed6e3c16e3829300fc66003dbc604d424 (9 sites) | |
| v4513226cdae34746b4dedf0b4dfa099e1781791509496 e1ac4849b9d4a498b68f8aca01e6ed99a11d94b35a2cec533b3916b8fb722fd6 (6 sites) |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | DYNADOT LLC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3034::ac43:8820 |
| Name servers | aitana.ns.cloudflare.com, zeus.ns.cloudflare.com |
| CDN / edge network | Cloudflare (from the hosting network; the edge lookup did not complete) |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-19 |
| Domain age | 114 days (registered 2026-07-22) |
| Domain expiry | 2027-07-22 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about authorizedcvv.in at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.