Verdict
The site's own pages showed several warning signs that deceptive sites commonly use, and together with the other checks they put it in the critical-risk band. Do not pay, sign in, or share personal details with this site.
cvv2.su shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the site asks visitors to sign in while its operator could not be verified and the registration lookup did not return the domain's registrant and country. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A password-protected storefront titled 'Automatic Cvv Shop' that advertises '100% COMPATIBLE' card data. It shows no legal identity, contact details, pricing, or policies, and it is consistent with a stolen payment card trading site. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (70%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | None malicious; 2 marked it suspiciousVirusTotal | Watch |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports | Clear |
| Domain age | 12.0 years oldRegistered 2014-11-25 | Clear |
| Web archive | Archived since 2009111 snapshots; the history predates the current registration (2014-11-25); an earlier owner may have held the name | Noted |
| Certificate | Encrypted connectionIssued by YR2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: more than 10 years at capture (registered 2014-11-25).
- Public web-archive history exists since 2009.
- No security engine marked this domain as malicious; some marked it suspicious, which TrustSniffer does not count as a listing.
Full analysis
Overview
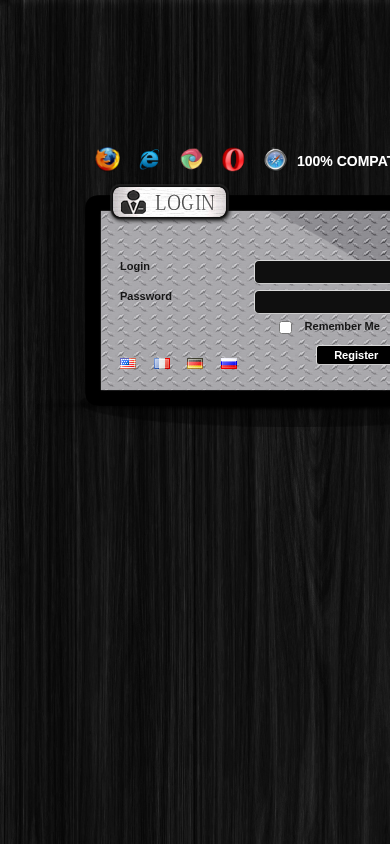
The website cvv2.su presents itself as an "Automatic Cvv Shop", a single-screen storefront whose only visible content is a "100% COMPATIBLE" banner above a member access panel with login, password and remember-me fields. It shows no catalogue, pricing, operator name or policy text. Its apparent purpose is to sell payment card verification data to members, and the page analysis found it consistent with a payment card data trading site.
Scam/Impersonation Risk
The assessment is critical risk, driven by what the site is rather than by any impersonation. No brand impersonation, conflicting legal identities, phishing indicator or third-party listing was observed. The risk comes from the storefront's own content. A shop for card verification data behind a members-only entry panel is a high-stakes offer, and the pages read give no pricing, delivery terms, refund terms or identifiable seller. The "100% COMPATIBLE" claim is a bare superlative with no supporting evidence, so the site's value flow cannot be verified. Behaviour at page load adds to the picture. Three requests carried data to destinations TrustSniffer does not recognise, and the page produced a high volume of console errors. Both are scored findings. Two engines rated the domain suspicious but none rated it malicious. A suspicious verdict is not a detection, and the score rests on the scored findings rather than on this alert.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Homepage and index page: the visible text is only the storefront title, the "100% COMPATIBLE" claim and the access panel. One form with sensitive-data characteristics was present, and no pricing or product detail appeared.
- Page loading: 3 requests sent data to destinations TrustSniffer does not recognise, and 18 console errors were recorded. Both are scored findings.
- VirusTotal: 0 engines malicious and 2 suspicious, so no engine detected the site. Google Safe Browsing did not list the site.
- Web archive: 111 snapshots from 2009-02-26 (first) to 2026-01-15 (last), a span of 6,167 days. The longest gap between captures was 893 days.
Regulatory Verification Notes
On the pages read, which were the homepage and the index page, a business of this type would be expected to disclose a legal entity, a registration or licence, a regulator and terms or privacy documentation. None of these four was found on those pages. The only identity-related element is a contact form. The site's own name appears as the organisation label, and TrustSniffer could not independently connect it to a real-world person or company. No third-party broker or regulatory record matched the site, so no external reputational signal is available either way. The registration record also lacks registrant and country details, which is a scored finding. Taken together, these gaps leave the legal status of any operator unestablished, and for a card-data storefront that absence carries real weight.
- Homepage and index page: no legal entity, licence or registration number, regulator, or terms and privacy documentation on the pages read.
- Registration record: registered 2014-11-25 through the registrar RUCENTER-SU, about 12.0 years at capture, with expiry on 2026-11-25. The registrant and country fields were missing.
- Transport encryption: certificate issued by YR2 at domain-validation level only, which confirms control of the domain but not who runs it. It was valid until 2026-12-27.
- Hosting network: served from AS214677.
What to Verify Next
The decisive question is whether any legal entity stands behind the storefront. A search of the relevant national business and company registers, run independently of the site, would show whether the operator exists. Any contact channel should be confirmed through an independent route rather than through the on-site form. How the address reached the reader (an unsolicited message, a referral or a search result) is also worth establishing before any further engagement.
- Homepage: a contact form is the only contact route offered, and no postal address was shown.
- Homepage and index page: no pricing, delivery terms or refund terms appeared on the pages read, so nothing can be checked against the "100% COMPATIBLE" claim.
- Registration record: registrant details are absent, so registry results cannot be matched to a named party from this record.
Summary Verdict
The overall posture is critical risk. The site's character and the behaviour of its pages outweigh the long registration history and the valid encryption certificate. The evidence supports no inference that it is a lawful, accountable business.
Infrastructure Integrity
The site resolves to a single address on a network operated by DeluxHost, with no CDN detected. A CDN's absence is neutral. The host's abuse record was checked and showed no reports. The certificate was valid at capture, and a valid certificate says nothing about who operates the site or what it sells.
Closing Assessment
Engagement with this site is not supported by the evidence. No payment or personal data should be submitted through its form, and any message that directed a recipient to it should be treated as unverified until independent checks establish who operates it.
Written analysis generated 2026-11-12 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
13 findings contributed to this verdict, raised by page content, several checks together, behaviour in a sandbox, and registration and ownership.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page presents a sign-in form, and the operator behind it could not be independently verified.Page content
rule:PAGE_TYPE_LOGIN_UNVERIFIED - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
02 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK - The domain has a long history, but the page it served when captured was weak.Several checks together
rule:HYB_STRONG_ARCHIVE_WEAK_PAGE
03 Behaviour in a sandbox
- The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
04 Registration and ownership
- The registration lookup did not return the domain's registrant and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE - The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page quality: 3 findings share one limit, because each is weak evidence on its own. The limit applied, so together they counted for less than their sum.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Cvv2 Su
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of cvv2.su.
- The request stayed on cvv2.su. It was not redirected to another domain. Clear
- Registered through RUCENTER-SU. Noted
- DNS for this domain is served by alidns.com, across 2 name servers. Noted
- The domain is registered until 2026-11-25. Noted
- The earliest public archive of this name is from 2009-02-26, before the current registration on 2014-11-25; an earlier owner may have held it. Noted
- It is hosted on DeluxHost, a network registered in FR; the provider, Matteo Martelloni trading as DELUXHOST, lists its country as IT. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files and uses the same analytics or tracking ID as 2 other sites it has analysed. All 2 are rated Critical on their own evidence.
Shared code and shared identifiers show that these sites were built from the same toolkit or are linked by the same identifier. It does not by itself show who operates them.
| Shared identifiers | Matomo analytics account: rescator.cm |
|---|
| Shared files (SHA-256) | clients.js 0b259dae0dc9b96ee4fda1c0f4d5dcbbfbda7416c5999ae0e1cfff49b198b7e2 (3 sites) |
|---|---|
| main.js 16ed628bee99e1906650937ddc524ea8cfce020add3b755d4ab1362b05e708d6 (3 sites) | |
| cufon-yui.js 186707c7ae0d45cba1490a5556f59fc371f6ab88cc16c452fef8b70072cb5e54 (3 sites) | |
| superfish.css 2ec1a689af26f7db8a124aa66bcb7a90d75ac4bbcabc815dcd870a409e9cbaae (3 sites) | |
| superfish.js 3e9fb74061133f9dc6c809fb777bdcdc8e02b6812ad5bf39aad5f6c69f1b96dd (3 sites) | |
| style.css 3f0a11b477ccbb0cbf7849e3faee6933b45d3b1fb4f40033d6b04a2067ee345c (3 sites) | |
| Titillium.js 4b65b5e72eb2f7e10aba6ce7fb2b5be6255cfa8de7598a9fc15b19a91b866aba (3 sites) | |
| loginbox.js bc90a3395b0542522a274b14ac44da670efeaae1401414f58930c49b3247b1d7 (3 sites) | |
| app.css 2e3488e37b02873ccea0d82ce57a6f4e188b116006c50d8526ea70df63b6690d | |
| main.css 45fe2ea12860c988c5a54c3b8a6b474cbe0d6cdbaa2d275f596330fcde9e6894 |
Showing 10 of the shared files, the most widely shared first.
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | RUCENTER-SU |
|---|---|
| Hosting | DeluxHost - Matteo Martelloni trading as DELUXHOST (the provider lists its country as IT) |
| Network registered in | FR |
| Server IP | 141.11.167.209 |
| Name servers | ns7.alidns.com, ns8.alidns.com |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR2 |
| SSL expiry | 2026-12-27 |
| Domain age | 11.97 years (registered 2014-11-25) |
| Domain expiry | 2026-11-25 |
| Archive first seen | 2009-02-26 (17.7 years before capture) |
| Archive snapshots | 111 |
| Reputation | VirusTotal: 0 malicious, 2 suspicious | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
The web archive has records of this name from 2009-02-26, before the current registration on 2014-11-25. That archive history predates the current registration, and an earlier owner may have held the name.
About this assessment
A trust score summarises the evidence TrustSniffer could collect about cvv2.su at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.