Verdict
Read-only browsing is the most the evidence supports: avoid signing in until a new check shows the listing has been cleared. An established site listed this way may have been compromised, in which case its owner is a victim.
cvv4you.su was listed as malicious by VirusTotal security engines when the evidence was captured on 2026-11-12.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the site asks visitors to sign in while its operator could not be verified and a form asks for sensitive details and sends them to a destination that could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A site that advertises the sale of stolen credit card data (CVV dumps, fullz, dumps with PIN) behind a forum-style login and registration form, with no verifiable operator identity. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- 9 VirusTotal engines (Fortinet, Kaspersky, Sophos among the engines that flagged it) marked this site as malicious when the evidence was captured on 2026-11-12, which meets TrustSniffer's bar for a confirmed listing. On its own it would limit the score to at most 24; the score is lower because of the other findings below. The domain had been registered for 12 years; an established site listed this way may have been compromised, in which case its owner is a victim rather than the source.
- The real-world operator identity was not independently verified.
- These checks returned no result: domain registration record (WHOIS), name servers (DNS).
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (70%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe confirmed external listing ceiling (at most 24) also applies, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 9 marked it malicious, 2 suspiciousVirusTotal; Fortinet, Kaspersky, Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 1 report; shared hosting inflates reports | Clear |
| First seen | 13.0 years before captureWeb archive; no registration record was returned | Clear |
| Web archive | Archived since 201344 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YR2 | Noted |
The page as captured
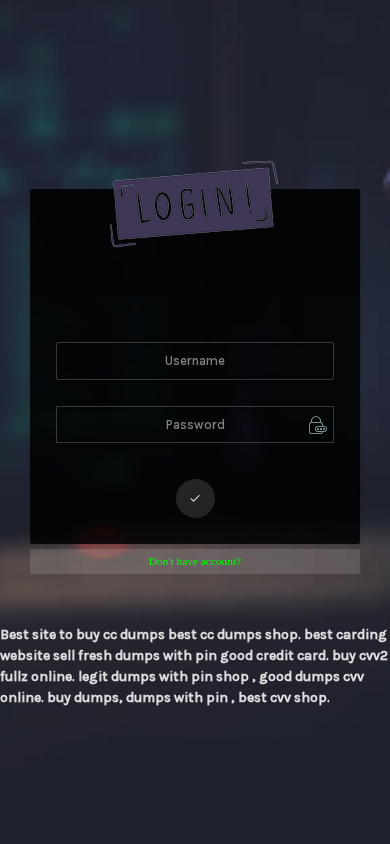
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: more than 10 years before capture (web archive; no registration record was returned).
- Public web-archive history exists since 2013.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
9 VirusTotal engines, including Fortinet, Kaspersky, Sophos, marked this site as malicious; this meets TrustSniffer's bar for a confirmed listing.
Overview
A forum-styled login and registration gateway fronting an online shop that advertises stolen payment card data. The homepage promotes "CVV dumps", "fullz" and "dumps with PIN" to buyers. It shows no company, pricing, delivery terms or support policy. Its apparent purpose is the sale of compromised card and identity data, and the sign-up and login forms appear to be the entry point to that marketplace.
Scam/Impersonation Risk
This assessment is at critical risk. The site's own homepage offers illicit goods. Its text is a series of sales pitches, including "Best site to buy cc dumps best cc dumps shop" and "buy cvv2 fullz online" (the same phrases are repeated in the page title). The page nonetheless presents itself as a "Forum Project User Login Page". The forum framing and the card-data content do not match, and the framing appears to serve as a front for the shop. Offering stolen card data is unlawful in most jurisdictions, and buying it is a crime. Marketplaces of this kind commonly take payment or registration details and deliver nothing, or expose buyers to further fraud. The site's own pages give no price list, delivery terms or refund policy, so a buyer would have no recourse. Security tooling also flagged the site. Nine engines rated it malicious, including three leading vendors, and two more rated it suspicious. This meets TrustSniffer's bar for a confirmed listing, although it comes from a single source. The score is low because of the scored findings below, not because of that alert alone. The scored findings are the illicit marketplace content, a password form, an unverified operator, missing page metadata, and a high volume of browser console errors. No brand impersonation or conflicting legal identities were observed. The identity problem is the absence of any verifiable operator, not a clash between names.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Homepage: the page text consists only of offers to sell card dumps, CVV2 data and fullz. The forum login title does not match that content.
- Homepage and registration page: two forms were observed, a login form and a registration form. TrustSniffer recorded a password form and a sensitive-data form, and the sandbox recorded 24 console errors.
- VirusTotal engine results at capture on 2026-11-12: 9 engines malicious and 2 suspicious, including Fortinet, Kaspersky and Sophos.
- Web archive: first seen on 2013-12-01 (4,729 days before capture), with 44 snapshots through 2026-11-04 (a span of 4,721 days). The archived samples contained no page content, so what the site sold in earlier years could not be established.
Regulatory Verification Notes
On the pages read (the homepage and the registration page), none of the disclosures expected of a financial-services business appeared. These are a legal entity, a registration or licence, a regulator, and terms or privacy information. A contact form is the only channel offered. The site also gives no price list, delivery terms or refund policy on the pages read. Given the illicit nature of the goods offered, a licence would not be expected to exist. These gaps therefore reinforce the critical-risk finding rather than stand alone as transparency notes. The site's claim to be a "legit" shop is an unsupported superlative, not evidence of authorisation. No third-party broker or regulator listing was matched, and the operator's real-world identity remains unverified.
- Homepage and registration page: no legal entity, licence or registration number, regulator, terms or privacy page appeared on the pages read.
- Network: the site resolved to a single address. The abuse record for that address was checked; its one report belongs to the shared address of the provider Chunkserve Mateusz Peplinski and was discounted.
- Transport encryption: a domain-validated TLS certificate issued by YR2 and valid until 2026-12-25. Domain validation confirms control of the domain only, not the operator's identity.
What to Verify Next
Verification here means protecting oneself, not testing the site's claims. Security and fraud teams should check proxy and DNS logs for any contact with this domain from internal systems. They should also review fraud-monitoring channels with card issuers for signs that their own cardholder data is being traded. Any exposure should be reported to the affected issuer or card scheme and to the national cybercrime reporting authority. The site should be added to organisational block lists.
- Registration page: a sign-up form that requests account details. Nothing on it indicates a legitimate service to confirm.
- Homepage: the only contact route is a form, so no independent channel exists through which the operator could be reached.
Summary Verdict
The site is rated critical risk. Its pages advertise the sale of stolen payment card data. It runs sign-up and login forms behind an unverifiable operator, and security tooling independently flagged it. The evidence points to an illicit marketplace, not a legitimate business with disclosure gaps.
Infrastructure Integrity
The site resolved to a single address. No content delivery network was observed, which is neutral. One abuse report existed for that address, but it belongs to the shared address of the provider Chunkserve Mateusz Peplinski and was discounted. The infrastructure neither supports nor offsets the content findings.
Closing Assessment
The site should not be visited for any purpose beyond analysis. No account should be registered, no credentials entered and no payment or card data sent. Organisations should block the domain and report any exposure.
Written analysis generated 2026-11-12 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
13 findings contributed to this verdict, raised by external reputation, page content, several checks together, behaviour in a sandbox, and registration and ownership.
01 External reputation
- 9 VirusTotal engines, including a leading vendor (Fortinet, Kaspersky, Sophos), marked this domain as malicious when the evidence was captured, which TrustSniffer counts as a confirmed external listing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- A form on the page submits to a destination TrustSniffer could not verify.Page content
rule:PAGE_FORM_UNTRUSTED_DEST - The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page presents a sign-in form, and the operator behind it could not be independently verified.Page content
rule:PAGE_TYPE_LOGIN_UNVERIFIED - The page asks visitors for sensitive information.Page content
rule:PAGE_FORM_SENSITIVE - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 Behaviour in a sandbox
- The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH - The page showed a password field during the sandbox session, and it could not be matched to a recognised brand's sign-in page.Behaviour in a sandbox
rule:BEHAV_PASSWORD_FORM_PRESENT
05 Registration and ownership
- The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Certificate and search-engine setup: 3 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 1 report on hosting IP 143.20.64.74 (wczapkowicz-as), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Cvv4you su
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of cvv4you.su.
- The request stayed on cvv4you.su. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2013-12-01. Clear
- It is hosted on wczapkowicz-as, a network registered in US; the provider, Wojciech Czapkowicz, lists its country as PL. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files and uses the same analytics or tracking ID as 2 other sites it has analysed. All 2 are rated Critical on their own evidence.
Shared code and shared identifiers show that these sites were built from the same toolkit or are linked by the same identifier. It does not by itself show who operates them.
| Shared identifiers | Matomo analytics account: rescator.cm |
|---|
| Shared files (SHA-256) | clients.js 0b259dae0dc9b96ee4fda1c0f4d5dcbbfbda7416c5999ae0e1cfff49b198b7e2 (3 sites) |
|---|---|
| main.js 16ed628bee99e1906650937ddc524ea8cfce020add3b755d4ab1362b05e708d6 (3 sites) | |
| cufon-yui.js 186707c7ae0d45cba1490a5556f59fc371f6ab88cc16c452fef8b70072cb5e54 (3 sites) | |
| superfish.css 2ec1a689af26f7db8a124aa66bcb7a90d75ac4bbcabc815dcd870a409e9cbaae (3 sites) | |
| superfish.js 3e9fb74061133f9dc6c809fb777bdcdc8e02b6812ad5bf39aad5f6c69f1b96dd (3 sites) | |
| style.css 3f0a11b477ccbb0cbf7849e3faee6933b45d3b1fb4f40033d6b04a2067ee345c (3 sites) | |
| Titillium.js 4b65b5e72eb2f7e10aba6ce7fb2b5be6255cfa8de7598a9fc15b19a91b866aba (3 sites) | |
| loginbox.js bc90a3395b0542522a274b14ac44da670efeaae1401414f58930c49b3247b1d7 (3 sites) | |
| app.css 2e3488e37b02873ccea0d82ce57a6f4e188b116006c50d8526ea70df63b6690d | |
| main.css 45fe2ea12860c988c5a54c3b8a6b474cbe0d6cdbaa2d275f596330fcde9e6894 |
Showing 10 of the shared files, the most widely shared first.
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | wczapkowicz-as - Wojciech Czapkowicz (the provider lists its country as PL) |
| Network registered in | US |
| Server IP | 143.20.64.74 |
| Name servers | Not available |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR2 |
| SSL expiry | 2026-12-25 |
| First seen (web archive) | 12.95 years before capture; no registration record was returned |
| Domain expiry | Not available |
| Archive first seen | 2013-12-01 (12.9 years before capture) |
| Archive snapshots | 44 |
| Reputation | VirusTotal: 9 malicious, 2 suspicious | AbuseIPDB: 0% confidence, 1 report | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about cvv4you.su at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.