Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
idgod.ph shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
| How the site describes itself | IDGod.ph is an online shop selling counterfeit state ID cards that it says scan and pass UV checks. Orders collect a photo, signature and personal details, and are paid in crypto, cash or mobile wallets before shipping. The site names no legal entity, registration or physical address, and its own terms restrict the cards to novelty use. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-11 and re-scored on 2026-11-14. The certificate, the registration age and the page content describe the site as it was on 2026-11-11.
- One external source flagged this site when the evidence was captured: 3 VirusTotal engines (Sophos among the engines that flagged it) marked it as malicious. No second source confirms it. The alert is from the evidence captured on 2026-11-11; it was not re-queried for this version and is treated as unconfirmed. On its own it would limit the score to at most 49; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
- These checks returned no result: domain registration record (WHOIS), name servers (DNS).
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe unconfirmed alert ceiling (at most 49) also applies, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 3 marked it malicious, 1 suspiciousVirusTotal; Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports | Clear |
| First seen | 12.0 years before captureWeb archive; no registration record was returned | Clear |
| Web archive | Archived since 2014573 snapshots | Clear |
| Certificate | Encrypted connectionIssued by Sectigo Public Server Authentication CA DV R36 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- First seen: more than 10 years before capture (web archive; no registration record was returned).
- Public web-archive history exists since 2014.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
3 VirusTotal engines, including Sophos, marked this site as malicious; VirusTotal is a single source, so this is one unconfirmed alert.
Overview
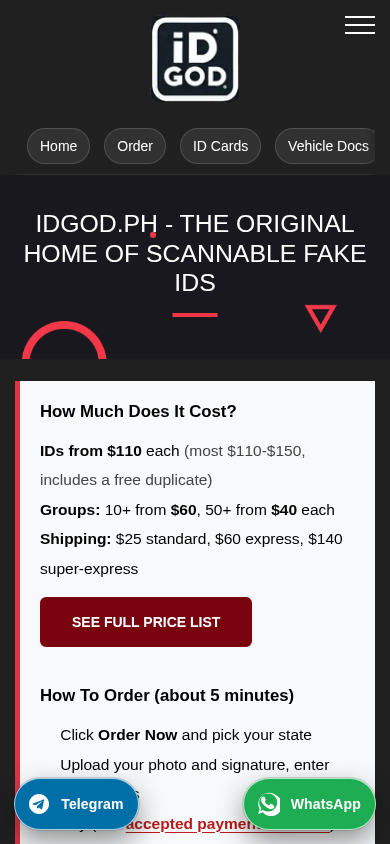
IDGod.ph is an online store that presents itself as the official home of the original "ID God" brand and sells counterfeit US state identification cards marketed as scannable and able to pass UV checks. A visitor picks a state, uploads a photo and signature, enters personal details, and pays before shipping by Bitcoin or other cryptocurrency, Google Pay or Apple Pay, or cash. Prices run from $40 to $150 per card depending on volume, with shipping of $25 to $140. The business model is the per-card sale of forged identity documents, shipped in what the site calls discreet packaging.
Scam/Impersonation Risk
The evidence supports a critical risk assessment. No brand impersonation and no conflicting legal identities were observed. The risk comes from the nature of the offer and from the adverse external signals. A single external alert is on record from VirusTotal, with three engines rating the domain malicious and one suspicious, Sophos among the malicious. This is one source and is not treated as a confirmed listing. The critical rating reflects the sum of the scored findings: the sale of counterfeit identity documents, prepayment through hard-to-reverse channels, an unnamed operator, and page-behaviour findings. The site sells fake IDs openly, and the cards are unlawful to buy or use in many jurisdictions. Payment is taken before shipping, and no verifiable merchant or delivery record exists to support a dispute. The site collects a government-style photo, a signature and personal details, so a buyer also hands identity data to an operator who cannot be identified. The offer is marketed with claims that the site's own pages do not support. The homepage promises "Scans & Works 100% Guaranteed" and "Undetectable", backed only by customer-submitted videos. It cites press features in USA Today, The State and The Brown and White. Its terms describe the cards as novelty items not approved for anything unlawful or deceptive, while the FAQ promises they pass scanners and UV checks at bars and stores. A quoted testimonial on the site says college IDs from this seller make it hard to keep underage people out. The site's own pages also state group pricing two ways: "10+ from $60" on the homepage and $75 for 10 to 49 IDs in the price table.
- External alert (VirusTotal): three engines malicious and one suspicious as of capture on 11 November 2026, with Sophos among the malicious. This is a single source and is not a confirmed listing.
- Homepage and price list: IDs from $110 each, groups of 10 or more from $60 and 50 or more from $40, shipping at $25 standard, $60 express and $140 super-express, and payment in Bitcoin or other cryptocurrency, mobile wallets or cash before shipping.
- Homepage and FAQ: the "Scans & Works 100% Guaranteed" and "Undetectable" claims sit alongside terms that restrict the cards to novelty use.
- Homepage behaviour: 3,039 page-structure changes occurred after interaction, and no meta description or structured data was present. Both are counted among the scored findings.
Regulatory Verification Notes
The site presents itself as the official home of the original ID God. This is an on-site claim, and the evidence points to a likely but independently unconfirmed brand identity. On the pages read, which covered the homepage, terms, privacy policy, contact, about, FAQ and two product pages, no legal entity or physical address was named. Terms are present, with a reprint and refund clause and a re-shipment fee for undeliverable parcels. Those terms are governed by the laws of the People's Republic of China, although the site ships worldwide and targets US state documents. No licence, regulator or business registration appears on the pages read, and a seller of this kind could not hold a legitimate one for these goods. The "Real IDGod Verification" and "ScamAdviser Certified" badges are self-asserted, with no verifiable certificate behind them. The site's long-lived presence and valid encryption do not outweigh the findings above. The web archive first saw the domain on 17 November 2014, and the transport encryption was valid at capture. No third-party broker or regulatory-database match was found.
- Terms and conditions page: governed by the laws of the People's Republic of China, with no legal entity named and a reprint-or-refund clause that excludes errors in details the buyer supplied.
- Web archive: 573 snapshots from 17 November 2014 to 19 August 2026, a span of 4,293 days.
- Hosting: served from AS30860 (YURTEH-AS, Virtual Systems LLC), a network registered in UA.
- Transport encryption: a domain-validated certificate issued by Sectigo Public Server Authentication CA DV R36, valid until 28 March 2027 as seen at capture.
What to Verify Next
Nothing on the pages read supports submitting a photo, signature, personal details or payment. For anyone who has already done so, the first step is to treat the submitted identity data as exposed and to contact the payment provider or wallet operator about the transaction. A second step is to check the press features the site cites directly with the publishers, since links the site publishes are not independent evidence. A third is to ask the local consumer-protection or law-enforcement authority about the legal exposure of buying or carrying counterfeit identification. A final step is to look for any registered business entity in the jurisdiction named in the terms. Any channel the site offers should be treated as unconfirmed unless confirmed through an independent route.
- Homepage: the press-feature claims and the "Real IDGod Verification" and "ScamAdviser Certified" badges are self-asserted and carry no independent proof.
- FAQ page: a re-shipment fee of $50 applies to single orders and up to $200 to group orders when an address is wrong, and the delivery guarantee excludes those cases.
- About page: describes stealth shipping in jewelry or phone boxes, with no carrier or tracking record presented.
Summary Verdict
TrustSniffer assesses the site as a critical risk. The business sells counterfeit identity documents, the claims it makes are unsupported, and its operator cannot be identified. The site's longevity and encryption do not change that conclusion.
Infrastructure Integrity
The site resolves to a single origin address. No CDN or edge layer was detected, which is a neutral observation. The host's abuse record was checked and showed no reports, and the page made no requests that sent data to other hosts. Neither point offsets the critical findings above.
Closing Assessment
The site should not be used for ordering, uploading identity material or paying. No part of the offer warrants engagement.
Written analysis generated 2026-11-14 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
11 findings contributed to this verdict, raised by external reputation, page content, several checks together, behaviour in a sandbox, and registration and ownership.
01 External reputation
- 3 VirusTotal engines marked this domain as malicious when the evidence was captured.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 Behaviour in a sandbox
- The page replaced a large part of its own content during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION - The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE
05 Registration and ownership
- The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page structure: 3 findings share one limit, because they describe one page structure. The limit applied, so together they counted for less than their sum.
- Certificate and search-engine setup: 3 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:IDGod ID God
- contact:email
- contact:form
- on_site_identity
- Email address shown on the page: [email protected] (not checked)
What TrustSniffer observed
First-party facts recorded during the assessment of idgod.ph.
- The request stayed on idgod.ph. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2014-11-17. Clear
- It is hosted on YURTEH-AS, a network registered in UA. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site lists the same contact as 2 other sites it has analysed. All 2 are rated Critical on their own evidence.
A shared identifier links these sites. It does not by itself show who operates them.
| Shared identifiers | WhatsApp contact: withheld |
|---|
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | YURTEH-AS - Virtual Systems LLC |
| Network registered in | UA |
| Server IP | 91.208.115.38 |
| Name servers | Not available |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | Sectigo Public Server Authentication CA DV R36 |
| SSL expiry | 2027-03-28 |
| First seen (web archive) | 11.98 years before capture; no registration record was returned |
| Domain expiry | Not available |
| Archive first seen | 2014-11-17 (12.0 years before capture) |
| Archive snapshots | 573 |
| Reputation | VirusTotal: 3 malicious, 1 suspicious | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about idgod.ph at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.