Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
testtttingmeeeehq.pages.dev shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: as a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site) and a form asks for sensitive details and sends them to a destination that could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A Webflow landing page for 'Decentralised Webee3 Protocol' promoting Web3, smart-contract and tokenization services. It includes Connect Wallet and Migrate Token calls to action, plus an embedded MetaMask-style spending-cap approval flow that requests permission to spend tokens from a third-party spender, with placeholder contact details and no verifiable legal identity. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- External threat sources confirmed a listing for this site when the evidence was captured (VirusTotal, a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-25)). On its own it would limit the score to at most 24; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe independent sources ceiling (at most 24) and the threat-listing ceiling (at most 5) also apply, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 4 marked it malicious, 1 suspiciousVirusTotal; Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 5 months before captureWeb archive; a site on pages.dev has no registration of its own | Risk |
| Web archive | Archived since 20262 snapshots; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: less than 1 year before capture (web archive; a site on pages.dev has no registration of its own).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
4 VirusTotal engines, including Sophos, marked this site as malicious; independent sources confirm a listing for this site.
Overview
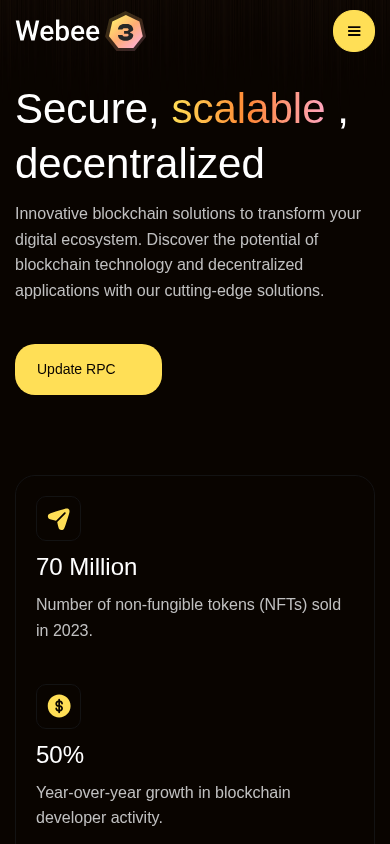
The site is a single-page landing site for "Decentralised Webee3 Protocol". It presents itself as a Web3 services provider offering blockchain integration, smart contracts, tokenization and token migration. Its homepage is built on Webflow and published from a free subdomain on Cloudflare's Pages hosting platform. The domain name contains the platform's name, but the site is not that platform. A visitor sees "Connect Wallet" and "Migrate Token" calls to action, a "View pricing" link with no prices, and an embedded wallet-style approval prompt. Its apparent purpose is to steer visitors into linking a crypto wallet and granting token-spending permission, rather than to sell a documented service.
Scam/Impersonation Risk
Confirmed contradictions are present and the risk is critical. Independent sources currently align on this address: a leading security vendor and other scanning engines flag it as malicious, and a threat-intelligence listing identifies it as a source of phishing, last seen on 25 October 2026. The homepage's own behaviour matches that picture. It embeds an imitation of a MetaMask "Spending cap request" dialog stating "This site wants permission to spend your tokens", with a third-party spender field and no terms, risk warning or legal entity covering the flow. A token approval of this kind lets another party move a visitor's assets, so it is the most dangerous interaction the page offers. The page also sends a large volume of requests to other hosts. All of them went to recognised services, but this is still a scored finding. It supplements the stronger signals above and is not the cause of the verdict.
The page's own content undermines its claims. The brand is Webee3, but the address line names "Estica Cop." and the footer credits Webestica. The page gives no company registration to connect these names. The headline statistics (70 million NFTs sold in 2023, 50% developer growth, 20,000+ projects) cite no source. The testimonials name companies such as CryptoInnovate and DecentralEdge with no way to verify them. The page cites Ethereum, Binance Smart Chain, Polygon and Filecoin to suggest breadth, but it names no contract or team behind any token it asks visitors to migrate.
- VirusTotal: four engines rated the address malicious, including Sophos, and one rated it suspicious. A separate threat-intelligence listing classes it as phishing, last seen 25 October 2026.
- Homepage: it embeds a spending-cap approval prompt that imitates a MetaMask dialog, plus a wallet-connect control and a newsletter form. Two forms were seen in total, and one of them posts to a destination the analysis could not trust.
- Registration record and web archive: the address was first seen 160 days before capture. The archive holds two snapshots, from 2026-06-03 to 2026-06-16, a span of 13 days.
- Homepage footer and address line: they name Estica Cop. and Webestica against the Webee3 brand.
Regulatory Verification Notes
No licence, regulator, registration number or regulated status is claimed or found on the pages read, and no third-party broker record matched. Of the disclosures a token project is expected to make, the homepage links a Privacy Policy. On the pages read, it lists no smart-contract address and no named team. The only identity details on the homepage are a Chicago headquarters line attributed to "Estica Cop." and contact details that use a placeholder email domain and a 555 test phone number. These are the site's own claims, and nothing independent connects them to a real operator. Because the page invites token approvals, the absence of a contract address, team and governing terms matters more than it would for an informational site.
- Homepage: a Privacy Policy link is present. No contract address or team section appeared on the pages read.
- Homepage: the "Chicago HQ Estica Cop." line and the placeholder contact details do not connect to any verifiable entity.
- Hosting: the site is served from AS13335 (Cloudflare, Inc., US), and the host's abuse record showed no reports.
- Transport encryption: the DV certificate was issued by WE1 and was valid to 2027-01-21. This shows only an encrypted connection, not who operates the site.
What to Verify Next
Anyone who has already connected a wallet or approved a spending cap on this site should review the wallet's token-approval list and revoke any permission granted to an unfamiliar spender. Any claim about the "Webee3" token or a migration should be checked only through an official source that is independent of this site, such as a published contract address on a block explorer. The listed headquarters and the Estica and Webestica names can be checked against a company register before any further contact. Support or contact channels should be confirmed through an independent route and not taken from this page.
- Homepage: the "Migrate Token" call to action gives no contract address or terms to check against.
- Homepage: the approval prompt names a third-party spender but gives no identity for it.
- Homepage: the headquarters line and the footer credit name different entities.
Summary Verdict
The assessment is critical risk. Independent threat sources align with the page's own wallet-approval mechanics and unsupported identity claims, and nothing in the evidence offsets them. Technical hygiene such as a valid certificate establishes only that the connection is encrypted, not that the operator is legitimate. The identity the site presents appears on-site only and remains unconfirmed.
Infrastructure Integrity
The site is served through Cloudflare, and all four observed addresses are edge addresses, so no origin server address was observed. TrustSniffer treats this as neutral. It neither mitigates nor adds to the risk, and it says nothing about the operator or content behind the edge. The same shared platform hosts many unrelated tenants, so the hosting gives no support to the site's identity claims.
Closing Assessment
This site should not be used for any wallet connection, token migration, spending approval or other financial interaction. Any use should be limited to viewing the page, and no permission should be granted from it under any circumstances.
Written analysis generated 2026-11-10 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
18 findings contributed to this verdict, raised by external reputation, page content, several checks together, history in the web archive, hosting and network, registration and ownership and behaviour in a sandbox.
01 External reputation
- 4 VirusTotal engines marked this domain as malicious when the evidence was captured.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- A form on the page submits to a destination TrustSniffer could not verify.Page content
rule:PAGE_FORM_UNTRUSTED_DEST - The page code contained a hidden form, a pattern common to phishing pages.Page content
rule:PAGE_PHISHING_HIDDEN_FORMS - The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The page runs on a free hosting-platform address instead of a domain of its own, a setup common to short-lived phishing and claim pages.Page content
rule:PAGE_FREE_PLATFORM_ADDRESS - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page asks visitors for sensitive information.Page content
rule:PAGE_FORM_SENSITIVE - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
05 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, three to six months before capture.Hosting and network
rule:DNS_YOUNG_6M
06 Registration and ownership
- As a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site).Registration and ownership
rule:KF_WHOIS_INCOMPLETE - The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
07 Behaviour in a sandbox
- The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:Decentralised Webee3 Protocol
- contact:form
- on_site_identity
- Phone number shown on the page: +1 (555) 123-4567 (not checked)
- Email address shown on the page: [email protected] (not checked)
What TrustSniffer observed
First-party facts recorded during the assessment of testtttingmeeeehq.pages.dev.
- The request stayed on testtttingmeeeehq.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-06-03. Watch
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 12 other sites it has analysed. 10 of them are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
- evmhealth.pages.dev (Critical)
- layer3-pro.pages.dev (Critical)
- ooooioioioioioi-xyz-ss.pages.dev (Critical)
- redstone-com.pages.dev (Critical)
- sale-surgecardano-com.pages.dev (Critical)
- vote-8zf.pages.dev (Critical)
- vote-mantle.pages.dev (Critical)
- vote-trillions.pages.dev (Critical)
- standx-vote-upcoming-rewards-date-treasury-pool-rewards.pages.dev (Critical)
- vote-mefai.pages.dev (Critical)
- app-fuseon-finance.pages.dev
- bluwhale-169.pages.dev
| Shared files (SHA-256) | fpbundle.js 126a8b465ef8734b4d7a289781e0535cd283ccf24394e08c44f23ae300be3a5a (13 sites) |
|---|---|
| modals.js 6d0c2c8d032982e9a86a1bed14f709911058b6b693abb5d46335a0106c12c411 (13 sites) | |
| bundle.js 969be4f64afdeaca0568779c3b0f7291bc9a7185cc983a5104fbd90e4f901039 (13 sites) | |
| main.js ef6c818437d7e45baf8db39611a38ee242ada87a72694cbad2b17f8ba0564c29 (3 sites) | |
| main.js a835bce751f034f8e6500642f4fa8469c97214e1f4375a7bb5b415c0447f20e6 | |
| main.js c52b6118f3b9965cc4ed552dc21b0882fd7eeb1f8bfd709a93e42f18fc633539 |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:310c::ac42:2cd5 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-21 |
| First seen (web archive) | 160 days before capture; a site on pages.dev has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2026-06-03 (160 days before capture) |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 4 malicious, 1 suspicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about testtttingmeeeehq.pages.dev at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.