Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
vote-trillions.pages.dev shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| How the site describes itself | A minimal token promotion page for TRILLIONS with 'How to buy' and 'Why you should buy' sections and a repeated 'Rewards Update' banner. It promises voters an early allocation from the Treasury Pool Funds but gives no verifiable details about the treasury, the token contract, the team, or the rules for the allocation. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 1.1 years before captureWeb archive; a site on pages.dev has no registration of its own | Clear |
| Web archive | Archived since 20256 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: 1 to 3 years before capture (web archive; a site on pages.dev has no registration of its own).
- Public web-archive history exists since 2025.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
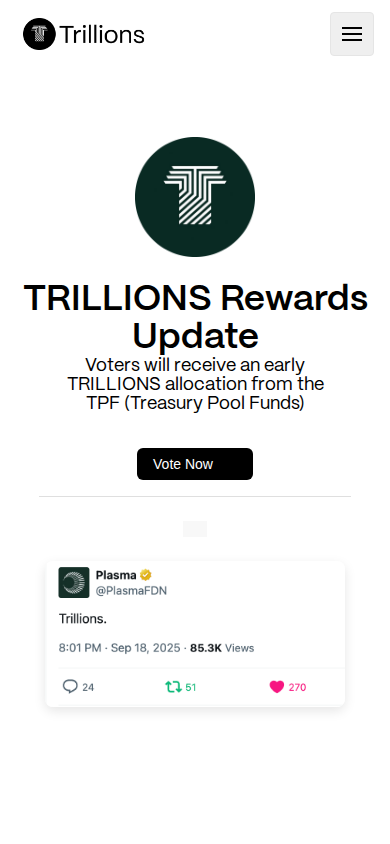
TRILLIONS is a single-page crypto token promotion site hosted on a free subdomain of a developer hosting platform. It shows only a navigation bar (Home, How to buy, Why you should buy, Chart) and a repeated "Rewards Update" banner. The banner says voters will receive an early TRILLIONS allocation from the "TPF (Treasury Pool Funds)", with a "Vote Now" button. Its apparent purpose is to push visitors to buy the TRILLIONS token and to take part in a vote tied to a reward. The page gives no token contract, team, documentation, or rules for the reward.
Scam/Impersonation Risk
Confirmed contradictions are present, and the site is blacklisted by several independent threat-intelligence sources. Several security engines flag the domain as malicious, and an external blacklist corroborates this. Behavioral testing also found strong cloaking. After interaction, both the visible content and the layout of the page changed completely from what was first rendered. A page can show different content to scanners than to real visitors in this way. The site also sits among a cluster of sibling subdomains on the same hosting platform that are flagged for similar abuse, a pattern typical of disposable kit-style crypto promotion pages. The page's own content matches this pattern. It promises an "early allocation from Treasury Pool Funds" to voters, but it never says who funds the pool, how large it is, or what a voter must do or pay to receive it. This is a value-flow claim with nothing behind it. Such "vote to earn" hooks are commonly used to lead visitors toward wallet connections or token purchases. No wallet-connection prompt, login form, or form submission was observed during testing, so the page's actual payment or drain mechanism, if any, was not seen. No conflicting legal identities or brand impersonation were established.
- Homepage: the banner promises an "early TRILLIONS allocation from the TPF (Treasury Pool Funds)" to voters, with no details of source, size, or conditions. The page text is only about 289 characters long.
- Behavioral testing of the homepage: strong cloaking, with the page fully replaced after interaction. One of three test runs failed.
- Hosting platform: 10 sibling subdomains on the same platform are flagged, including several crypto-themed ones.
- Provenance: the domain is about 1.07 years old, and 6 archive snapshots span 2025–2026 (2 years tracked, first capture October 2025). This is a short, thin history.
Regulatory Verification Notes
The site presents no legal entity, licence, registration number, jurisdiction, terms page, or physical address. The business is a token promotion with a treasury-allocation claim, and nothing on the site shows it is authorised for any financial or investment activity. The site's real-world operator remains unverified. No third-party broker or regulator record matches this site. The absence of regulatory information is a disclosure gap, but the confirmed threat detections above are what drive the cautionary assessment. The site's own pages offer no legal or contractual basis for any promised allocation.
- Homepage: no company name, licence, address, contact channel, risk disclosure, or token contract is shown.
- Hosting: served from AS13335 (Cloudflare, Inc., US) on a platform-provided subdomain, so there is no independently registered brand domain.
- Transport encryption: the TLS certificate was issued by WE1 (DV, domain validation only) and is valid to 2026-12-28. Encryption confirms the connection is private but says nothing about who operates the site.
What to Verify Next
Do not rely on anything on the page as proof of the project. Any claim that TRILLIONS exists as a legitimate token should be checked through an independent route, such as a reputable token-data aggregator or a block explorer. The contract address must come from a source outside this site, and its issuer, holder distribution, and liquidity should be reviewed. A prospective participant should also ask the project's claimed operators, through channels found independently of this page, to document what the "Treasury Pool Funds" are and who controls them. The official support channels should be confirmed the same way. Security teams can also check whether the flagged sibling subdomains share this page's markup or wording.
- Homepage: the "Vote Now" action gives no destination, contract, or terms, so any link or wallet prompt reached through it would have to be treated as unvetted.
- Homepage: the "How to buy" and "Why you should buy" sections contain no verifiable instructions or sources.
- Sibling subdomains: 10 related pages on the same hosting platform are flagged, with 5 named in the available sample.
Summary Verdict
The available evidence points to a high-risk, cautionary posture. Confirmed threat detections, deceptive page behavior, and an unsupported reward claim outweigh the site's technically sound connection and its short but continuous history. The site's operator remains unverified, and nothing found supports treating it as a legitimate project.
Infrastructure Integrity
The site is delivered through Cloudflare's CDN and WAF, and all observed addresses are CDN edge servers. The origin server was not observable. Edge-only visibility prevents independent confirmation of where the content is actually hosted and can mask rapid content swaps. The Cloudflare protection mitigates exposure to infrastructure-level abuse, but it neither vouches for the operator nor offsets the reputation findings.
Closing Assessment
The site should be treated as unsafe for any login, credential entry, wallet connection, or payment. Any interaction should be limited to passive viewing in an isolated environment. Anyone who has already acted on the page should disconnect and revoke any wallet permissions and monitor their accounts.
Written analysis generated 2026-11-06 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox and page content.
01 External reputation
- Three or more VirusTotal engines, or two including a leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_HIGH
02 Behaviour in a sandbox
- During the sandbox session the page showed markedly different content to different visitor profiles. This can have ordinary causes such as bot defence, and it can also hide content from checks.Behaviour in a sandbox
rule:BEHAV_CLOAKING_STRONG
03 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN - The page runs on a free pages.dev address instead of a domain of its own, a setup common to short-lived phishing and claim pages.Page content
rule:PAGE_BRAND_SUSPECTED
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of vote-trillions.pages.dev.
- The request stayed on vote-trillions.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2025-10-10. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 12 other sites it has analysed. 10 of them are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
- evmhealth.pages.dev (Critical)
- layer3-pro.pages.dev (Critical)
- ooooioioioioioi-xyz-ss.pages.dev (Critical)
- redstone-com.pages.dev (Critical)
- sale-surgecardano-com.pages.dev (Critical)
- testtttingmeeeehq.pages.dev (Critical)
- vote-8zf.pages.dev (Critical)
- vote-mantle.pages.dev (Critical)
- standx-vote-upcoming-rewards-date-treasury-pool-rewards.pages.dev (Critical)
- vote-mefai.pages.dev (Critical)
- app-fuseon-finance.pages.dev
- bluwhale-169.pages.dev
| Shared files (SHA-256) | fpbundle.js 126a8b465ef8734b4d7a289781e0535cd283ccf24394e08c44f23ae300be3a5a (13 sites) |
|---|---|
| modals.js 6d0c2c8d032982e9a86a1bed14f709911058b6b693abb5d46335a0106c12c411 (13 sites) | |
| bundle.js 969be4f64afdeaca0568779c3b0f7291bc9a7185cc983a5104fbd90e4f901039 (13 sites) | |
| main.js ef6c818437d7e45baf8db39611a38ee242ada87a72694cbad2b17f8ba0564c29 (3 sites) | |
| main.js a835bce751f034f8e6500642f4fa8469c97214e1f4375a7bb5b415c0447f20e6 | |
| main.js c52b6118f3b9965cc4ed552dc21b0882fd7eeb1f8bfd709a93e42f18fc633539 |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:310c::ac42:2c89 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-28 |
| First seen (web archive) | 1.07 years before capture; a site on pages.dev has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2025-10-10 (1.1 years before capture) |
| Archive snapshots | 6 |
| Reputation | VirusTotal: 4 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about vote-trillions.pages.dev at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.