Verdict
This assessment found strong scam indicators on the site itself. Do not pay or share personal details with this site.
clonecardnotes.com shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: The governance checks raised a concern: the page offers goods that are illegal to sell; the registration lookup did not return the domain's registrant. The findings below give the detail.
| How the site describes itself | The site sells clone cards, counterfeit banknotes and Flash BTC Software, promising untraceable ATM cashout and accepting cryptocurrency payment. It states no legal entity, licence, physical address or working contact channel, and the products are instruments of financial fraud. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-11-12 and re-scored on 2026-11-15. The certificate, the registration age and the page content describe the site as it was on 2026-11-12.
- One external source flagged this site when the evidence was captured: 4 VirusTotal engines (Fortinet among the engines that flagged it) marked it as malicious. No second source confirms it. The alert is from the evidence captured on 2026-11-12; it was not re-queried for this version and is treated as unconfirmed. On its own it would limit the score to at most 49; the score is lower because of the illegal-goods ceiling, shown under At a glance, and the other findings below.
- The real-world operator identity was not independently verified.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 10/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | Illegal-goods ceilingThe site's own pages offer illegal goods for sale (stolen card or bank data, counterfeit money, forged documents, illegal drugs, prescription drugs sold without a prescription, or darknet-market access), and that caps the score. The unconfirmed alert ceiling (at most 49) also applies, but the score is below it. | Risk |
|---|---|---|
| Malware engines | 4 marked it malicious, 3 suspiciousVirusTotal; Fortinet among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which the capture did not observe; a later check found it, shown below | Noted |
| Domain age | 2.4 years oldRegistered 2024-06-27 | Clear |
| Web archive | Archived since 2024117 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: 1 to 3 years at capture (registered 2024-06-27).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
4 VirusTotal engines, including Fortinet, marked this site as malicious; VirusTotal is a single source, so this is one unconfirmed alert.
Overview
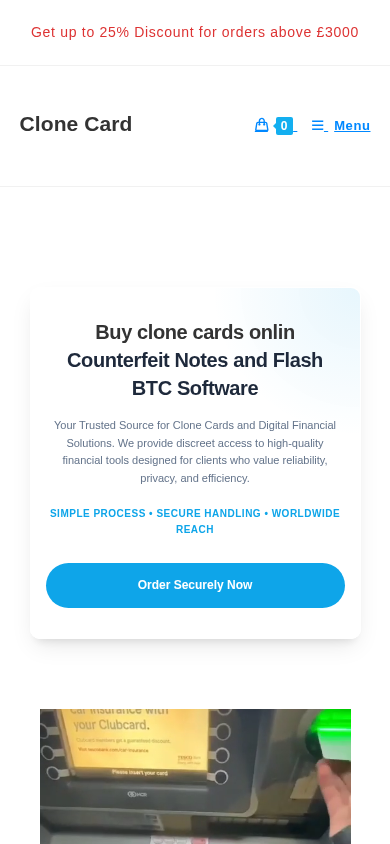
The website clonecardnotes.com is an online shop that presents itself as "Your Trusted Source for Clone Cards and Digital Financial Solutions". Its homepage and product pages list loaded clone cards, counterfeit banknotes in several currencies, and "Flash BTC Software", with checkout in cryptocurrency. The apparent business model is direct sale of instruments for financial fraud, priced at a stated range of £199.00 to £900.00 per item.
Scam/Impersonation Risk
This is a critical-risk site, and the central finding is what it sells. The site's own pages offer stolen-financial-data goods: the homepage title and product listings say "buy clone cards", and the pages promise cards that arrive "fully configured and ready for immediate spending or ATM cashout", with "Skip verification steps" as a selling point. They also sell counterfeit notes, including USD, AUD, EUR and CAD bundles. Buying such goods is a crime in most countries. Shops of this kind commonly take payment, usually in cryptocurrency that cannot be recovered, and deliver nothing, and the score reflects this. The "illicit goods offered for sale" ceiling is what holds the score down. No outside source has confirmed the illicit-goods finding. It rests on the site's own pages.
Separately, a single outside source, VirusTotal, raised an alert on the domain at capture. Four engines rated it malicious, including the leading vendor Fortinet, and three rated it suspicious. This is one source, not corroboration, and Google Safe Browsing had not listed the site. It does not set the score. No brand impersonation and no conflicting legal entities were found. The risk comes from the goods themselves, the payment mechanics and the absence of any accountable operator.
The site's pages contradict one another. The brand appears as "Clone Card", "Card Cloning", "The Clone Card Hub" and "Clone card and Counterfeit Notes Shop". The clone-card listing is titled "$2000 - $12000" while the displayed price range is £199.00 through £900.00. A headline "up to 25% discount for orders above £3000" sits beside products that start at £199.00. The About page describes the products as for "professional and educational purposes", which cannot be squared with listings sold for ATM cashout.
The site's own claims are unsupported marketing: "Pay securely using BTC, ETH, and top cryptocurrencies for encrypted, fast, and completely private transactions" and "100% Discreet & Tracked Worldwide Delivery". During sandbox browsing the page sent 21 requests carrying data to destinations TrustSniffer does not recognise. These are 12 background fetches and 9 POST submissions, and they count as scored findings.
- Homepage and product pages: the title and listings say "buy clone cards", with loaded cards, counterfeit notes and Flash BTC Software offered through add-to-cart and checkout flows.
- Homepage: the claims "Skip verification steps" and "ATM cashout" with cryptocurrency-only payment, plus the unsupported "Your Trusted Source" and "Secure Handling" language.
- Registration record: domain registered 2024-06-27 (~2.4 years old at capture, 868 days), expiring 2027-06-27.
- Web archive: 117 snapshots from 2024-08-09 to 2026-10-23, a 805-day span, showing continuous presence of this storefront rather than a clean past.
- Sandbox browsing of the homepage: 21 requests sent data to unrecognised destinations.
Regulatory Verification Notes
On the pages read (the homepage, privacy policy, refund and returns policy, shipping page, two contact and information pages, and the clone-card and counterfeit-notes product pages), no legal entity, registration or licence, or regulator is named. The copyright line reads "Clone Cards, Counterfeit Notes 2026", which is a trading label rather than a legal entity. A real-world operator identity remains unverified. The legal and disclosure pages are thin and generic. The privacy policy is a stock template about website comments and a Gravatar hash. The refund policy refers to credit-card refunds, although the site takes only cryptocurrency. The pages do state a price range, a refund page and a contact page, but these do not substitute for accountability. The contact page points visitors to a community and lists counterfeit-note bundles rather than a verifiable business address or working channel. No licensed financial business could lawfully sell these goods, so absent licensing is not a gap awaiting repair. No third-party broker or regulatory-database entry was matched. The registration record lacks registrant details.
- Privacy policy page: a generic comment-and-cookie template with no named controller, company or address.
- Refund and returns policy page: describes credit-card refunds that the crypto-only checkout cannot use, and has no operator details.
- Hosting infrastructure: served from AS13335 (Cloudflare, Inc., US).
- Registration record: registrar NICENIC INTERNATIONAL GROUP CO., LIMITED; registrant details are missing from the record.
What to Verify Next
The page evidence leaves little to verify about the offering itself, so the steps are protective. First, do not treat the shop's trade names or its "24/7 support" and "tracked delivery" language as evidence of a real operator, and do not engage with any support channel it offers. Anyone who has already paid should contact their bank or the cryptocurrency exchange used and report the transaction to national cybercrime authorities. Anyone who has installed any "Flash BTC" software from this site should have the device checked before further use. Organisations that encounter this domain in mail or traffic should report it to their security team and block it. Confirming the site's official support or contact channels is pointless, since the operator is anonymous.
- Product pages: Flash BTC Software is offered as a downloadable tool alongside card and note sales.
- Checkout pages: "Crypto Payment Selection" with BTC and ETH leaves no chargeback route.
- Homepage: "Get up to 25% Discount for orders above £3000" pushes high-value orders.
Summary Verdict
The site is a critical-risk property. It openly trades in goods used for financial fraud, names no accountable operator, and is flagged by an outside alert. Its basic technical hygiene shows only that it operates; it does not show that the business is legitimate.
The network's abuse record was checked and showed no reports, as expected for a shared edge address. The TLS certificate seen at capture was a domain-validated certificate issued by YE1, valid until 2026-12-16. Hosting behind a CDN and a valid certificate are neutral facts, shared by sites of every kind. They carry no weight against the findings above.
Closing Assessment
This site should not be used for any purpose. Nothing should be bought from it, no payment made, and nothing downloaded or installed from it, and anyone who has already paid should act on the steps above promptly.
Written analysis generated 2026-11-15 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
15 findings contributed to this verdict, raised by governance, external reputation, page content, several checks together, registration and ownership and behaviour in a sandbox.
01 Governance
- The site's own pages offer illegal goods for sale (stolen card or bank data, counterfeit money, forged documents, illegal drugs, prescription drugs sold without a prescription, or darknet-market access), and that caps the score.Governance
rule:gov_illicit_goods_storefront
02 External reputation
- 4 VirusTotal engines marked this domain as malicious when the evidence was captured.External reputation
rule:EXT_BLACKLIST_HIGH
03 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
04 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
05 Registration and ownership
- The registration lookup did not return the domain's registrant.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
06 Behaviour in a sandbox
- The page exchanged network traffic with destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_TRAFFIC - The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS - The page made background requests to destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_XHR - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
- The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Third-party connections: 5 findings share one limit, because they all measure one fact: the page loads files from other hosts. The limit applied, so together they counted for less than their sum.
- Certificate and search-engine setup: 2 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Clonecardnotes
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of clonecardnotes.com.
- The request stayed on clonecardnotes.com. It was not redirected to another domain. Clear
- Registered through NICENIC INTERNATIONAL GROUP CO., LIMITED. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-06-27. Noted
- The earliest public archive of this site is from 2024-08-09. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 10 other sites it has analysed. 6 of them are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
- clonedcardstoreusa.com (Critical)
- cocainelovers.com (Critical)
- 18suite.com (Critical)
- cardingclub.ru (Critical)
- cloncardnotes.com (Critical)
- bscompany.es (Critical)
- emproproperties.com (Low trust)
- gitanocollection.com (Low trust)
- aaafinancebd.com (Low trust)
- baobimocan.vn
| Shared files (SHA-256) | b7a195865297eed840d6ddaf63453c4d.js 3d8595f77498f439f4877c1ea6bf58989dd527e5da8fa98d8cdfd4821e422f27 (6 sites) |
|---|---|
| 311e83a182b0d1ee9a5aefb10c3a4c25.js 6a504d775b4ba01c6c10470ecfd6b71d5b458555d17cee6c112270956a4ad6e1 (6 sites) | |
| e552f0e83b75c965d878d3eec8e3672d.js c54866b1fb1abb90f535eba4294066394df39027677af959455763c54ae58185 (6 sites) | |
| 8fddcde9f541ea3adb30580034f559b6.css 292ce5ca5f06d57da7e5d7343c0eb6f9190b774899e94cb7a669d4da793d73bd (5 sites) | |
| af39d452ae5ad62b2367a7352ee7bf45.js 516f7f4d6bb36f43c760760a9abeda29d111ad8c0e923de6aa8a1f6cec03a8ee (5 sites) | |
| e99757b4be8de7572e87267dff40ff3f.js a1650c7fb2284501b453cfb9895e55cdf0f70b38ee6f69a481f8e816fb4d95d7 (5 sites) | |
| 7ab4a530f755295c80f123e317f38f98.js 01f8ac9e9acb5e3154123968574c52e0cadbe454b96e01e69217270465329917 (4 sites) | |
| 6a7286844d59793a0175e3a333c934b7.js 3cc4ca170332e1c82941f1a5dc03bb85fc22d65fe4d518e34eeaabf04d8f9368 (4 sites) | |
| 5e5c7e9f80e74c4d34d6d7164d92c717.js 66a0e7a8b429b59471f410187654b3b0d93b9343b7647201175a3bf395ad7622 (4 sites) | |
| e96fab28042326ab71c18b7c19f4eb37.js a0d5e899feea460272c90a62b243e9240151f4d71e7b110a694a2e0653b25ed5 (4 sites) |
Showing 10 of the shared files, the most widely shared first.
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3035::ac43:9990 (a CDN edge address; the capture did not observe the server behind it, which a later check found, shown below) |
| Name servers | brit.ns.cloudflare.com, damon.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-16 |
| Domain age | 2.38 years (registered 2024-06-27) |
| Domain expiry | 2027-06-27 |
| Archive first seen | 2024-08-09 (2.3 years before capture) |
| Archive snapshots | 117 |
| Reputation | VirusTotal: 4 malicious, 3 suspicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
Server behind Cloudflare
The site is served through Cloudflare, which hides the address of the server behind it, and the capture itself saw only Cloudflare's addresses. A later check on 2026-11-15 found that server: asked directly for this site, the address below returned the same page (100% of the same words).
| Server behind the CDN | 111.90.156.119 (Shinjiru Technology Sdn Bhd, AS45839, MY) |
|---|---|
| Found from | mail server _dc-mx.737e291d2577.clonecardnotes.com |
Found only from free public records (certificate logs, mail and SPF records, Mnemonic passive DNS, addresses written in the page) and one ordinary request to the address. An earlier address is a record of the past, not proof of where the site runs today.
About this assessment
A trust score summarises the evidence TrustSniffer could collect about clonecardnotes.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.