Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
clonedcardstoreusa.com shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: A registration check came back incomplete: the registration lookup did not return the domain's registrant. That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
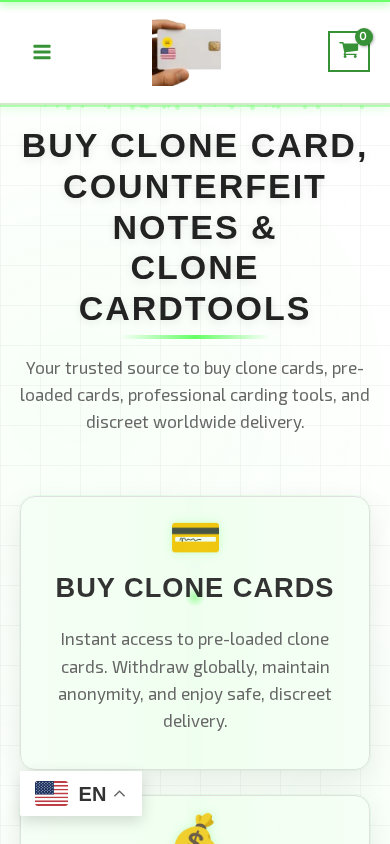
| How the site describes itself | A storefront selling clone payment cards, counterfeit banknotes and carding tools for crypto payment with discreet worldwide shipping. The offer is illegal and fraud-enabling, and the page gives no verifiable legal identity, licence, address or consistent brand. Page risk is critical. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- 6 VirusTotal engines (Fortinet, Kaspersky, Sophos among the engines that flagged it) marked this site as malicious when the evidence was captured on 2026-11-11, which meets TrustSniffer's bar for a confirmed listing. On its own it would limit the score to at most 24; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe confirmed external listing ceiling (at most 24) also applies, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 6 marked it malicious, 1 suspiciousVirusTotal; Fortinet, Kaspersky, Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 1.1 years oldRegistered 2025-10-15 | Clear |
| Web archive | Archived since 20231023 snapshots; the history predates the current registration (2025-10-15); an earlier owner may have held the name | Noted |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: 1 to 3 years at capture (registered 2025-10-15).
- Public web-archive history exists since 2023.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
6 VirusTotal engines, including Fortinet, Kaspersky, Sophos, marked this site as malicious; this meets TrustSniffer's bar for a confirmed listing.
Overview
The website clonedcardstoreusa.com is an online storefront that presents itself as a source of pre-loaded "clone" payment cards, counterfeit banknotes and carding tools. It advertises "Secure Worldwide Delivery" with payment in cryptocurrency. Its navigation offers product categories for cloned cards, counterfeit notes and carding tools, plus shipping, refund and account pages. Its apparent business model is selling fraud-enabling goods at fixed prices to anonymous buyers. No verifiable business identity stands behind the sales.
Scam/Impersonation Risk
This assessment is critical risk. The contradictory signals are confirmed and mutually reinforcing. An external reputation check flagged the domain as malicious across several engines, including three leading security vendors, which meets TrustSniffer's bar for a confirmed listing. That is a single source, not several corroborating ones. The site's own content independently supports a critical reading, because its stated product is itself illegal and fraud-enabling. The homepage offers "pre-loaded clone cards" so that buyers can "withdraw globally, maintain anonymity", and "counterfeit notes" described as "undetectable". A French-language line on the contact page, translated here as "Buy cloned ATM cards Global (balance $2500, 60 days)", confirms the same offer. The site also advertises that buyers should "opt for Bitcoin or Monero to layer anonymity over your transaction". It claims "encrypted ordering processes and no-log policies" and says it does not sell to first-time shoppers unless they were referred by an earlier customer. That combination of untraceable payment, anonymity and referral gating is typical of a storefront that avoids accountability. No brand impersonation or conflicting legal entity was detected. The risk comes from the goods offered, the external listing and the absence of any accountable operator. The page's own text contradicts itself in ways that undermine its credibility. Counterfeit notes are labelled "for educational and research use" yet "undetectable for legitimate private applications". Every clone card is priced at the same £199.90 whether the stated balance is $2,500 or $25,000+. A "discount" from £350.00 has no stated sale period. A template placeholder reading "[insert legitimate purpose, e.g., educational or novelty use]" is left in the text. Browser-behaviour testing was also adverse. The pages generated a high volume of requests to destinations TrustSniffer does not recognise, repeated console errors and large structural page changes after interaction, and a password form is present. The page template also shares characteristics with two other sites that were flagged as critical.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Registration record: the domain was registered in 2025 (about 1.1 years at capture) through NICENIC INTERNATIONAL GROUP CO., LIMITED.
- VirusTotal: 6 engines rated the domain malicious and 1 suspicious, including Fortinet, Kaspersky and Sophos. Google Safe Browsing had not listed it.
- Homepage and contact page: the offer of clone cards, counterfeit notes and carding tools, with crypto-only anonymous payment, appears in the site's own text. The contact page repeats it in French.
- Browser-behaviour testing: 29 requests sent data to destinations TrustSniffer does not recognise, 16 console errors were logged, and one password form was present.
Regulatory Verification Notes
On the pages read, the site discloses none of the identity and authorisation details expected of a financial-services seller. These are a legal entity, a registration or licence number and a regulator. The only expected disclosure present is a privacy policy, and that policy states that the site does not disclose a physical address. The refund page asserts compliance with "global consumer protection standards" without naming any authority or entity that could be held to them. The site's name changes from page to page. It appears as Buy-Clone-Cards.com on the contact and about pages and as ClonedCardStoreUSA.com in the homepage text. The about page calls it Clone Card Hub, and the privacy page is titled Psychedelic Store. The refund promise is also internally inconsistent, offering a 14-day full refund under a heading that reads "7-Day Exploration Guarantee". Claims of "verified status", "holographic seals" and "years of flawless deliveries" are unsupported by any checkable evidence. No third-party broker or regulator record was matched to the site. The inconsistent names and absent disclosures are consistent with the pages' own critical risk indicators. They are not a basis for treating the site as a regulated or accountable business.
- Privacy page: it says no physical address is disclosed. No legal entity, licence or regulator appears on the homepage, about page, contact page or shipping pages.
- About and contact pages: the site names differ across pages, as set out above.
- Web archive: 1,023 snapshots were captured between 2023-08-06 and 2026-10-23, a span of 1,174 days.
- Hosting and transport encryption: the site was served from AS13335 (Cloudflare, Inc., US). Its domain-validated TLS certificate was issued by WE1 and was valid until 2027-02-06 at capture. A valid certificate says nothing about the operator's legitimacy.
What to Verify Next
Verification here means confirming the harm rather than seeking assurance. Anyone who has already paid or shared personal or payment details with the site should contact their bank or payment provider and the national cybercrime or fraud-reporting authority. Cryptocurrency payments to a storefront of this kind are generally difficult to reverse, so that report should be made promptly. Organisations that encounter the domain in mail, advertising or referrals should treat it as a threat indicator. They should route it to their security team for blocking and escalation rather than test it further.
- Homepage and shipping pages: the address-entry and order flows are built to collect shipping details for goods the site describes as discreetly delivered.
- Contact page: the only channel offered is a message form.
- Account page: it is linked from the navigation and contains a password form.
Summary Verdict
The site presents critical risk across content, reputation and accountability. Its stated product is fraud-enabling, an external reputation check has flagged it, and no accountable operator is evident. The evidence shows a storefront built around illegal goods, not a legitimate business with administrative gaps. The assessment places the site at critical risk.
Infrastructure Integrity
The site sits behind Cloudflare's edge network, and none of its four observed addresses was identified as an origin host. The host's abuse record was checked and showed no reports. This carries no weight either way, because the network's reputation says nothing about the site's content. It does not offset the external listing or the nature of the offer.
Closing Assessment
The site should not be used for any purchase, payment or account registration, and no credentials or personal details should be entered on it. Visitors should leave the site and not follow referral links or messages that point to it. Any contact should be limited to reporting it.
Written analysis generated 2026-11-11 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
19 findings contributed to this verdict, raised by external reputation, page content, several checks together, code shared with sites rated critical, behaviour in a sandbox, and registration and ownership.
01 External reputation
- 6 VirusTotal engines, including a leading vendor (Fortinet, Kaspersky, Sophos), marked this domain as malicious when the evidence was captured, which TrustSniffer counts as a confirmed external listing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 Code shared with sites rated Critical
- The site runs the same code, or has code wired to the same hidden endpoint, as other sites TrustSniffer rated Critical.Code shared with sites rated Critical
rule:KIT_SHARED_WITH_CRITICAL_SITE
05 Behaviour in a sandbox
- The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION - The page exchanged network traffic with destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_TRAFFIC - The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS - The page made background requests to destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_XHR - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH - The page showed a password field during the sandbox session, and it could not be matched to a recognised brand's sign-in page.Behaviour in a sandbox
rule:BEHAV_PASSWORD_FORM_PRESENT - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
- The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY
06 Registration and ownership
- The registration lookup did not return the domain's registrant.Registration and ownership
rule:KF_WHOIS_INCOMPLETE - The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:Clonedcardstoreusa
- contact:email
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of clonedcardstoreusa.com.
- The request stayed on clonedcardstoreusa.com. It was not redirected to another domain. Clear
- Registered through NICENIC INTERNATIONAL GROUP CO., LIMITED. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-10-15. Noted
- The earliest public archive of this name is from 2023-08-06, before the current registration on 2025-10-15; an earlier owner may have held it. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 16 other sites it has analysed. 11 of them are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
- cocainelovers.com (Critical)
- trustedbillsandclones.com (Critical)
- 18suite.com (Critical)
- 2alb-atfal.com (Critical)
- cardingclub.ru (Critical)
- cloncardnotes.com (Critical)
- clonecardnotes.com (Critical)
- cocaineforsale.co (Critical)
- heroindistro.com (Critical)
- mytrippy.ca (Critical)
- bscompany.es (Critical)
- acblog.am (Low trust)
- ajaypipes.com (Low trust)
- athensems.gr (Low trust)
- aaafinancebd.com (Low trust)
- baobimocan.vn
| Shared files (SHA-256) | d4b4dd934e6d2b144239d0e477f44dc5.js d1840df3839d12f5805a78727e905f5a979856bea210ad5c919108f8044fdf1b (7 sites) |
|---|---|
| ab95a8d37cf283c8d6722db32ec31a24.js 17c54838ff27fd5ce4792f6a4da0905a39ecb723bb56085cb4ddf9157468ce42 (4 sites) | |
| 1c6df716953f870be76c3e88a69a326f.css 1b34d4c7324321e36db5d35f05bb011238a1326f89058a4399d028d1f6c47dd5 (4 sites) | |
| 8fddcde9f541ea3adb30580034f559b6.css 292ce5ca5f06d57da7e5d7343c0eb6f9190b774899e94cb7a669d4da793d73bd (4 sites) | |
| c5fd583e176fa5c734da0599bfa3dab0.css 398e2425ac154b75384c55af3fcb40cf68ef50e15714b9dda11bf54ee0b9fc35 (4 sites) | |
| b7a195865297eed840d6ddaf63453c4d.js 3d8595f77498f439f4877c1ea6bf58989dd527e5da8fa98d8cdfd4821e422f27 (4 sites) | |
| 311e83a182b0d1ee9a5aefb10c3a4c25.js 6a504d775b4ba01c6c10470ecfd6b71d5b458555d17cee6c112270956a4ad6e1 (4 sites) | |
| a2bf2605eba1c8badf2ff5339d3cbc65.js 8f7d8c84622b80c5cc0fd522bfbce892e5f20cdb1a182fc3accb000ee1bf3234 (4 sites) | |
| 7d12961cd5732bfcd20dbe4025801536.js bcd8482491d261c223749a5b352d5f29eea4560d9dd7bfa030dc270327c37eee (4 sites) | |
| e552f0e83b75c965d878d3eec8e3672d.js c54866b1fb1abb90f535eba4294066394df39027677af959455763c54ae58185 (4 sites) |
Showing 10 of the shared files, the most widely shared first.
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3033::6815:1338 (a CDN edge address; the server behind it was not observed) |
| Name servers | brit.ns.cloudflare.com, damon.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-02-06 |
| Domain age | 1.07 years (registered 2025-10-15) |
| Domain expiry | 2027-10-15 |
| Archive first seen | 2023-08-06 (3.3 years before capture) |
| Archive snapshots | 1023 |
| Reputation | VirusTotal: 6 malicious, 1 suspicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
The web archive has records of this name from 2023-08-06, before the current registration on 2025-10-15. That archive history predates the current registration, and an earlier owner may have held the name.
About this assessment
A trust score summarises the evidence TrustSniffer could collect about clonedcardstoreusa.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.