Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
decentralizedapps.pages.dev shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
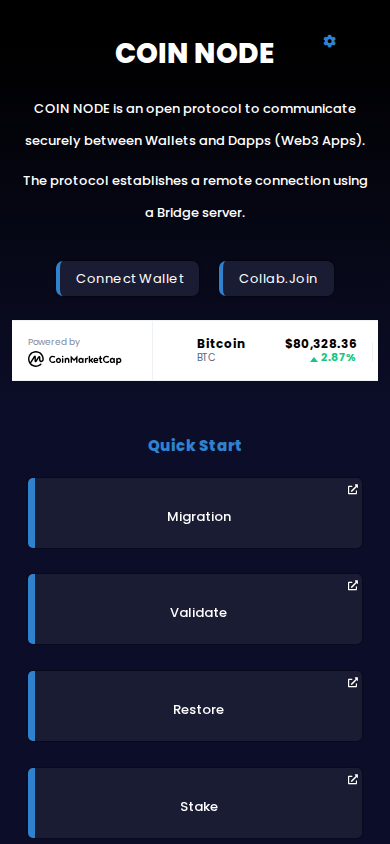
| How the site describes itself | A crypto wallet 'fix' and recovery landing page branded COIN NODE / Wallet Fix. It promotes wallet connection, token restore, airdrop claims and staking-reward harvesting with unverifiable usage statistics and no legal identity, contact details or pricing. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 14 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Listed as unsafeGoogle | Risk |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 2.2 years before captureWeb archive; a site on pages.dev has no registration of its own | Clear |
| Web archive | Archived since 202412 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: 1 to 3 years before capture (web archive; a site on pages.dev has no registration of its own).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
Fortinet, Google, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Overview
This website is a single-page crypto landing page branded "COIN NODE", with a footer that reads "Wallet Fix". It describes itself as an open protocol for securely connecting wallets and Web3 apps. Its main call to action is a "Connect Wallet" button, and its menu offers wallet repair, token restoration and reward-claiming services. The apparent business model is to draw visitors into linking a crypto wallet, and no pricing, fee structure or payment terms are disclosed.
Scam/Impersonation Risk
Confirmed contradictory signals are present, and this is the decisive feature of the assessment. A major browser-security service classifies the site as social engineering, and several independent security engines separately flag it as malicious. The site is therefore blacklisted by multiple external sources, and this alone places it in an elevated-risk posture. The page content reinforces that conclusion. It offers "Restore tokens", "Claim Airdrop Rewards", "Harvest my stakings", "Unstake Tokens", "Recovery", "LP Lock" and "NFT Mint" as one-click services behind wallet connection. This is the typical lure of wallet-draining and fake-recovery schemes, where a victim is invited to "fix" a problem that may not exist. The headline protocol description is also inconsistent with the recovery offering, and the site carries two different brand names. The claims "200k+ resolved issues", "50K+ active wallets" and "100+ contributors" are unsupported by any audit, case study, named contributor or third-party reference. The footer copyright year of 2022 pre-dates the domain's registration by about two years, which undermines the implied operating history. The live price ticker for Bitcoin, Ether, XRP and other major tokens lends borrowed credibility but has no bearing on the service itself. Automated browsing did not record an active wallet-drainer or clipboard-hijack routine. This is not exculpatory, because the harm path here is the wallet-connection step itself. The domain also sits on a free shared-hosting subdomain, and several sibling sites on that platform with similar wallet-fix themes are separately flagged.
- Homepage: the "Connect Wallet" button and the "Get Started" prompt ("Ready to resolve your blockchain issues?") are the only calls to action. The service list includes "Restore tokens", "Claim Airdrop Rewards" and "Harvest my stakings".
- Homepage: the statistics counters "50K+ active wallets", "200k+ resolved issues" and "100+ contributors" have no substantiation anywhere on the page. The footer reads "Wallet Fix © 2022", while the header brand is "COIN NODE".
- Domain provenance: the domain was registered about 2.2 years ago (first archived June 2024), so it post-dates the 2022 copyright claim.
- Web archive: 12 snapshots across 2024–2026 (3 years tracked), a thin history with no record of an established service.
- External reputation: 14 security engines rate the site malicious and 1 rates it suspicious. Three tier-one vendors are among them, and the browser-security classification is "social engineering".
Regulatory Verification Notes
The site discloses no operating company, no registered address, no contact channel, no refund or dispute policy and no licensing or registration status. No audit is cited for a service that would take custody-level access to user wallets, so its identity cannot be independently connected to any real-world person or business. There is also no on-page legal or terms content, so the usual regulatory touchpoints for financial or custodial services cannot be assessed. No third-party broker or regulator record matches the site. This absence of disclosure is separate from the threat findings above, but it removes any ordinary recourse path for a harmed user.
- Homepage and footer: no legal entity, address, licence number, pricing, fee schedule or terms of service are shown.
- Transport security: a valid domain-validated TLS certificate issued by WE1, valid to 2026-12-18. This confirms only encrypted transport, not operator legitimacy.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
What to Verify Next
Verification here is mainly about establishing exposure and safe handling, not about vetting the operator for engagement. Anyone who has already interacted with the site should check the wallet's approval and permission list for unfamiliar contract authorisations and revoke them from a clean device. Any asset-recovery or wallet-fix need should be taken to the wallet vendor's own official support, reached by typing its address manually. The official support channel of the relevant wallet or token project should be asked whether the "claim", "airdrop" or "restore" offers are genuine. Any claim of regulated or licensed status should be checked directly against the relevant public registry, and the site's own assertions should not be relied on. The official support and contact channels of any project the site names should be confirmed independently, offline where possible.
- Homepage: the "Connect Wallet" flow and the recovery-themed service menu are the interaction points that warrant the exposure review.
- Homepage: no contact route is published, so no channel can be validated from the site itself.
- Browser-security classification: social engineering, indicating that a user-deception flow is the expected threat.
Summary Verdict
The site carries a critical, high-risk trust posture. Active external threat flags, together with a wallet-access lure that has no legal identity, no contact route and no pricing, outweigh every neutral technical attribute. Available evidence points to a deceptive crypto "fix and claim" front end, not a legitimate service.
Infrastructure Integrity
The site is delivered through Cloudflare's CDN and web application firewall, and all observed addresses are edge servers, so the origin host is not visible. The TLS certificate is valid and the hosting reputation is clean. These are only mitigating factors. They show the site is competently fronted, not that its content or operator is trustworthy, and they cannot offset the external threat detections. Edge-only visibility also prevents independent hosting verification and can mask rapid content changes.
Closing Assessment
The site should not be used for any wallet, login, credential or financial interaction. Wallets should not be connected, seed phrases or private keys should never be entered, and nothing should be signed or approved. Browsing for informational purposes only is the maximum reasonable use, and anyone who has already connected a wallet should treat it as potentially exposed.
Written analysis generated 2026-11-05 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content and several checks together.
01 External reputation
- A confirmed external listing marks this domain as malicious: at least five security engines including a leading vendor, ten engines, or Google Safe Browsing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of decentralizedapps.pages.dev.
- The request stayed on decentralizedapps.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2024-06-17. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 4 other sites it has analysed. All 4 are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
- coisynctechresolve.pages.dev (Critical)
- decentralizedapp.pages.dev (Critical)
- fixalgo.pages.dev (Critical)
- polymarket-en.firebaseapp.com (Critical)
| Shared files (SHA-256) | main.css 39ba049d03abe5def80830ba38d0f2b432dd7374cac67ffd3c800d9bcc551164 (5 sites) |
|---|---|
| walletpage.css 7f27584b0c891c2340eae90868b94b543d1a9d149bc9c6e9407d127320f57b98 (5 sites) | |
| jquery3.6.0.min.js ce9d07500ad91ec2b524c270764ec4c9a33e78320d8d374ec400ede488f6251b (3 sites) | |
| index.css f5d9810298c6009cdf9fbbbbf0c695180feb4a8960b8e9116b412a648eaf61cf (3 sites) |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:310c::ac42:2fb0 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-18 |
| First seen (web archive) | 2.20 years before capture; a site on pages.dev has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2024-06-17 (2.4 years before capture) |
| Archive snapshots | 12 |
| Reputation | VirusTotal: 14 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 1 match |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about decentralizedapps.pages.dev at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.