Verdict
External threat listings named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
polymarket-en.firebaseapp.com shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-13 and re-scored on 2026-11-15. The certificate, the registration age and the page content describe the site as it was on 2026-11-13.
- External threat sources confirmed a listing for this site when the evidence was captured (VirusTotal, a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-24)). It was not re-queried for this version. On its own the alert would limit the score to at most 24; the threat-listing ceiling holds it at 5, because the listing names the site itself as the source.
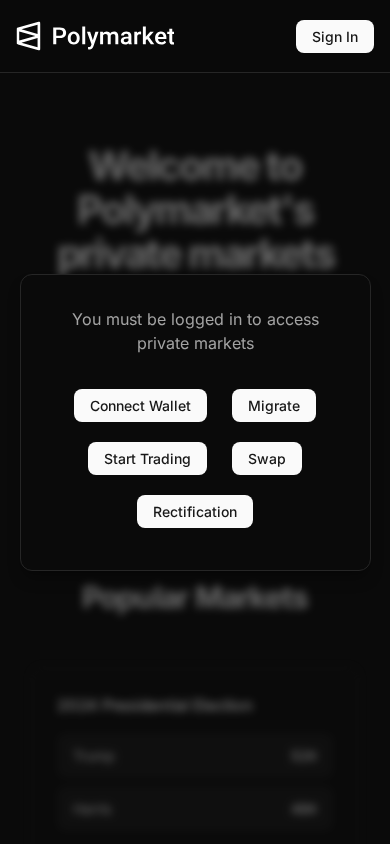
- When captured, this address served a placeholder (a suspension notice, a server's default page or a coming-soon page) instead of the site; the page and sandbox findings below were measured on that placeholder.
- The real-world operator identity was not independently verified.
- These checks returned no result: AI reading of the page.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 5/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | Threat-listing ceilingA threat-intelligence feed TrustSniffer monitors listed this site itself as the source of a threat when the evidence was captured (last seen 2026-10-24), and that listing caps the score. The cloaking ceiling and the independent sources ceiling (at most 24) also apply, but the score is below them. | Risk |
|---|---|---|
| Malware engines | 2 marked it malicious, 2 suspiciousVirusTotal | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 1% confidenceAbuseIPDB, 3 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by WR3 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
The address polymarket-en.firebaseapp.com is a subdomain on Google's Firebase hosting platform whose name borrows the Polymarket brand, which the site is not. When captured on 13 November 2026, it served a placeholder page with no content of its own, no forms, and no stated product, operator, or business model. Its apparent purpose cannot be established from the page itself. Its name, combined with the threat findings below, points to a lookalike built to trade on a recognised prediction-market brand.
Scam/Impersonation Risk
The evidence shows critical risk and contradictions that meet the bar for a confirmed listing. A threat-intelligence listing, last seen on 24 October 2026, classifies this address as the actor in a phishing case. VirusTotal separately reported two engines as malicious and two as suspicious, and no leading vendor was among the malicious verdicts. These two independent sources align. The listing is what holds the score down, through the threat-listing ceiling. The measurements taken on the captured placeholder page carry further scored findings. The landing content differed completely between visits, a pattern consistent with cloaking. Roughly two-thirds of the files the page loaded came from other domains. Ten requests sent data to other hosts, four of them to destinations TrustSniffer does not recognise. The site's identity could not be tied to any real-world operator, so nothing links it to the Polymarket brand it names. No conflicting legal identities were observed. The score reflects the threat listing and these behavioural findings, not any claim the site makes.
- External threat listing: a phishing classification with the site as actor, last seen 24 October 2026.
- VirusTotal: 2 engines malicious and 2 suspicious, with no top-tier vendor among the malicious verdicts.
- Captured homepage behaviour: strong cloaking indicators, with 63.7% of files loaded from other domains and 4 requests to unrecognised destinations.
- Hosting registration: the address is a tenant subdomain of a hosting platform, so it has no registration record of its own.
Regulatory Verification Notes
On the single page read, a placeholder, no contact channels and no terms or privacy statement were found. This is a gap on the pages read, not a conclusion about the site as a whole. The page makes no claims about licensing, registration, or regulated activity, and no third-party broker or regulator record matched this address. The page's only on-site identity cue is a name echoing the hosting subdomain itself. The operator's identity remains unverified, and no legitimacy can be inferred from the page.
- Homepage (placeholder): no contact channels and no terms or privacy page on the pages read.
- Network record: served from AS54113 (Fastly, Inc., US).
- Transport encryption: a domain-validated certificate issued by WR3, valid to 25 January 2027. Such a certificate shows only that the connection is encrypted, not who operates the site.
- Broker reputation database: no match for this site.
What to Verify Next
Anyone who reached this address through a message, advertisement, or search result should trace that referral and treat the link as suspect. Access to Polymarket should come only from an address independently known to belong to it, such as one entered by hand or taken from the company's official channels. Any official support or contact channel should be confirmed through that same independent route. If the address was received by message or social post, the sender's account should be checked as a possible source of the phishing.
- Hosting record: the hostname is a platform-issued subdomain, which anyone can create under a brand-like name.
- Threat listing: the 24 October 2026 listing suggests the address has already been used to reach visitors.
- Homepage (placeholder): it offered no verifiable operator information to confirm.
Summary Verdict
The site sits at the critical-risk end of the scale. A confirmed phishing listing aligns with sandbox behaviour consistent with cloaking and with data sent to unfamiliar destinations. No identity evidence offsets these findings, and the brand-mimicking hostname adds to the concern.
Infrastructure Integrity
The site is served through the Fastly content delivery network, from two edge addresses on the Fastly network in the United States. The origin server was not observed. Edge delivery is neutral for this assessment, and it does not mitigate the findings above. The three abuse reports on the Google-operated shared address belong to that provider's shared infrastructure, not specifically to this site.
Closing Assessment
The address should be treated as a critical risk and not relied on as an official presence of the brand it names. Visitors should not follow its links, connect any account or wallet, or supply personal or payment information through anything reached from it.
Written analysis generated 2026-11-15 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
7 findings contributed to this verdict, raised by governance, behaviour in a sandbox and external reputation.
When captured, this address served a placeholder (a suspension notice, a server's default page or a coming-soon page) instead of the site; the page and sandbox findings below were measured on that placeholder.
01 Governance
- The page showed different content to different visitor profiles during the sandbox session, and a separate warning sign backs that up, so the score is capped. This ceiling applies, but the score is below it, so it does not set the score.Governance
rule:GOV_CLOAKING - A threat-intelligence feed TrustSniffer monitors listed this site itself as the source of a threat when the evidence was captured (last seen 2026-10-24), and that listing caps the score.Governance
rule:gov_active_threat_listing
02 Behaviour in a sandbox
- During the sandbox session the page showed markedly different content to different visitor profiles. This can have ordinary causes such as bot defence, and it can also hide content from checks.Behaviour in a sandbox
rule:BEHAV_CLOAKING_STRONG - A large share of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_MODERATE - Many of the responses the page received looked generated rather than served normally.Behaviour in a sandbox
rule:BEHAV_SYNTHETIC_RESPONSES_HIGH - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
03 External reputation
- 2 VirusTotal engines marked this domain as malicious when the evidence was captured.External reputation
rule:EXT_BLACKLIST_MEDIUM
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Third-party connections: 2 findings share one limit, because they all measure one fact: the page loads files from other hosts. Together they stayed under the limit.
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 3 reports on hosting IP 2620:0:890::100 (FASTLY), 1% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|
The identity check returned no result for this report.
- AI page analysis unavailable (page captured; identity not AI-verified)
What TrustSniffer observed
First-party facts recorded during the assessment of polymarket-en.firebaseapp.com.
- It is hosted on FASTLY, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files as 9 other sites it has analysed. All 9 are rated Critical on their own evidence.
Shared code shows that these sites were built from the same toolkit. It does not by itself show who operates them.
- blockswalletschain.web.app (Critical)
- coisynctechresolve.pages.dev (Critical)
- decentralizedapp.pages.dev (Critical)
- decentralizedapps.pages.dev (Critical)
- fixalgo.pages.dev (Critical)
- iost-net.web.app (Critical)
- kinetiq-en.firebaseapp.com (Critical)
- kinetiq-en.web.app (Critical)
- solcard-en.web.app (Critical)
| Shared files (SHA-256) | main.css 39ba049d03abe5def80830ba38d0f2b432dd7374cac67ffd3c800d9bcc551164 (10 sites) |
|---|---|
| walletpage.css 7f27584b0c891c2340eae90868b94b543d1a9d149bc9c6e9407d127320f57b98 (10 sites) | |
| jquery3.6.0.min.js ce9d07500ad91ec2b524c270764ec4c9a33e78320d8d374ec400ede488f6251b (3 sites) | |
| index.css f5d9810298c6009cdf9fbbbbf0c695180feb4a8960b8e9116b412a648eaf61cf (3 sites) |
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | FASTLY - Fastly, Inc. |
| Network registered in | US |
| Server IP | 2620:0:890::100 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (fastly) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR3 |
| SSL expiry | 2027-01-25 |
| First seen (web archive) | Not available (the web archive has no record of this address; a site on firebaseapp.com has no registration of its own) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 2 malicious, 2 suspicious | AbuseIPDB (CDN edge address, not the host): 1% confidence, 3 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about polymarket-en.firebaseapp.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.