Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
firelight-voting-allocation.web.app shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on web.app, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| How the site describes itself | Firelight Voting is a Phase 2 governance interface for eligible participants of the Firelight DeFi protocol. Users connect a wallet to verify eligibility, review proposals, and submit votes, and the page also mentions claiming voting-pool rewards. The page makes strong 'institutional-grade' claims supported only by a testimonial, with no visible audit, legal entity, or contact details. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-22 and re-scored on 2026-11-04. The certificate, the registration age and the page content describe the site as it was on 2026-10-22.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 3% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 5 months before captureWeb archive; a site on web.app has no registration of its own | Risk |
| Web archive | Archived since 20264 snapshots; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by WR4 | Noted |
The page as captured
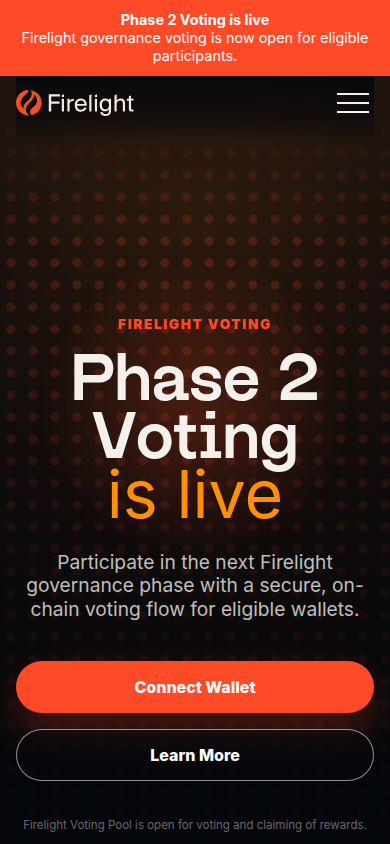
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: less than 1 year before capture (web archive; a site on web.app has no registration of its own).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
Firelight Voting is a single-page governance interface presented as "Phase 2 Voting is live" for eligible participants of the Firelight DeFi protocol, which describes itself as turning staked digital assets into protection or coverage for DeFi. The page invites visitors to connect a crypto wallet, check eligibility, read a proposal, submit a vote, and claim rewards from a "Voting Pool". It is built as a wallet-driven decentralized-application front end. Its apparent purpose is to funnel protocol participants into an on-chain wallet interaction.
Scam/Impersonation Risk
The site is blacklisted: several independent threat-intelligence sources currently flag it as malicious, and a separate external blacklist signal corroborates this. This is the decisive finding. It calls for a security-forward posture regardless of how professional the page looks. No conflicting legal-entity names were found, and no brand impersonation was detected. The behavioural analysis also found no credential forms, hidden forms, clipboard manipulation, wallet-drainer behaviour, or content cloaking. The blacklisting therefore stands without a matching on-page exploit mechanic. That does not make the page safe, because the page's core function is to get a visitor to connect a wallet. The homepage promotes "institutional-grade embedded coverage for on-chain solutions", but its only support is a single testimonial from a named co-founder of a third-party firm, Sentora. No audit, security review, or verifiable partner confirmation is shown. The page also advertises claiming rewards from a voting pool without saying how those rewards are funded, what fees or deposit terms apply, or what the participant risks. That combination of an unproven credibility claim, an unexplained reward mechanic, and a wallet-connect prompt is the pattern commonly used in fake governance or airdrop-style lures. Combined with the external flags, it keeps the risk elevated.
- Homepage: multiple independent threat-intelligence engines currently classify the domain as malicious, and an external blacklist signal is also active.
- Homepage: the "Institutional-grade" statement is backed only by a co-founder testimonial. No audit or security-review reference appears on the page.
- Homepage: the "Voting Pool is open for voting and claiming of rewards" banner gives no reward source, fee, or deposit terms.
- Domain provenance: registered about 0.44 years ago (~160 days), with 4 archive snapshots, all in 2026 (first 2026-05-14, last 2026-05-19; 1 year tracked).
Regulatory Verification Notes
The page identifies its operator only as "© 2026 Firelight". It names no legal entity, jurisdiction, registration number, license, or contact address. It carries a securities and advice disclaimer, which does not substitute for operator identity. The page offers no regulatory standing that could be checked, and the real-world operator remains unverified. This is a disclosure gap that adds to, but is not itself the basis of, the cautionary conclusion. Ownership and governance opacity are present. The site runs as a subdomain on a shared hosting platform rather than on a standalone registered domain, so the registration says little about the operator. Social links point to Medium, X, and Discord. These are unauthenticated from the page's perspective and carry no weight as identity proof. No third-party broker or regulatory-database match exists for the site, so there is no external reputational context to offset the threat flags.
- Homepage footer: the only attribution is "© 2026 Firelight", with no named company, address, or licence reference.
- Homepage: no contact details of any kind are published.
- Transport security: the TLS certificate is domain-validated (DV), issued by WR4, and valid to 2026-12-22. It confirms an encrypted connection, not operator identity.
- Hosting: served from AS54113 (FASTLY - Fastly, Inc., US).
What to Verify Next
Before any interaction, confirm independently whether a Phase 2 voting event exists. Use the protocol's officially published channels, reached through a route that does not involve any link, button, or social icon on this page. Confirm directly with Sentora that its co-founder gave the quoted endorsement. Request a published smart-contract audit and a named legal entity for Firelight from the protocol's official documentation. If the protocol's official channels do not recognize this address, report it to the hosting platform's abuse desk.
- Homepage: the wallet-connect prompt is the only action path, so confirming the official voting address is the key check.
- Homepage: the testimonial is attributed to Jesus Rodriguez, Co-Founder and CPO of Sentora, which makes it directly checkable with that firm.
- Homepage: the page lists no audit, so the audit request has no on-page reference to check against.
Summary Verdict
The overall posture is high risk. Active threat-intelligence detections, an unverified operator, and a wallet-centred reward flow with unsupported credibility claims converge on a clearly cautionary classification. The absence of overt exploit behaviour in the page's code does not outweigh these signals.
Infrastructure Integrity
The site is delivered through Fastly's CDN and WAF. Only edge addresses were observable, so the origin host cannot be independently identified, and edge-only visibility can mask rapid content swaps. Protective infrastructure and a valid certificate are mitigating factors only, and they cannot offset the threat detections. Four abuse reports exist on the shared CDN address range. Because that address serves many tenants, those reports are attributed to shared infrastructure and are not treated as evidence against this site specifically.
Closing Assessment
The site should be treated as read-only content at most. Wallets should not be connected, transactions or signature requests should not be approved, and no credentials or funds should be entered or committed until the protocol's official channels confirm this voting flow. Anyone who has already connected a wallet here should revoke token approvals and review recent activity.
Written analysis generated 2026-11-04 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, history in the web archive, page content, hosting and network, and registration and ownership.
01 External reputation
- Three or more VirusTotal engines, or two including a leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_HIGH
02 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
03 Page content
- The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
04 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, three to six months before capture.Hosting and network
rule:DNS_YOUNG_6M
05 Registration and ownership
- As a site on web.app, this address has no registration record of its own (the platform's domain is registered, not the site).Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 4 reports on hosting IP 2620:0:890::100 (FASTLY), 3% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of firelight-voting-allocation.web.app.
- The request stayed on firelight-voting-allocation.web.app. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-05-14. Watch
- It is hosted on FASTLY, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site has code that posts to the same Telegram bot or chat as 3 other sites it has analysed. All 3 are rated Critical on their own evidence.
A shared identifier links these sites. It does not by itself show who operates them.
- firelight-voting-allocations.web.app (Critical)
- firelight-voting.web.app (Critical)
- firelight-voting-reward.web.app (Critical)
| Shared identifiers | Telegram bot: 8249651820 |
|---|
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | FASTLY - Fastly, Inc. |
| Network registered in | US |
| Server IP | 2620:0:890::100 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (fastly) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR4 |
| SSL expiry | 2026-12-22 |
| First seen (web archive) | 161 days before capture; a site on web.app has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2026-05-14 (161 days before capture) |
| Archive snapshots | 4 |
| Reputation | VirusTotal: 4 malicious | AbuseIPDB (CDN edge address, not the host): 3% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about firelight-voting-allocation.web.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.