Verdict
External threat listings named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
firelight-voting-reward.web.app shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: The governance checks raised a concern: a threat-intelligence listing limits the score; as a site on web.app, this address has no registration record of its own (the platform's domain is registered, not the site). The findings below give the detail.
| How the site describes itself | Firelight Voting Phase 2 page inviting eligible wallet holders to connect a wallet, check eligibility, vote on-chain, and claim rewards. It makes strong institutional and coverage claims without naming a legal entity, licence, regulator, audit, or direct contact channel. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-13 and re-scored on 2026-11-15. The certificate, the registration age and the page content describe the site as it was on 2026-11-13.
- External threat sources confirmed a listing for this site when the evidence was captured (VirusTotal, a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-18)). It was not re-queried for this version. On its own the alert would limit the score to at most 24; the threat-listing ceiling holds it at 5, because the listing names the site itself as the source.
- The real-world operator identity was not independently verified.
- These checks returned no result: web archive lookup.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 5/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | Threat-listing ceilingA threat-intelligence feed TrustSniffer monitors listed this site itself as the source of a threat when the evidence was captured (last seen 2026-10-18), and that listing caps the score. The independent sources ceiling (at most 24) also applies, but the score is below it. | Risk |
|---|---|---|
| Malware engines | 2 marked it malicious, 2 suspiciousVirusTotal | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 1% confidenceAbuseIPDB, 3 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by WR3 | Noted |
| Hosted by | FASTLYNetwork registered in US | Noted |
The page as captured
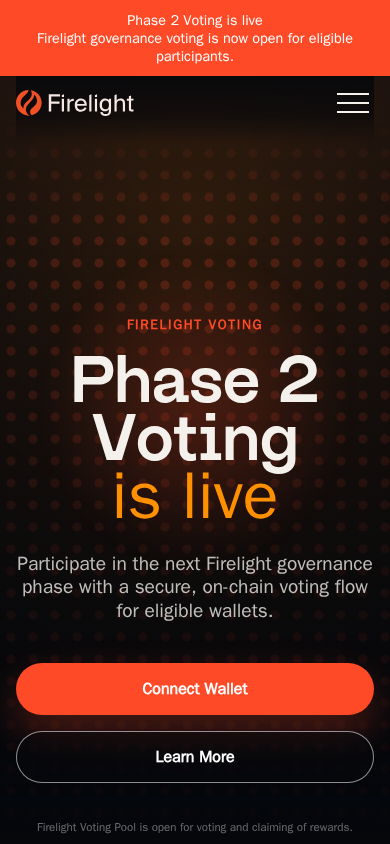
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
Firelight Voting Phase 2 is a single-page, wallet-based governance voting interface that presents itself as part of the Firelight DeFi protocol, which says it turns staked digital assets into coverage against DeFi risk. The page tells eligible wallet holders that a Phase 2 vote is "live". It walks them through connecting a wallet, checking eligibility, voting on-chain and claiming rewards, and it says the voting pool is "open for voting and claiming of rewards". It is hosted as a subdomain on a public web-app hosting platform rather than on a domain of its own, and its apparent purpose is to draw wallet holders into a connection and reward-claim flow.
Scam/Impersonation Risk
This site carries critical risk, and contradictory signals are present. Two independent sources align on a confirmed listing. A security-engine aggregator rated the address malicious on two engines and suspicious on two more, and none of the leading vendors was among the malicious detections. Separately, a threat-intelligence feed classified the site as a phishing source, with the site itself in the acting role rather than as a victim. That listing was last seen on 18 October 2026. The threat-listing ceiling is what holds the score down. The page analysis did not detect impersonation of a specific brand. Even so, the address uses the Firelight name on a generic hosting subdomain, and nothing independently links it to the operator of the real protocol. The site only says it is Firelight, so the claim is unverified. A second address on the same hosting platform, with a near-identical Firelight voting name, was also flagged. The page asks visitors to connect a wallet and claim rewards, and it never explains where the rewards come from or how value flows. That is the typical shape of a wallet-draining lure. The browser capture adds a consistent picture: heavy outbound traffic to other hosts, including destinations TrustSniffer does not recognise, and a high number of console errors. Both were scored findings and both count toward the score. The page contains no login or payment form. The exposure lies in the wallet-connection and claim flow.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- VirusTotal: two engines malicious and two suspicious at capture on 13 November 2026, with no top-tier vendor among the malicious detections.
- Threat listing: phishing classification, site in the acting role, last seen 18 October 2026, aligned with the VirusTotal result.
- Browser capture of the homepage: 37 requests sent data to other hosts, 9 of them to destinations TrustSniffer does not recognise, and 12 console errors were logged.
- Platform sibling: a similarly named Firelight voting address on the same hosting platform was flagged.
Regulatory Verification Notes
On the single page read, the site shows a generic informational disclaimer and links to Terms of Use and a Privacy Policy. It shows no contract address, no legal entity, no licence, no regulator, no audit and no direct contact channel. For a protocol asking users to connect wallets and claim rewards, these are material gaps on the pages read. The page's own wording is also inconsistent. The footer says nothing on the site is an offer or recommendation, while the body actively invites wallet connection and reward claiming. The "institutional-grade embedded coverage" and "capital-efficient, large-scale protocol" claims are the site's own and are backed by no evidence on the page. The page attributes its endorsing quote to a person it names as Co-Founder and CPO of Sentora, but nothing on the page substantiates that attribution. No broker-reputation match exists, so no third-party regulatory signal is available either way. The site has no registration of its own because it is a subdomain on the hosting platform.
- Homepage: the disclaimer and the Terms and Privacy links are present. No contract address, entity name, licence or audit appears on the page read.
- Homepage: the stated disclaimer conflicts with the on-page invitation to connect a wallet and claim rewards.
- Homepage: the endorsing quote is attributed to a named co-founder of a third-party firm, with no corroboration on the page.
- Transport encryption: the certificate was issued by WR3 at domain-validation level and was valid until 2027-01-25 at capture. This shows an encrypted connection only, not the operator's identity.
What to Verify Next
Any Phase 2 vote should be confirmed through the Firelight protocol's official channels, reached by a route that does not pass through this page. The channels the site itself links to are not independent evidence. Any contract address or reward mechanism should be compared against the protocol's published documentation before a wallet is connected. The Sentora attribution should be checked with that firm directly. A wallet that has already been connected to this address should have its token approvals reviewed and revoked.
- Homepage: the only outbound links are to Medium, Docs, X and Discord. These are links the site publishes itself, so they do not count as independent confirmation.
- Homepage: the voting flow runs entirely through a wallet-connect prompt, with no forms.
- Hosting platform: the address is a subdomain on the web.app platform, so no registration record ties it to the protocol's operator.
Summary Verdict
The site carries critical risk. Its identity as the Firelight protocol is unverified, and independent listings classify it as a phishing source. The few technical positives do not change that assessment.
Infrastructure Integrity
The site is served through the Fastly CDN from AS54113 in the United States, using two edge addresses. No origin server address was observed. A CDN is neutral here and offsets none of the reputation findings. Three abuse reports on the shared edge address, which is a Content Delivery Network address operated by Google, relate to that shared provider infrastructure rather than to this site specifically.
Closing Assessment
Wallets should not be connected to this address, no transactions or signatures should be approved, and no rewards should be claimed through it. Any Firelight governance activity should be accessed only through routes reached independently of this page.
Written analysis generated 2026-11-15 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
14 findings contributed to this verdict, raised by governance, page content, behaviour in a sandbox, external reputation, and registration and ownership.
01 Governance
- A threat-intelligence feed TrustSniffer monitors listed this site itself as the source of a threat when the evidence was captured (last seen 2026-10-18), and that listing caps the score.Governance
rule:gov_active_threat_listing
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED - The page refers to crypto without naming a specific token, a weak caution signal on its own.Page content
rule:PAGE_CRYPTO_PRESENT_MILD
03 Behaviour in a sandbox
- The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH - The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
04 External reputation
- 2 VirusTotal engines marked this domain as malicious when the evidence was captured.External reputation
rule:EXT_BLACKLIST_MEDIUM
05 Registration and ownership
- As a site on web.app, this address has no registration record of its own (the platform's domain is registered, not the site).Registration and ownership
rule:KF_WHOIS_INCOMPLETE
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Third-party connections: 3 findings share one limit, because they all measure one fact: the page loads files from other hosts. Together they stayed under the limit.
- Page quality: 2 findings share one limit, because each is weak evidence on its own. Together they stayed under the limit.
- Certificate and search-engine setup: 2 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 3 reports on hosting IP 2620:0:890::100 (FASTLY), 1% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Firelight Voting
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of firelight-voting-reward.web.app.
- The request stayed on firelight-voting-reward.web.app. It was not redirected to another domain. Clear
- It is hosted on FASTLY, a network registered in US. Noted
Code shared with other sites rated Critical
TrustSniffer found that this site serves the same distinctive code files and has code that posts to the same Telegram bot or chat as 3 other sites it has analysed. All 3 are rated Critical on their own evidence.
Shared code and shared identifiers show that these sites were built from the same toolkit or are linked by the same identifier. It does not by itself show who operates them.
- firelight-voting-allocation.web.app (Critical)
- firelight-voting-allocations.web.app (Critical)
- firelight-voting.web.app (Critical)
| Shared identifiers | Telegram bot: 8249651820 |
|---|
| Shared files (SHA-256) | styles.css 60ee615a5b1bbb509f23c0fd8dd552793d474d2b699f3b36d433430ea8558564 (3 sites) |
|---|---|
| SwapController-DB62DvNi.js 06b13c78aacdeb7d1658e4ca91d6627608ce883886706f5f253d4e74589cd98c | |
| index-BhPM6go6.js 0eee3b52ef2765219473e9dfb5dca2397af1c083e14291a78ebac00d9c1df78e | |
| index-ICeLzCcb.js 107ddd0ed5082ed51530ceade302f86944956b05af111df7e3d3d47bdfbe4dce | |
| index-BWyQ8YFH.js 1bd2f2008f79bb2b2450155aadad6725c42e0dfe16e2a6a0b5da4d9313bbf71e | |
| index-37_-OFUM.js 1c94b15601d7d3e9838ffdeffa6e77ae381d583ce273241f87fbc7e62b4813f9 | |
| index-DVQW-upq.js 1e9c293a0f69c68549c95c93bdc19d438b3cea078f683b368933df3be5eef40f | |
| index-IDOIhBpQ.css 23ae2e40529591fd3fb5d91149dbc093d7f508b7025dcdf0bfaf0a77da35e9f2 | |
| socials-Brb0_Mjh.js 2791610c0bb44e04762ad9c04844613dd43a2a8b84c97d792694a36716de33ea | |
| index-Qos94IS_.js 29cd83ab96afdeb71d2a50ec53c7bd39a0f87ef622ae4cd30baf41bdb929b33c |
Showing 10 of the shared files, the most widely shared first.
Two sites are linked only by two or more shared distinctive files or one shared identifier: an endpoint written into the page's code (a Cloudflare Worker or a Telegram bot), a wallet address shown on the page (checksum-validated), a contact or an analytics ID. Common libraries, platform files, images, well-known contracts, a brand's own accounts and anything also used by a site rated Moderate or High are excluded. Contact details (Telegram, WhatsApp, phone, email) are withheld. A shared file can be checked by its SHA-256 hash.
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | FASTLY - Fastly, Inc. |
| Network registered in | US |
| Server IP | 2620:0:890::100 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (fastly) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR3 |
| SSL expiry | 2027-01-25 |
| First seen (web archive) | Not available (the web archive has no record of this address; a site on web.app has no registration of its own) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 2 malicious, 2 suspicious | AbuseIPDB (CDN edge address, not the host): 1% confidence, 3 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about firelight-voting-reward.web.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.