Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
listadao.app shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 6 months oldMost scam domains are under a year old | Risk |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
| Hosted by | CLOUDFLARENETServer in US | Noted |
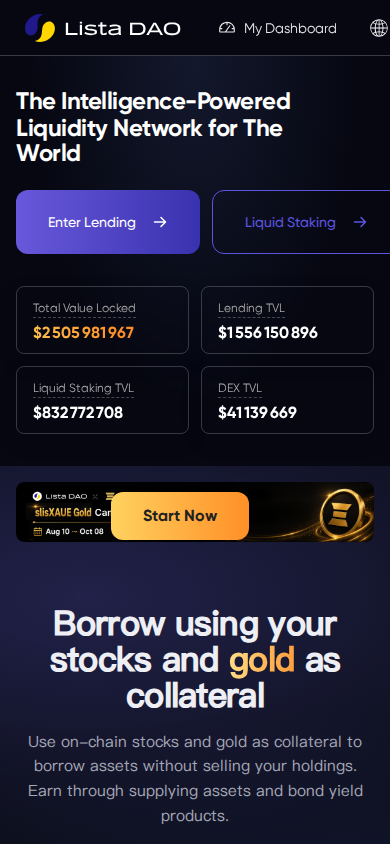
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
ListaDAO presents itself on its homepage as "a simple and permissionless liquid staking and CDP stablecoin lending protocol". The pitch is a decentralized-finance service where visitors can stake assets in exchange for liquid tokens and borrow a stablecoin against collateral. The page carries a large volume of text, but it was captured without any independent confirmation of who operates it.
Scam/Impersonation Risk
This site carries an elevated risk, and the contradictions are concrete. The domain is blacklisted: multiple threat-intelligence engines currently flag it as malicious or suspicious, including a tier-one security vendor, and the site also matches an external blacklist. The domain is only a few months old, which is a poor fit for a protocol that claims to manage staked assets and collateralised loans. It is also absent from the public DeFi protocol directory, so the site's claim to be an operating lending and staking protocol has no independent corroboration. No conflicting legal entities and no confirmed brand impersonation were observed. The concern comes from the external detections combined with the domain's youth and the type of service it advertises. The sandbox visits mitigate this somewhat: three of three sessions loaded cleanly and made no external network calls. They showed no wallet-draining behavior, no clipboard manipulation, no hidden forms and no content cloaking. That is a mitigating observation about the captured pages only, and it does not offset the active detections. Staking and lending sites are a common vehicle for fake front-ends that swap in malicious wallet-approval flows after a domain earns trust, and a fresh domain with live detections fits that profile. Evidence:
- Homepage: the site presents itself as a permissionless liquid staking and stablecoin lending protocol, which is a high-value financial use case.
- Domain registration: created 2026-05-03 (about 0.48 years old), with expiry set for 2027-05-03.
- Threat intelligence: three engines rate the domain malicious and two rate it suspicious, with a tier-one vendor among them. A separate external blacklist also lists it.
- DeFi directory check: the domain is not listed, so no recognised protocol or TVL figure corroborates it.
- Sandbox behavior: three runs completed with zero external requests, zero wallet-connection events and no cloaking.
Regulatory Verification Notes
Neither the page text nor the supplied evidence connects the site to a named legal entity, a regulator or a licensing authority. The registrant details are incomplete, so the operator behind the staking and stablecoin-lending claims is unidentified. Real-world identity could not be independently verified. No broker-reputation database entry was found for the domain, so there is no third-party reputational context either way. Recognised infrastructure is not a substitute for disclosed governance. The domain's age and the missing operator disclosure, together with the active detections, leave the site's financial claims unsupported by any visible accountability. Evidence:
- Domain registrar: NICENIC International Group Co., Limited. The registrant record is incomplete.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: TLS certificate issued by YE1 (DV, domain-validated only), valid to 2026-11-27 with about 31 days remaining. DV certification confirms control of the domain, not the identity of its operator.
- Homepage: no operator name, licence or registration reference was identified in the captured content.
What to Verify Next
Before any engagement, confirm through an independent route that this exact domain is the official address of any protocol it claims to be. Check the project's documentation or social channels as reached from a trusted source, not from links on this site. Search the DeFi protocol directories and on-chain explorers for the contract addresses the site asks users to interact with, and check whether the deployer is a known entity. Cross-check the domain against reputation and phishing-reporting services, and re-test after any claimed clean-up. Confirm official support and contact channels through an offline or independent route. If wallet approvals are requested anywhere, examine what permissions are being granted before signing, and prefer a read-only wallet or a fresh, empty wallet for any inspection. Evidence:
- Domain age of about six months means no long-standing public record exists to lean on, so independent confirmation is the only basis for trust.
- Active threat detections mean the domain must be re-checked against current reputation sources before any decision.
- The homepage names no operator or contract references, so those must be sourced from outside the site.
Summary Verdict
The overall posture is high-risk. The domain is actively flagged by multiple security sources and is very young. It also advertises a financial service whose operator cannot be tied to any real-world entity. Clean behavior in the captured sessions is the only point in the site's favor. It is outweighed by the external detections and does not establish legitimacy.
Infrastructure Integrity
The site is delivered through Cloudflare's CDN and WAF. Every observed address belongs to edge servers, and the origin host was not visible, so the underlying hosting cannot be independently checked. The certificate is valid and issued by a recognised authority. These are mitigating factors only. Edge-only visibility also makes it easier to change what the site serves without any visible change in hosting, and protective infrastructure cannot offset the external threat detections.
Closing Assessment
The site should be treated as unsafe for anything beyond passive reading. Wallet connections, token approvals, deposits, logins and any credential or financial interaction should be avoided until the domain is delisted and the operator is independently established.
Written analysis generated 2026-10-27 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, hosting and network, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered between three and six months ago.Hosting and network
rule:DNS_YOUNG_6M
03 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of listadao.app.
- The request stayed on listadao.app. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-05-03. Noted
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3033::ac43:9584 |
| Name servers | holly.ns.cloudflare.com, kyle.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-11-27 |
| Domain age | 0.48 years (continuous registration) |
| Domain expiry | 2027-05-03 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 3 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about listadao.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.