Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
register-bunnie-sol-xyz.pages.dev shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 12 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETServer in US | Noted |
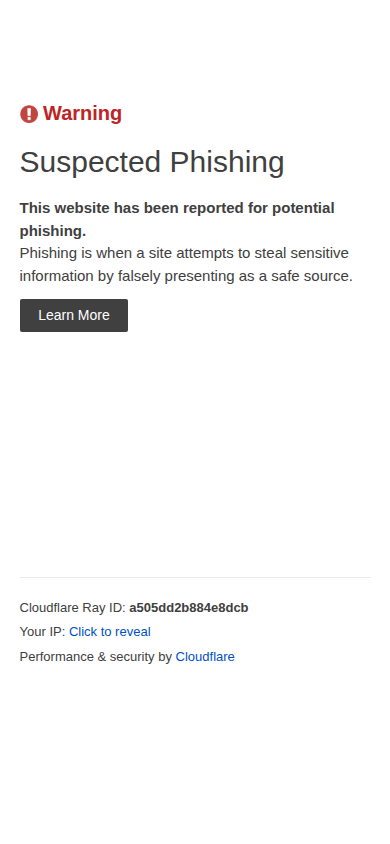
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website is a Solana-themed registration page. It is published on a free subdomain of a shared web-hosting platform rather than on a domain of its own, and its name suggests a sign-up or onboarding flow for a crypto-asset project. When analysed, the page presented only a very short body of text and was fronted by a security interstitial headed "Suspected Phishing", so the visitor is shown a warning instead of any recognisable product or service. Its apparent purpose is to collect registrations, and possibly wallet or credential interactions, from visitors drawn to a crypto-themed offer.
Scam/Impersonation Risk
Contradictory signals are present and decisive. Independent reputation sources currently list this site as malicious. These listings are strong enough to count as a confirmed blacklist and are not a soft reputational flag. Several leading security engines are among the detectors, and the hosting platform's own interstitial labels the page as suspected phishing. This fits the profile of a throwaway "register" page built on a free subdomain. Its name closely mirrors the hosting platform's own domain, and such pages are commonly used to bait crypto users into connecting wallets or entering credentials. No conflicting legal entities were observed, and no specific brand impersonation was confirmed. Neither fact offsets the active threat detections. The behavioural sandbox gives limited mitigating context. It observed no wallet-connection attempts, clipboard manipulation, hidden forms or credential posts to external hosts. The page nevertheless rebuilt itself heavily after interaction, and most of its network activity went to third-party destinations. A page that shows benign behaviour to an automated sandbox does not prove it is benign to a real visitor. Evidence:
- Homepage: twelve security engines flagged the domain as malicious and one as suspicious, including three leading vendors.
- Homepage: the page captured was a hosting-platform interstitial titled "Suspected Phishing", returned behind a bot challenge with an access-denied status.
- Homepage behaviour: 19 external data requests and 5 external POST submissions across three runs, with about 95% of peak network activity directed externally and 16 console errors.
- Homepage behaviour: the page content changed by over 99% after interaction, which indicates a highly dynamic interface.
Regulatory Verification Notes
No regulator, licence or registration record is connected to this site, and no third-party broker-reputation entry matches it. That is a verification gap, not a finding in its own right. The real-world operator is not independently identified. The free shared subdomain gives no registered domain of its own to link the page to a company or individual. For a site that appears to invite registration in a crypto context, the lack of a verifiable operator is material given the active threat listings. The site's own legal, terms and privacy content could not be reviewed. The transport-security posture is routine and does not speak to legitimacy: a valid but low-assurance certificate is easily obtained by any operator, including malicious ones. Evidence:
- Site-wide: no licence, registry entry or company registration is attached to the site, and no broker-reputation record matches it.
- Transport encryption: TLS certificate issued by WE1 with domain-validation (DV) only, valid to 2027-01-16.
- Hosting infrastructure: served from AS13335 (Cloudflare, Inc., US).
What to Verify Next
Any project or token that this page claims to represent should be confirmed through its officially published channels, reached independently of this site, before any registration is attempted. A wallet that has already interacted with the page should have its connected-site permissions and token approvals reviewed and revoked. A visitor who entered credentials should change them and enable multi-factor authentication. The page can be reported to the hosting platform's abuse desk, and the site should be re-checked only after the platform or the owner confirms it has been cleaned or removed. Evidence:
- Homepage: the registration theme and Solana-style naming indicate a likely wallet or credential interaction path.
- Homepage: the platform's own phishing interstitial supports reporting the page to the host.
- Site-wide: no independent operator identity was found to confirm the site against.
Summary Verdict
The site is assessed at critical risk. Confirmed external threat listings, a platform-level phishing warning and the absence of any verifiable operator together outweigh its routine technical hygiene. The evidence supports a clearly cautionary, high-risk posture. Its legitimacy cannot be established, and it should be treated as a probable credential- or wallet-harvesting page.
Infrastructure Integrity
The site is served entirely through Cloudflare's CDN and web-application firewall. All four observed addresses, both IPv4 and IPv6, are edge servers, and the origin host was not observable. The protection is a mitigating technical factor only. It shows that the platform is reputable and that the page was delivered with a valid certificate. It does not make the content hosted behind it trustworthy, and it cannot offset the active reputation findings.
Closing Assessment
The site should not be used for login, registration, wallet connection or any financial interaction. If it is opened at all, it should be viewed read-only from an isolated browser profile, and nothing should be downloaded from it.
Written analysis generated 2026-10-26 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH - The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
03 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of register-bunnie-sol-xyz.pages.dev.
- The request stayed on register-bunnie-sol-xyz.pages.dev. It was not redirected to another domain. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2cb3 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-16 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 12 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about register-bunnie-sol-xyz.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.